Agregátor RSS
FUJITSU-MONAKA CPU a Fujitsu MONAKA Server
Společnost Fujitsu představila FUJITSU-MONAKA CPU a Fujitsu MONAKA Server. Navrženo, vyvinuto a vyrobeno v Japonsku. Pro suverénní AI infrastrukturu.
Kategorie: GNU/Linux & BSD
Googlebooky jsou za rohem. Google vyrazí proti Windows a macOS s upraveným Androidem
Google oznámil, že již 21. září v 15:00 našeho času spustí předobjednávky Googlebooků. Firma s nimi chce vstoupit do třídy prémiových notebooků, které nabídnou vyšší výkon, lepší výbavu a nové softwarové funkce oproti dosavadním Chromebookům. Běží také na jiném operačním systému.
Zatímco ...
Kategorie: IT News
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere else on the host, Docker warns in a security announcement on September 15.
The escape runs with the rights of the host account that runs the virtual machine. The flaw, CVE-2026-77179, is rated Critical, affects versions Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
London property manager breach may have exposed bank details and lockbox codes
London property management biz City Relay has warned customers that intruders may have stolen financial data, passwords, and codes used to access keys after compromising its Metabase Cloud instance. City Relay, marketing itself as "London's most trusted property management company," told landlords via email - seen by The Reg - that attackers accessed the third-party provided cloud twice "as a result of a vulnerability in the platform that we were unaware of." The message to customers stated: "Personal data was extracted from the platform." The potentially compromised data on the platform includes names, email and physical addresses, telephone numbers, financial information, property access details, and account passwords. City Relay said the exposed financial data included bank account numbers, sort codes, IBANs, SWIFT references, and account names and addresses. Attackers may also have obtained data about property amenities and access, including the locations of stored keys and codes for lockboxes containing them. Dray Agha, senior manager of security operations at Huntress, explained that Metabase connects to customers' databases, so the information exposed in an attack depends on the access each customer granted it. "A company linking Metabase to a general analytics database will only expose harmless user metrics," he said. "A company that connects it directly to their core transactional database risks exposing highly sensitive financial records and credentials." Agha said that if the exposed passwords and financial details were stored in readable form, that would point to inadequate data protection practices. "Sensitive financial details should also be encrypted or tokenized when held in a database. Keeping this information readable creates a massive risk if a connected reporting tool is ever compromised." The Register understands that City Relay sent the emails to current landlords and former users of its services. One source claimed City Relay learned of the intrusion on September 8 and notified affected customers on September 14. "As property access and key-storage information was potentially included, we immediately took precautionary action to update the relevant access and key-storage codes," the emails stated. "This work has now been completed. The previously exposed codes can no longer be used and we have no evidence of any unauthorised property access arising from the incident." Beyond the immediate physical security risks, City Relay urged customers to check their bank accounts for suspicious transactions, watch for phishing and other scams, and change any reused passwords on other accounts. The company told us it had found no evidence that the exposed data had been misused. It is continuing to investigate alongside cybersecurity specialists and "the relevant authorities" to establish the attack's full scope. City Relay's website says it has hundreds of "partners" – landlords who outsource management of their property portfolios – and that it manages, or has managed, thousands of London properties. The company has not said how many customers were affected in London or Paris, where it also operates. The Register asked City Relay for more information. City Relay did not identify the vulnerability used in the attack. Metabase disclosed a zero-day SQL injection flaw on August 6, saying attackers compromised fewer than 3 percent of its customers before fixes were automatically deployed, but it has not confirmed that the City Relay incident was part of that campaign. Known victims included laptop maker Framework and workflow automation platform n8n. ®
Kategorie: Viry a Červi
Předprodej notebooků Googlebook spuštěn v pondělí 21. září
Předprodej v květnu představených notebooků Googlebook, nástupců notebooků Chromebook, bude spuštěn v pondělí 21. září.
Kategorie: GNU/Linux & BSD
DJI Osmo 360 II je vlajková akční kamera. Má čtvercový snímač, vyměnitelné objektivy a šílené parametry
Kategorie: IT News
Anthropic tries to make Claude stickier with launch of Docs and Slides
Anthropic is equipping its Claude AI assistant for more productivity work with the launch of Claude Docs and Slides.
While it’s already possible to create documents such as Microsoft Word and Google Docs files from Claude chats, the latest update, announced Wednesday, brings a rich-text editor directly into Claude.
Users ask the AI assistant to draft a document or slides via the chat interface, and Claude will ask clarifying questions before starting work. It will also leave comments to explain its choices.
Claude Docs files are then stored in the Artifacts tab and can be exported as Word, PDF, Google Docs, or markdown files. Documents can be shared with colleagues for real-time collaboration.
Anthropic
“Strategically, this signals Claude moving from an AI assistant into an agentic platform meant for full lifecycle of knowledge work,” said Arun Chandrasekaran, Distinguished VP analyst at Gartner.
He anticipates early user demand around “recurring, template-driven work,” such as status reports, board decks, and data-to-story reports.
“The likely near-term outcome isn’t wholesale replacement of alternative digital workplace tools, but it positions Anthropic as an entry point for workflows historically created in third-party tools,” said Chandrasekaran.
Claude Docs usage counts towards a customer’s Claude usage limits, and larger requests such as drafting a document with several sources takes up more of the limit. There are currently feature limitations, with no version history, access levels, or external sharing on Team and Enterprise pans. It’s also unavailable for customers that use “customer-managed encryption keys (CMEK), zero data retention (ZDR), or a HIPAA-ready configuration,” according to Claude’s support site.
Claude Docs and Slides are available in beta now on paid plans, rolling out to Pro and Max plans first. The feature is turned off by default for enterprise plans.
Anthropic
All of the major AI model providers are seeking ways to make their products stickier within customer organizations, said Jack Gold, principal analyst at J. Gold Associates. Some have targeted coding agents, while others, particularly Microsoft and Google, have AI assistants and agents that are connected into existing office productivity tools.
Microsoft’s Copilot is embedded across its Office suite, for instance, although users can also create documents directly from the Microsoft 365 Copilot chat interface.
“Microsoft and Google are bringing AI deeper into established productivity environments, while Anthropic is bringing more of the productivity environment into AI,” said Maria Bell, senior research analyst at FDM CCS Insight. “Over time, the competition may increasingly be over which becomes the primary interface through which knowledge workers get work done.”
Early findings of FDM CCS Insight’s ‘2026 Employee Workplace Technology Survey’ show that show that around half of employees that use generative AI at work do so to create or edit reports and documents.
It’s unlikely that native document editing features in Claude will result in a large-scale move from Microsoft or Google’s productivity suites, analysts say.
The updates to Claude this week have the potential to help users get more done, said Gold, “but it’s unclear how many users that already have productivity suites in place will choose to move to other tools,” even if they prefer Claude for its AI capabilities.
“The fundamental question is, if I am used to certain tools and they work for me, am I willing to change for the promise of working better? Not sure that will be a winning strategy,” he said.
“Microsoft and Google are deeply embedded in how people already work, and users have spent years becoming comfortable with their products and workflows,” said Bell.
“They are also increasingly bringing access to powerful AI models directly into those familiar environments. Anthropic therefore must do more than match document-creation features; it has to offer an experience compelling enough for users to build new habits around Claude,” she said.
As well as Anthropic’s Claude, it has long been rumored that OpenAI plans to build its own native productivity tools in ChatGPT that would bring it into more direct competition with Microsoft and other incumbent office software vendors.
Anthropic also announced that users can now invoke Claude Design in an ordinary chat. Claude Design, which generates visual outputs such as slides and prototypes, was previously available as a separate tool within the Claude app.
In addition, Claude Cowork — which can perform multiple-stage tasks — and the regular Claude chat interface have now been combined, with Claude determining how to handle a request. This removes the need for users to decide which tool to use for a particular task, according to Anthropic. It’s not clear exactly how Anthropic decides where to route a request, however. Cowork queries are generally more token-intensive than the core chat interface.
“Claude can now figure out what a task needs, so what Cowork and Design can do is available from any conversation, with the context, skills, and connectors you already have,” the company said in a blog post.
The new Claude experience will roll out gradually, starting with Pro and Max customers. Anthropic said it will alert Claude Enterprise customers before any changes are made to their account.
Claude Enterprise costs $20 per user each month alongside consumption-based pricing.
Kategorie: Hacking & Security
Těhotná želvuška, hojící se rána a divoké bitvy pestřenek. Nikon vyhlásil nejlepší videa z mikroskopů za rok 2026
Nikon každý rok vybírá ty nejkrásnější fotografie z optických mikroskopů. Mezinárodní soutěž Small World, do které přispívají vědecké týmy z celého světa, se bez přestávky koná už od roku 1975 a od sezóny 2011 ji doplnila i druhá kategorie Small World in Motion.
Jak už název napovídá, tentokrát ...
Kategorie: IT News
Will Apple enter the server business?
In a world of speculation, this week’s most interesting rumor says Apple may plan to enter the server business once again, with powerful systems running its own Apple Silicon chips.
It’s hard to dismiss the claims, particularly as Apple is already in the server business, with its Texas factory manufacturing servers for its Private Cloud Compute (PCC) cloud intelligence system. While those servers are only used internally —or externally if installed at third-party data centers for use with Apple’s ecosystem of products — they are still servers.
Apple is already in the server businessIt’s also a business Apple has been in before. Many years ago, around 2002, I visited Apple in Paris, where the company demonstrated its Xserve and Xserve RAID systems. These were particularly aimed at the video and music industries and became quite widely used in those sectors. Apple discontinued Xserve in 2011, because the product sat outside its broad consumer-focused strategy.
Things were different then. You see, today’s Apple has billions of users. It has a fast-growing reach into enterprise tech — SAP recently updated its fleet of 60,000 Macs to macOS 27 on the very day the OS shipped, and there are hundreds of thousands of Macs in use at businesses worldwide. Apple has hundreds of millions of iPhones in active use across business. Apple even has the silicon to power these things.
The Apple Silicon advantageYou can’t ignore the computational advantage of Apple Silicon. The first leaked benchmarks for the M5 Ultra chip used in the new Mac Studio are incredibly impressive, with multi-core performance at an astonishing 52,516. That’s amazing performance from a Mac that costs an estimated 8 cents an hour to run at full capacity.
Now imagine that price/performance ratio stashed in a server.
You don’t even need to imagine it, because MacStadium, AWS, and others already use Macs in server farms, with great success. MacStadium CTO Chris Chapman once told me that Apple Silicon is so power efficient his data centers would tell him the Macs he had racked with them were not using enough power for the space. (Data centers sell space by the square foot and calculate energy costs within that calculation.)
Making cloud cheaper and more secureThe computational performance per watt is an advantage to any user, but the cost benefits rack up pretty fast when you have a thousand machines racked up on the data farm. Apple even has a server operating system waiting in the wings — or did until it stopped offering macOS Server four years ago.
Apple’s existing server production is focused on Private Cloud Compute. That system is impressive, (a) because Apple has opened it up to security experts to confirm it is secure, and (b) because it delivers data and privacy security equal to what its end-user platforms provide.
But, as data centers blossom across Terra Firma, there’s a growing recognition of the need for sovereign AI, on-premises AI, and private AI. Think of it this way: We already know Macs can run some of the world’s most powerful LLMs very, very well. What’s wrong with introducing Apple Silicon-based servers to do the same thing? These things could even offer companies access to their own white-label private builds of Apple Intelligence, though I consider that unlikely.
Why the speculation makes sense, and why it doesn’tSo, I see lots of reasons why speculation that Apple may re-enter the server market makes sense — though it may not be in a huge hurry, as the original claim is that these servers will run M8 Ultra chips. (Mark Gurman thinks it may be an M7 Ultra).
Of course, speculation and conversation don’t always become fact. Merely because Apple is talking about servers again doesn’t mean it will advance those plans.
Former Apple business-focused product marketing executive Todd Dailey doubts these plans. He says Apple is far more focused on consumer markets than enterprise.
He also points out that if it were to offer servers, the company would need to consider providing same-day tech support and more flexibility around OS upgrades, adding that the business may not be big enough to justify the cost of implementing the plan.
That doesn’t mean Apple isn’t considering it, just that once you bounce the idea through a few real-world weeds there may be obstacles to making it happen.
Is it time for iCloud Ultra?I do think there are signs Apple is taking enterprise markets more seriously. I also think that as PCC deployment expands, it makes sense for Apple’s server teams to build a product road map for the future of PCC servers like any other Apple product, even if they are only used to support its own server-side AI.
But I also think that if the company were to go ahead to make this happen, the solution would be aimed at developers and businesses seeking a uniquely private way to deploy sophisticated AI outside of the thrall of the frontier models, chipping a little more business away from those over-leveraged entities as it does.
The thing is, if that’s the case, then is it servers Apple is thinking of building, or server farms offering hosted services for a price? An iCloud Ultra service for developers and enterprise users may perhaps make more sense. I guess we’ll have to wait and see.
Now please subscribe to my daily, human-curated Apple-related news headline feed at The Core, or follow me on BlueSky, LinkedIn, or Mastodon.
Kategorie: Hacking & Security
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE.
"HEAVYGRAM offers builtin commands supporting remote command execution, system, network and process information discovery, data and Telegram session files exfiltration, screenshot capture, DLL sideloading, Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
What Recent AI-Powered Attacks Mean for Your Identity Security
AI is making credential theft faster and easier to scale, giving attackers more opportunities to abuse valid identities. Specops explains why identity security must go beyond successful authentication by verifying that both the user and the device requesting access can be trusted. [...]
Kategorie: Hacking & Security
Windows 11 24H2 Home and Pro reach end of support in October
Microsoft reminded customers this week that devices running Windows 11 24H2 Home and Pro editions will stop receiving updates next month. [...]
Kategorie: Hacking & Security
The Odyssey and trojans again: MovieReaper attacks users in multiple countries via compromised torrents
Introduction
Torrent trackers have long been abused for distributing malicious software, disguised as popular films, games, and other content. Our previous research has shown that cybercriminals repeatedly turn torrents as an initial infection vector, using trojanized cracks and installers to reach a large number of users. Installation guides for pirated software routinely instruct users to disable their antivirus, conditioning them to ignore potential threats they are inviting onto their computers.
During our analysis of malware that leverages blockchain networks for its C2 infrastructure, we have discovered a previously unknown modular, multi-stage framework that we dubbed MovieReaper. This report details the new crimeware campaign that began with the mass infection of users via compromised torrent tracker file storage. We have identified several hundred victims, including both individual users and organizations in a multitude of countries, such as Russia, Türkiye, Japan, Kenya, Uganda, and Colombia, as well as in several European countries like Spain, the Netherlands, Belgium, Germany. We analyze the techniques used to evade detection by security and sandbox solutions, examine the capabilities of the modular framework.
Kaspersky products detect this threat as HEUR:Trojan.Win64.Agent.gen.
Technical Details BackgroundIn mid‑August 2026, during our threat‑hunting efforts, we identified a large‑scale infection campaign involving previously unknown malware disguised as popular movies. The campaign affected both individuals and organizations across multiple countries. Our initial analysis revealed a common factor among the victims: all had used torrent trackers. This finding prompted us to investigate the campaign further and analyze its distribution mechanism, overall scope, and unknown malware implants.
Initial infection and spreadingCompromised torrent trackers are the primary vector used to distribute malware. During our investigation, we identified multiple user reports describing suspicious files being downloaded instead of the intended content.
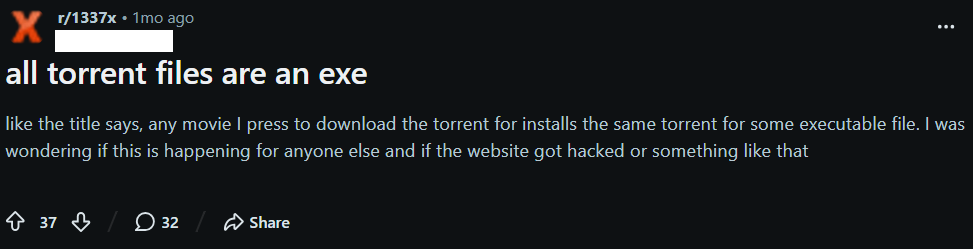
For example, a user of a popular movie torrent tracker reported the following case on Reddit:
Further analysis of the attack revealed that the threat actors did not compromise the torrent trackers themselves. Instead, they compromised a widely used public repository of torrent files — itorrents[.]org. As a result, torrent trackers that relied on this repository began inadvertently distributing malicious torrent files to their users. This approach is particularly powerful because the threat actors can reach users of multiple tracчkers without compromising each platform individually.
As of the publication date of this report, the archive remains compromised. When a user attempts to download a torrent using a magnet link, the legitimate torrent archive instead returns a different torrent file. This malicious torrent leads to the download of the malware loader. It is used to deploy a framework that we dubbed MovieReaper.
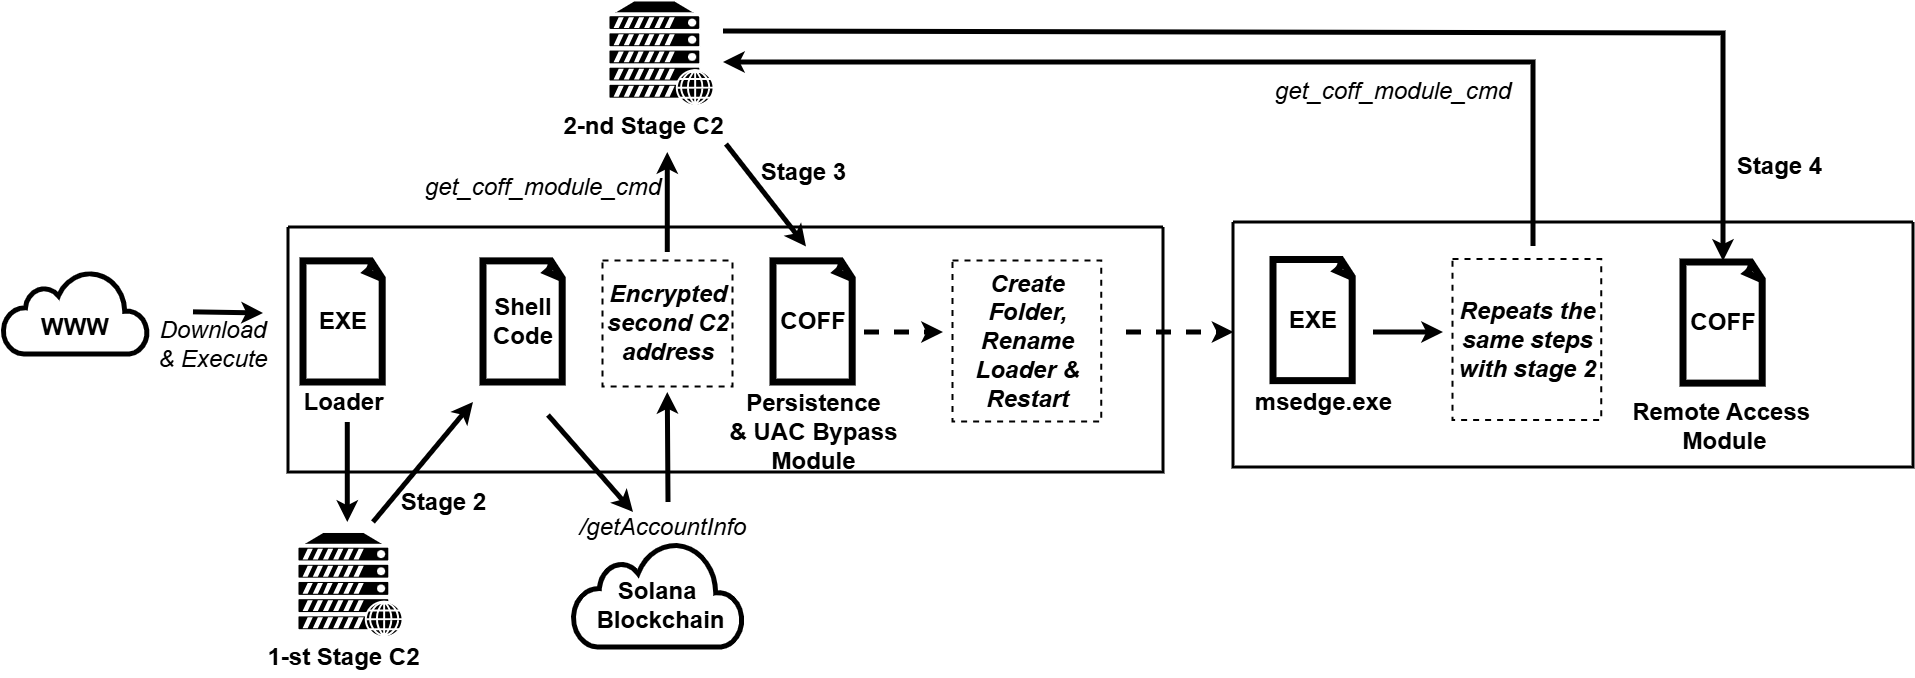
The loader initiates the infection chain, which is illustrated in the diagram below. Each stage of the infection chain is described in detail in the following sections.
Malware implantsThe infection chain consists of several steps, where only the initial one is dropped on the disk before its execution to avoid detection. The malware itself is not heavily obfuscated, apart from the fact that strings are encrypted with a custom stream cipher. Most of the countermeasures were aimed at avoiding detection by AV sandboxes.
Step 1: LoaderThe most popular initial executable was distributed through torrent trackers under many different names (for example, the odyssey (2026) [1080p] [webrip] [5.1].exe), but the file hash (MD5: A0B13781EDD7CFDAB13D79AFFF3C83C1) was identical across all downloads. We have seen multiple different loaders, where the executable file disguises itself with a long filename and an icon of some well-known application. Most of the filenames are rather large, presumably, to hide the “.exe” extension at the end.
After the user manually starts the application, it establishes a global mutex to ensure that only one loader is executed at a time. We have seen several variations of a mutex in our samples, which contain a randomly generated string (in example Global\fnulSktzSqvVLXHU). Then this executable performs the series of operations in order to avoid detection by the AV sandbox solutions.
While performing those operations, the malware avoids making LoadLibrary and GetProcAddress calls in order to acquire addresses of required functions. Instead, it searches for loaded libraries by traversing the double-linked list taken from the Ldr field of PEB and then performs manual parsing of loaded DLL to calculate the address of function.
After all the initial checks have passed, this binary prepares to perform network connection to a C2 web-server to download the shellcode, map it into the RWX memory and execute. While doing it, loader decodes https://deadhub[.]org domain name and if connection to it has failed, then it uses the IP address http://193.23.118[.]155 as a fallback and connects to it using plain HTTP. Malware chooses a random group of strings and uses them as a path in the HTTP request to download parts of a shellcode.
Example URLs:
/cloud/v192.4/ui/sync-status-icons.png
/cloud/v192.4/onboarding/welcome-bg.jpg
/cloud/v192.4/ui/file-preview-placeholder.png
/cloud/v192.4/shared/link-banner.jpg
While mapping the address space and executing the shellcode, the loader registers a vectored exception handler and rewrites the handler address in memory in order to perform a debug break, which will not crash the program, but instead redirect control-flow into the function that actually makes raw NtProtectVirtualMemory syscall (via previously located “0x0F 0x05” syscall instruction inside ntdll). Then it calls an undocumented ntdll function EtwpCreateEtwThread, which is a popular alternative to a CreateThread to perform code execution and executes the shellcode.
Step 2: ShellcodeThe second stage of this malware performs an HTTPS request to the Solana blockchain at the /getAccountInfo endpoint for the 6pnDGAiHgyPdmckM5Qt1YbanGzrX43WLEU159nRaNLDm account. The data field of the response contains the base64‑encoded address of a second C2, which is encrypted with a static XOR key located within the shellcode itself. To store data in this account, attackers used a simple Solana program (address: CSiY8bQLBYPdfPWkwipBzH6sijTVQVVsA279JQdvwHtL).
By using Solana blockchain network as a distribution layer of endpoints for a next stage attackers may increase stability of their campaign and resist takedown efforts of defenders.
The second stage payload communicates with its C2 server strictly through HTTPS via TLS-pinned certificate using nanopb protobuf library as a container for transferred data. The main logic of stage 2 implant contains several initial commands, where the most important is the one that parses the COFF file and loads it to the memory, and executes the module_init function from it. It provides a convenient interface for extension of the command list, which leads us to the next stage of the payload.
Step 3: UAC Bypass and persistenceNotably, the recovered modules were compiled with symbols, which accelerated reverse engineering.
After receiving the next stage from the second C2 server, the newly loaded module performs several tasks right in the module_init function.
Stage 3 performs UAC Bypass and achieves persistence using public techniques, masquerades the original binary as C:\ProgramData\Microsoft\Windows\Telemetry\msedge.exe, and restarts itself.
The respawned process starts with the initial loader, but with a special command-line argument, which allows it to skip most of the anti-sandboxing checks and proceed straight to the download of the stage 2. The executable proceeds with the same steps as before, but this time, instead of downloading persistence and UAC bypass module, the new one is downloaded from the second C2 server, because there is a flag being sent to a remote server that indicates whether the implant is running from the Telemetry folder is sent in the beacon, allowing the C2 to distinguish first-run and respawned instances.
Step 4: The final implantThe final module (“file manager”) exposes 21 commands that give the operator filesystem access on the victim host. It allows remote operator to download, upload, read files on the system, list and enumerate directories, manipulate files using create, copy, rename, move, delete, chmod, symlink commands, use preview and thumbnail commands to exfiltrate previews of images and files before actually extracting them.
We suspect that other modules may be loaded on-demand by the request of the operator.
InfrastructureDuring this malware campaign, attackers use various commercial hosting providers for their C2 infrastructure (see IoC section for details). Furthermore, as noted above, the campaign leverages the legitimate Solana blockchain via the api.mainnet.solana.com RPC endpoint to deliver the address of the second‑stage C2 server to the malware. This approach provides the attackers with decentralized storage for C2 addresses, adding an additional layer of resilience and making it more difficult for defenders to disrupt the campaign by simply blocking the IP addresses of the C2 servers.
VictimsThe observed campaign targeted both individuals and organizations across Europe, Asia, and Africa, with infection attempts identified in countries including Russia, Spain, Germany, Finland, Türkiye, Japan, Nepal, Kenya, Tanzania, Ghana, and others. The targeted organizations span a wide range of sectors, including enterprise, government, IT, consulting, retail, transportation, and agriculture.
ConclusionsOur research uncovered activity of the same actor, dating back to October 2025. The campaign has evolved over time with the malware authors expanding their arsenal, making the loader harder to detect, although the pattern remains the same: encoded strings, parts of shellcode are downloaded through the plain HTTP protocol, several techniques are used to avoid sandboxes and virtual machines. We will continue monitoring this actor’s activity to catch new potential threats.
The first stage offers the clearest opportunity to disrupt this campaign, as it relies on a single specific domain name and a single IP address to serve the shellcode, meaning that taking down this server would prevent the infection chain further. This includes the second-stage payload, which uses the Solana blockchain network for C2 and is, therefore, more resistant to conventional infrastructure takedowns.
However, this framework’s self-containment, modularity and in-memory execution has its potential to be reused in later campaigns with minimal rework.
Indicators of compromise File hashes4334BBAEA8DE33BF9D45E9B4E4E3BC2
4843F9FAFCAE492F11E2D4D33DBB4CDD
5310CABAE3FBE6DB8742849B588093F9
A0B13781EDD7CFDAB13D79AFFF3C83C1
70060341CAF3338697A7DDFE0FB62875
AD4643EEA15AC286FA47D1131F9EF756
D0B967571AC8A3863C7F324BF5BDE99C
D88D550D0FB8E60CFFFF3EA61FF7A067
%ProgramData%\Microsoft\Windows\Telemetry\msedge.exe
MutexesGlobal\E4AyDKzvEhe2hgAr
Global\fnulSktzSqvVLXHU
First-stage C2:
deadhub[.]org
193.23.118[.]155
Second-stage C2:
208.64.33[.]90
208.94.246[.]53
Kategorie: Hacking & Security, Viry a Červi
Srovnávací test tiskáren na fotky – tentokrát bez pořadí, každá je úplně jiná. A někdy se vyplatí prostě zajít do fotolabu...
Mobil máme plný tisíců snímků, ale k většině z nich se už nikdy nevrátíme. Fotografie na papíře má i v době cloudových galerií svoje kouzlo. A vytisknout si ji doma je jednodušší než kdy dřív. Jen to vyžaduje vybrat správnou tiskárnu – jinou potřebuje ten, kdo vytiskne deset fotek za rok, a jinou ...
Kategorie: IT News
Cisco drops another exploited zero-day, this time a perfect 10
Cisco admins who have spent their week patching email gateways now face a perfect-10 Identity Services Engine flaw under active attack. Cisco disclosed CVE-2026-76460 on Wednesday, describing it as an authentication bypass affecting Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC). Successful exploitation can give an unauthenticated remote attacker command execution with root privileges. Product Security Incident Response Team said it was aware of active exploitation and urged customers to install the fixes immediately. CISA has also added the vulnerability to its Known Exploited Vulnerabilities catalog. The warning follows another actively exploited critical vulnerability disclosed days earlier, CVE-2026-76461, affecting its Secure Email Gateway and Secure Email and Web Manager appliances. That 9.8-rated bug could also lead to root access, prompting Cisco to warn admins that attackers may be able to cover their tracks after getting in. The latest problem lies in an API within Cisco ISE, the company's network access control platform. Cisco says insufficient authentication controls on an API endpoint mean an attacker can send a crafted request to bypass the product's web-based management interface. No credentials or user interaction are required, and Cisco says vulnerable versions of ISE and ISE-PIC are affected regardless of configuration. The flaw received the maximum CVSS score of 10.0. Cisco warned that root access could allow attackers to remove or conceal traces of an intrusion, complicating efforts to determine whether an appliance had been breached. Cisco advised admins to review ISE access logs for suspicious usernames on every node in a distributed deployment and to check network and firewall logs held outside the affected device for signs of unexpected uploads or downloads. If admins find evidence of possible exploitation, Cisco "strongly recommends" reimaging affected nodes and restoring their configurations from backup if necessary. No workaround exists, although Cisco said infrastructure access control lists can be used as a temporary mitigation to restrict management and control-plane traffic reaching affected systems. Permanent fixes are available in ISE and ISE-PIC 3.1 Patch 12, 3.2 Patch 11, 3.3 Patch 12, 3.4 Patch 7 and 3.5 Patch 4. ISE 3.0 has reached the end of software maintenance, so customers running it must migrate to a supported release. Cisco discovered CVE-2026-76460 while resolving a Technical Assistance Center support case, but has not disclosed who is exploiting it, how long the attacks have been underway, or what the intruders have done after gaining access. The advisory accompanied a substantial batch of other ISE vulnerabilities published Wednesday. Two other Cisco advisories carried maximum CVSS scores of 10.0, while a separate trio of remote code execution flaws scored as high as 9.9. For admins responsible for Cisco kit, September is shaping up to be quite the patching month. ®
Kategorie: Viry a Červi
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday.
An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution.
Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2026-81642, along withSwati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Druhý blok jaderné elektrárny Temelín se zastavil. Za vše mohla vadná karta
Druhý temelínský blok museli energetici neplánovaně odpojit kvůli poruše elektroniky • Závadu v řídicím systému vyřešila celkem rychlá výměna vadné karty • Plný provoz zařízení odborníci obnoví pravděpodobně již během dnešního dne
Kategorie: IT News
Co se teď nejvíc hraje na Nintendu Switch. Nejoblíbenější hry pro starou i novou konzoli
Hybridní konzole od Nintenda fungují dál bok po boku. I když stále víc prostoru dostává Switch 2, ani jeho předchůdce bychom neházeli do starého železa. Nejhranější jsou hlavně oddechovky a exkluzivity, ale daří se i větším multiplatformním titulům.
Kategorie: IT News
US takes down NightmareStresser DDoS-for-hire platform
The U.S. Federal Bureau of Investigation (FBI) seized the domains used by NightmareStresser, one of the world's longest-running distributed denial-of-service (DDoS) platforms. [...]
Kategorie: Hacking & Security
Test environment let anyone access live customer data
Welcome back to PWNED, the weekly column where we learn important life lessons about how we let cybercrims access our data through carelessness. Hopefully, others’ mistakes provide an example of what not to do. Today’s tales of woe comes courtesy of Richard Schut, Managing Director & AI Software Researcher at SmartRepl, a company that offers business AI services such as AI receptionists and sales automation. In a past job, Schut was working for what he describes as a mid-size company during a security audit whose purpose was to identify any potential problems ahead of moving some local systems to the cloud. Schut and his team discovered that there was a test environment that was accessible outside the network and connected to a database which had live customer information in it. This was a gaping hole that a miscreant could have used to grab valuable information from the business. “What made the situation particularly concerning was that the environment had originally been created for what the development team considered a short-term purpose,” he told The Register. “They needed somewhere to demonstrate the application and test the migration, so a staging instance was spun up quickly. It was never intended to become part of the company's permanent infrastructure.” Unfortunately, the test environment was still running months after it was initially set up. And because those who created it did not expect unauthorized people to access it, they didn’t use the same authentication and access control methods that they would in production. The SQL file containing the database was appropriately named master_test_final.sql, just in case there was any question about what it contained. “It was a classic example of how security problems don't always come from sophisticated attacks or exotic vulnerabilities,” Schut said. “Sometimes the biggest risk is simply something that was supposed to exist for a few hours, but was still sitting there six months later.” After Schut and his colleagues discovered the security vulnerability, he immediately restricted access to the staging environment. Then he and his team started a review of other development and test environments in the company to make sure none of them was open to exploitation. The takeaway here is as accessible as that SQL file: Don't get lax with security simply because an environment is made for testing. Even if the test server was live for only a day, that’s a day where it could be exploited. “The incident completely changed how I look at staging environments. If an environment has access to real data, it needs to be treated as a real security asset — regardless of whether the developers expect it to exist for a day, a week, or six months,” Schut said.®
Kategorie: Viry a Červi
- « první
- ‹ předchozí
- …
- 3
- 4
- 5
- 6
- 7
- 8
- 9
- 10
- 11
- …
- následující ›
- poslední »