Agregátor RSS
CISA Red Team Compromised Two Critical Infrastructure Orgs, One Detected Nothing
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has published the results of two red team assessments it conducted simultaneously against two critical infrastructure organizations, using what it described as similar tradecraft while recording sharply different defensive outcomes.
Both organizations were fully compromised at the domain level, and in both, the red team also Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Armbian 26.8
Armbian, tj. linuxová distribuce založená na Debianu a Ubuntu optimalizovaná pro jednodeskové počítače na platformě ARM a RISC-V, ke stažení ale také pro Intel a AMD, byl vydán ve verzi 26.8. Přehled novinek v poznámkách k vydání.
Kategorie: GNU/Linux & BSD
ChatGPT už umí generovat obrázky s průhledným pozadím nebo jej odstraňovat z fotek
Společnost OpenAI minulý týden oznámila, že vylepšila obrazový model GPT-Image-2, takže už dokáže generovat plně průhledná pozadí. Novinka je dostupná prostřednictvím API, ale zamířila také do chatbotu.
ChatGPT uměl generovat průhledné obrázky i v minulosti, ale nebylo to moc spolehlivé. Výsledkem ...
Kategorie: IT News
Microsoft tests new privacy controls for Windows 11 desktop apps
Microsoft has begun testing new privacy controls that will let Windows 11 users choose which desktop applications can access their camera, microphone, and precise location. [...]
Kategorie: Hacking & Security
Unpatched Kaltura mwEmbed Flaws Could Let Remote Attackers Read Files and Run Code
The CERT Coordination Center (CERT/CC) has disclosed two unpatched vulnerabilities in Kaltura's HTML5 video player library that allow a remote, unauthenticated attacker to read arbitrary files from a server and execute code on it.
The flaws, tracked as CVE-2026-19913 and CVE-2026-19912, both stem from the same unsafe deserialization in the mwEmbedLoader.php endpoint of the mwEmbed player
Kategorie: Hacking & Security
Unpatched Kaltura mwEmbed Flaws Could Let Remote Attackers Read Files and Run Code
The CERT Coordination Center (CERT/CC) has disclosed two unpatched vulnerabilities in Kaltura's HTML5 video player library that allow a remote, unauthenticated attacker to read arbitrary files from a server and execute code on it.
The flaws, tracked as CVE-2026-19913 and CVE-2026-19912, both stem from the same unsafe deserialization in the mwEmbedLoader.php endpoint of the mwEmbed player Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Koupili jste si Zaklínače 3? V září dostanete zdarma remaster s lepší grafikou i hratelností
Kategorie: IT News
Imagine the SOC Without a Queue: From Alert Backlog to AI Hypothesis Engine
The SOC we've always known was built around a model that guarantees most of the alert queue will never receive analyst review. There's never time. In a traditional SOC, the typical progression follows a well-known pattern: an alert arrives; a detection engine assigns a severity score. The issue then waits for a human to decide if it should escalate to an investigation.
Given the volume of
Kategorie: Hacking & Security
Imagine the SOC Without a Queue: From Alert Backlog to AI Hypothesis Engine
The SOC we've always known was built around a model that guarantees most of the alert queue will never receive analyst review. There's never time. In a traditional SOC, the typical progression follows a well-known pattern: an alert arrives; a detection engine assigns a severity score. The issue then waits for a human to decide if it should escalate to an investigation.
Given the volume of [email protected]
Kategorie: Hacking & Security
If OpenAI has nothing to hide, it has nothing to fear
Apple has filed a motion demanding expedited discovery in its trade secrets litigation against OpenAI.
The lawsuit alleges that OpenAI and some former Apple employees now at the AI firm deliberately worked to exfiltrate valuable trade secrets from Apple. The initial allegations describe a series of serious attempts to grab this information, including one claim that OpenAI attempted to get a partner manufacturer to demonstrate proprietary Apple manufacturing process technology. Apple argues that this information is not free, belongs to Apple, and reflects decades of effort in building the tech.
OpenAI’s counter arguments so far have been easy to paraphrase; it’s claimed that if Apple hadn’t wanted its secrets to slip, it would have put more security in place to protect them.
The company has also said it is making something completely new, so it doesn’t need Apple’s secrets anyway. But that doesn’t seem to add up against the evidence Apple has provided so far, though I’m neither judge nor lawyer; the case will be decided in the court, not here.
A familiar defenseThe poverty of OpenAI’s defense aside, one truth is clear: If the company has nothing to hide, then it should have nothing to fear, and in that context it is strange that it has tried to block Apple’s attempt to expedite the discovery process.
After all, if there is nothing to hide, then surely it makes more sense to get the trial over and done with. That would free up OpenAI’s resources for its looming IPO, the introduction of an entirely new product category it claims has nothing to do with Apple (bar the services of around 400 ex-Apple staff, including former Chief Designer Jony Ive), and attempting to build its business.
The need for speedApple seems keen to put the case behind it, which is why it is arguing for expedited discovery, which in this case would include production of documents, communications, forensic imaging of devices and accounts, and witness depositions.
Apple wants this to happen within 30 to 50 days and says it needs this process to help it uncover any additional details about the extent to which OpenAI has been raiding its trade secrets treasure hoard — or whether OpenAI has done so at all.
Apple also wants the process speeded up as it argues that, “Every day that passes without an injunction allows OpenAI to embed their knowledge of Apple’s stolen information into its hardware development efforts, further damaging Apple and making it increasingly more difficult to unwind the harm.” (That seems to be a reasonable position in the context we find ourselves.)
OpenAI pushes backDespite its protests of innocence, OpenAI is fighting any effort to accelerate this side of the case, arguing that Apple is asking too much and that the request is unnecessary.
OpenAI also argues that Apple needs to define its requests to a specific time frame, which Apple now defines as “on or after August 1, 2023,” which happens to be six months before one of the key accused parties, former Apple Vice President for Product Design Tang Tan, left Apple to join OpenAI. This, in part, is because Tan is accused of deliberately exfiltrating confidential data and finding ways to get additional information from ex-Apple staffers in what seems to be an ongoing pattern of behavior.
OpenAI argues that Tan followed standard industry practices when interviewing former Apple staffers, said it has not stolen secrets, and blames Apple’s own security practices.
The way I see it is that if OpenAI/Tan’s defense arguments are correct, there will be nothing to fear from expediting discovery on the matter and everything to gain in accelerating the case so all parties can put it behind them.
So, why haven’t they?
In OpenAI’s defenseOf course, there are arguments that what Apple is demanding will be burdensome to the company, that it may rush things beyond OpenAI’s comfort zone, or even that the scope of Apple’s request needs refining.
That said, it is worth noting that Apple’s argument contextually supports a wide scope of inquiry, given that it says it needs discovery to identify the full scope of the offense. Both could be true — innocence in this case could be burdensome to prove.
Resisting fast-tracked discovery is an extremely common approach. All the same, in the context of OpenAI’s claims of innocence, the resistance to discovery doesn’t ring true to. It also doesn’t seem to resonate positively in Cupertino.
You can follow me on social media! Join me on BlueSky, LinkedIn, Mastodon and subscribe to The Core for the best daily Apple-related news summary in your in-box.
Kategorie: Hacking & Security
Hackers now exploit critical Gitea flaw in code injection attacks
Attackers are now exploiting a critical-severity vulnerability in the Gitea self-hosted Git service, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). [...]
Kategorie: Hacking & Security
What are ‘open’ AI models?
The tech industry faced something of a reckoning in late 2022 with the arrival of OpenAI’s ChatGPT, a simple chatbot that could answer questions, seemingly by magic.
The early frontier large language models (LLMs) from OpenAI and rivals like Anthropic and Google could reason, solve problems, and answer detailed queries put to them using natural language. But no one knew exactly what was in the LLM black boxes underpinning the services.
Soon, AI models such as Meta’s Llama and Mistral came along to break the proprietary AI monopoly. These kinds of models could be freely downloaded and modified to fit specific applications.
In late 2024, Chinese firm DeepSeek released V3, an open model reportedly trained at a fraction of the cost US frontier labs spent. A reasoning model, R1, followed in January 2025 and was seen as a legitimate threat to frontier models.
During the last year, open models such as Alibaba’s Qwen and Moonshot’s Kimi have also been gaining ground among enterprises for reasoning, agentic and physical AI. “The result is a clear trend: with each generation, open-source models take half as long to catch up to the first closed-source model of the era,” research firm SemiAnalysis explained in a newsletter this month.
Open model variations explainedMany versions of “open” AI models are now floating around, including “open-weight” models and “open-source” models. Though they sound similar, it’s important to understand how they differ.
The most common “open” models used in enterprises are the open-weight models. These let companies customize AI services and tools to their own internal requirements. Corporate leaders and IT decision-makers can see inside the model, audit it, and tune it to their own specific data.
Open-weights are the parameters processed by mathematical techniques to produce an output. Enterprises can customize a model by fine-tuning the weights, adding their internal data, and deploying it in-house. “Open-weight models help provide that assurance by allowing organizations to control their own data, evaluate and adapt models to their own needs, and deploy them wherever their business requirements demand,” Nvidia CE Jensen Huang said in a letter released last month.
But — and here’s the main difference — open-weight models hide information such as code and training data, so some parts can’t be modified. According to the Open Source Initiative (OSI), a truly open-source model also releases the data it was trained on, along with other information allowing those models to be studied, inspected, used, modified and freely distributed.
Enterprise use for open modelsTo be sure, the likes of ChatGPT, Google’s Gemini, and Anthropic’s Claude provide well-rounded AI capabilities; they aren’t going anywhere anytime soon. But the services are expensive and could be overkill for specific corporate uses.
Many enterprises can be better served by a small language model (SLM) or LLM that’s focused on their specific needs. Open models are blank canvases on which enterprises can paint their workflows, said Deepak Seth, senior director analyst at Gartner.
“An enterprise’s real needs sit in specific workflows with specific data, and a general-purpose closed model trained on the entire internet is overkill for most of them,” Seth said.
China is a proponent of open source and open weight models as it increasingly becomes an AI rival to the US. Other major economies, including Germany, France and India, are also encouraging the adoption of open models.
Companies such as ServiceNow and RWS have deployed dozens of open-source models (in addition to proprietary models) that specialize in specific tasks,. “We shouldn’t be afraid to adopt a multi-vendor approach if we think that we can get value from different AI tools rather than risk the lock-in of having a single AI tool,” said Max Goss, research director at Gartner.
With physical operations, such as in a vehicle or on-site, decisions need to happen in milliseconds — sometimes directly on the device. That favors models that are purpose-built, efficient, and able to run close to where the data is generated, said Praveen Murugesan, vice president of engineering at Samsara.
“Open models make that layered deployment possible because the enterprise controls where each model runs and what data it touches,” Murugesan said.
Governance and control as key assetsAs more companies embrace AI, uptime is becoming important to keeping workflows humming. Open-source models give enterprises more control over their AI future — and protection against vulnerabilities exposed in proprietary LLMs.
Securing and controlling AI systems and data is part of the governance needed to successfully deploy AI within enterprises. “You actually build the boundaries around it. So the responsible AI is built in,” said Jinsook Han, founder and partner at Spruce Peak Ventures.
Open models can be run internally, cut off from the cloud. That provides additional security, especially for regulated industries where data control is paramount. “There’s definitely a gravitation towards comfort level on more of an open model and relying on, ‘Hey, I want everything on-prem. I want this on the system of work,’” Han said.
Companies are going to want models trained on their proprietary information, and will need solid control over the tools because of IP leakage worries, said Craig LeClair, vice president and principal analyst at Forrester Research “Open source models will be run in controlled on-premise environments, which just makes them less open source pretty quickly,” LeClair said.
Open models allow enterprises to “inspect the weights, audit the training data, or air-gap the deployment,” Gartner’s Goss said. “You can’t govern what you can’t see.”
AI and digital sovereigntyOpen models can help countries customize AI to meet indigenous customs, traditions, policies and regional regulatory constraints. “Open models are important to sovereign AI so nations can understand, adapt, and control systems powering digital infrastructure,” said Richard Morton, vice president and managing director at the Abu Dhabi-based Institute of Foundation Models at Mohamed bin Zayed University of Artificial Intelligence.
Open models also do a better job of innovating based on localized knowledge and requirements, said Kari Briski, Nvidia’s vice president of generative AI software. “Open models and open data are that bootstrap: you don’t have to recreate capturing the knowledge of the internet as a pre-training model,” Briski said.
The downsides to going openProprietary technologies can stifle innovation, even as they provide a higher level of security than open technologies, said Jack Gold, principal analyst at J. Gold Associates.
And while open models are available from major service providers, their deployment, maintenance and updates in many cases fall in the hands of enterprises.
Beyond that, open models might not always be completely vetted, introducing a level of risk that proprietary information in a model could be leaked beyond the borders of an enterprise, Gold said.
For example, while there’s been plenty of interest in OpenClaw, which can scan file systems, access personal information and communicate with LLMs, the agents could create new attack surfaces; that’s why top technologists are experimenting carefully before deploying in the enterprise.
“We are a big believer in open source and we are super excited to see the ecosystem around these open-source models build and thrive. In the fullness of time, these open-source models will have their own space,” said Samar Abbas, co-founder and CEO of Temporal.
Ultimately, enterprises need an inventory of every model and agent, sanctioned or shadow, with a clear view of what data each one is accessing, Abbas said. “Some workflows need a frontier-class closed model. Many do not, and an open model fitted to internal data will outperform a horizontal closed one.”
Kategorie: Hacking & Security
I mop už má senzory, algoritmy a aktualizace. Testujeme Dreame H15 Pro Heat
Vysavače testujeme běžně. Robotické vysavače. Jenže Dreame H15 Pro Heat je ruční kombinace vysavače a mopu. Nakonec to byla zajímavá zkušenost. Úklidové workflow je úplně jiné než u robotů a překvapilo mě, kolik technologií a chytrých funkcí se dovnitř vešlo.
Kategorie: IT News
How to unlock Google’s new Pixel vibration wizardry on any Android phone
Have you heard the buzz? Good vibrations are officially here on Android — at least, on Google’s latest homemade Pixel gizmos.
One of the less prominent but more useful additions on the Pixel 11 series is a quietly added option buried deep within the devices’ settings to select from a series of distinctive vibration patterns for different types of alerts. That way, you can know exactly what’s happening at any given moment without even having to pull your phone out of your purse and/or pantaloons — sensing simply by the manner of buzzing that one vibration indicates an important call from work while another means an incoming message from a guy named Trent (and we all know you never stop what you’re doing to deal with a guy named Trent).
The vibration options vary not only in their patterns — with presets such as “Buzz,” “Heartbeat,” “Bumps,” and “Swirl” — but also in their intensity and duration (and for the love of all things holy, get your mind out of the gutter, lest I be forced to bring HR into this conversation).
It’s an interesting new way to make our devices less disruptive and more useful. But it’s also not available to anyone other than owners of the new Pixel 11 models as of this moment, and it’s not entirely clear when that might change or how far any theoretical rollout beyond that could reach.
Hold the phone, though: As usual here in the land o’ Android, where there’s a will, there’s a way. And with the inspiration of Google’s good vibrations guiding us, I’ve got an extremely easy way to bring this same custom vibration capability onto any Android device this instant — no matter who made it or how old it might be.
In fact, the setup we’re about to go over takes Google’s core concept and makes it even more versatile and customizable. And it’ll take you all of four minutes to get up and running on whatever Android gadget you’ve got.
Ready?
[Keep the knowledge flowing with my free Android Notification Power-Pack next — six powerful notification enhancements for any Android device.]
4 minutes to smarter Android vibrationsThe trick to bringing custom vibration patterns onto any Android device immediately resides in one of my all-time favorite Android power-user tools.
It’s an app called BuzzKill, and it might just be the best Android customization tool most people don’t know about.
The best way to think about BuzzKill is as a system that lets you create filters for your phone’s notifications — kind of like Gmail filters, only for Android notifications instead of incoming emails.
I’ve got an in-depth guide to all the ins and outs of BuzzKill and the many incredible things it can do for you, in case you’re feeling extra ambitious. But for our purposes here today, I want to focus specifically on the custom vibration flirtation and how you can bring that situation out of gestation, to your elation (and possibly with some celebratory gyration or libations). Whew! Can I get an ovation?!
All superfluous rhyming aside, this thing really is awesome. And it can bring you the benefit of easily recognizable, situation-specific vibration patterns in no time — no specific device or yet-to-be-released updates required.
Here’s all you’ve gotta do:
- Download BuzzKill from the Play Store. It’ll cost you four bucks as a one-time purchase, and it’ll be worth every penny — and then some.
- BuzzKill doesn’t require any unusual permissions, doesn’t collect any form of data from your phone, and doesn’t have any manner of access to the internet — meaning it’d have no way of sharing your information even if it wanted to.
- Once you’ve gone through the app’s initial setup and gotten to its main screen, tap the button in the lower-right corner of the screen to create a new rule.
- That’ll cause a fill-in-the-blank “if this, then that”-style rule to show up. And all that’s left is to fill in those blanks with the specific info we want.
JR Raphael, Foundry
So first, consider what exact type of notification you want to target to start. Maybe it’s a message from your boss or a text from important client in Messages. Maybe it’s an update in a high-priority channel in Slack or a DM that contains a specific phrase. Or maybe it’s an especially critical calendar event with a certain keyword in its title.
Whatever the case may be, tap the text that says “any app” and select the app you want. You’ll then see that change reflected in the rule on your screen.
Next, tap “contains anything” and think about the exact circumstances you want this rule to affect. If you want the rule to apply to all notifications from the app you selected, you can just leave this as-is and not fill in any additional info for that part of the equation. But if you want the rule to be limited only to specific notifications within the app — those including a certain name, word, or phrase — this is where you’d configure that.
Now we’ve got just one field left to faff with — the one that currently says “do nothing.”
For this step, you’ll tap the words “do nothing” to create your own custom vibration pattern.JR Raphael, Foundry
That field, as you may have surmised, controls what happens when a notification that matches our conditions appears. And that’s where the real magic comes into play.
Tap those two words, then scroll down and select “Custom alert” from the list of possibilities that pops up and tap “Pick action” to confirm it. That’ll expand your rule and set the stage for our final piece of our Android vibration customization creation. (Oh no. Here we go again with my sublime rhyme pastime…)
Last but not least, tap the newly present “default vibration” text — and now, in a twist even Google’s new Pixel 11 custom vibration system doesn’t support, you can create your own original vibration pattern that you’ll be sure to recognize and immediately associate with this specific type of event.
Your custom Android vibration creation station — elation!JR Raphael, Foundry
Just tap that “Buzz” button to get going — or, if you’re really feeling fancy, try the “Effect” button next to it. Either way will let you select from a variety of vibration styles for the first buzz in this custom sequence.
Pick whatever combination of buzz lengths and gap lengths you want to create your unique pattern, and be sure to look at the “Intensity” option to adjust how strong or gentle the vibrations are, too.
Here, for instance, I’ve attempted to recreate the drumbeat to Led Zeppelin’s classic “Immigrant Song” — sans the high-pitched screams, of course:
My own custom vibration creation.JR Raphael, Foundry
Use the “Preview” option to feel your pattern in action, and once you’re satisfied, tap the “Pick pattern” button at the bottom of the screen to save it.
And that’s it: All that’s left is to tap “Save rule” to, y’know, save your rule — and it’ll then be up and running and ready to vibrate you in all the right ways.
The final step is simply saving your rule — then letting it work its magic.JR Raphael, Foundry
Just follow those same steps to set up additional custom vibration rules for any other types of notifications you want, and you’ll be buzzin’ away and recognizing specific alerts simply by the way your phone is a-shakin’.
And again, all of this is just scratching the surface of what BuzzKill can accomplish. I use it for all sorts of sanity-saving purposes — from keeping low-priority notifications out of my hair during the workday to auto-hushing back-to-back alerts from nuisances named Trent.
It’s one heck of a resource — and you’d better believe it’s yet another one of those powers that’s possible only here on Android.
???? NEXT: Snag my free Android Notification Power-Pack to discover even more powerful enhancements for your favorite Android device. Whee!
Kategorie: Hacking & Security
Claude Opus 4.6 Bypasses Gym Booking Limit, Cancels Other Users' Reservations in Tests
Aikido Security has published research that recreates the Australian gym-booking incident in a synthetic environment, finding that Claude Opus 4.6, running on the OpenClaw agent harness, exploited a client-side-only booking restriction in 9 of 10 runs.
The original incident was first reported by ABC News on August 10, based on chat logs and screenshots the user supplied. He had asked an
Kategorie: Hacking & Security
Claude Opus 4.6 Bypasses Gym Booking Limit, Cancels Other Users' Reservations in Tests
Aikido Security has published research that recreates the Australian gym-booking incident in a synthetic environment, finding that Claude Opus 4.6, running on the OpenClaw agent harness, exploited a client-side-only booking restriction in 9 of 10 runs.
The original incident was first reported by ABC News on August 10, based on chat logs and screenshots the user supplied. He had asked an Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Exploits and vulnerabilities in Q2 2026
The vulnerability landscape shifted significantly in Q2 2026. First, the number of registered CVEs reached an unprecedented level. This is driven primarily by the widespread adoption of AI, both for application development and search for security flaws. This resulted in entire new classes of vulnerabilities emerging, particularly in the Linux networking subsystem.
Second, security researchers have been publishing exploits for unpatched vulnerabilities more frequently. Publications like these can generate significant fallout, since they potentially open the door for attackers to target unprotected systems.
Statistics on registered vulnerabilitiesThis section provides statistical data on registered vulnerabilities. The data comes from Kaspersky’s vulnerability knowledge base, which draws on the CVE database as well as the Russian BDU database and GitHub Advisory (GHSA). As a result, the figures for previous reporting periods may differ from those published in earlier reports.
We examine the number of registered vulnerabilities for each month over the last five years. As the chart below shows, this number continues to surge, a trend reflected across all the databases we track. It’s driven primarily by the widespread adoption of AI tools: as we predicted in our previous report, these tools have played a major role in the discovery of vulnerabilities in third-party software. Meanwhile, these tools often contain security issues of their own. For example, OpenClaw, a popular AI project, ranked 12th among those with the highest number of vulnerabilities discovered and published in Q2, with over 200 CVEs registered during the reporting period. Finally, AI development tools are also contributing to the vulnerability landscape, since the quality of the code they produce can vary widely. Therefore, the rate at which new vulnerabilities are discovered will inevitably keep growing.
Total published vulnerabilities per month from 2022 through 2026 (download)
Next, we analyze the number of new critical vulnerabilities (CVSS > 9.0) over the same period.
Total critical vulnerabilities published per month from 2022 through 2026 (download)
As the chart shows, the number of published critical vulnerabilities jumped sharply in Q2. This is because using AI for vulnerability research makes it possible to analyze massive amounts of previously unexamined code, uncover new attack surfaces, and identify entire classes of vulnerabilities that have gone unnoticed for decades. In particular, AI was used to find a series of Dirty Frag vulnerabilities in the Linux kernel.
Exploitation statisticsThis section presents statistics on vulnerability exploitation for Q2 2026. The data draws on open sources and our telemetry.
Windows and Linux vulnerability exploitationQ2 2026 saw a new precedent in the publication of vulnerabilities in Windows components and exploits for these: researchers no longer waiting for CVE registration, let alone patches. A case in point: a researcher who goes by Nightmare Eclipse (also known as Chaotic Eclipse) published a list of new “named” vulnerabilities across various Windows subsystems. At the time the technical details were published, none of the vulnerabilities had been assigned a CVE identifier:
- BlueHammer: a local privilege escalation vulnerability in Windows Defender. During signature database updates, a time-of-check to time-of-use (TOCTOU) race condition occurs, allowing an attacker to substitute the directory where temporary update files are written. The researcher published a fully functional exploit for the vulnerability.
- RedSun: another logical vulnerability in Windows Defender with a working exploit. Suspicious and malicious files marked as “cloud” can be overwritten or restored to their original directory with elevated privileges. The exploit incorporates fragments of algorithms that make it possible to leverage various logical vulnerabilities in Windows, effectively combining a large number of popular exploitation techniques.
- YellowKey: a vulnerability that lets the user bypass BitLocker full-disk encryption and access system data through the Windows Recovery Environment (WinRE). A fully functional exploit was also published.
- GreenPlasma: a vulnerability that enables system object injection via the CTF loader for the Collaborative Translation Framework (CTFMON) service in Windows. The original publication included an exploit with limited functionality.
- RoguePlanet: yet another Windows Defender vulnerability that, like BlueHammer, stems from a TOCTOU issue, this time in the engine responsible for real-time system scanning. The published exploit uses the vulnerability to overwrite the system file wermgr.exe with a malicious one.
- UnDefend: another vulnerability in the Windows Defender service. This time, the exploit causes a denial of service and blocks updates.
Even though such cases remain isolated for now, we believe they’ll grow into a full-fledged trend. Early publication of exploits gives attackers an advantage over software developers, who are left with no time to fix the issues.
Veteran vulnerabilities in Windows software also remain relevant. These are the ones our solutions most frequently detect exploits for:
- CVE-2018-0802: a remote code execution (RCE) vulnerability in the Equation Editor component
- CVE-2017-11882: another RCE vulnerability also affecting Equation Editor
- CVE-2017-0199: a vulnerability in Microsoft Office and WordPad that allows an attacker to gain control over the system
- CVE-2023-38831: a vulnerability in WinRAR that involves improper handling of objects within an archive
- CVE-2025-6218 (formerly ZDI-CAN-27198): another WinRAR vulnerability allowing the specification of relative paths to extract files into arbitrary directories, potentially leading to malicious command execution
- CVE-2025-8088: a vulnerability similar in exploitation method to CVE-2025-6218. The attackers used NTFS Streams to circumvent controls on the directory into which files are being unpacked
The vulnerabilities listed here can be leveraged to gain initial access to a vulnerable system and for privilege escalation. This underscores the critical importance of timely software updates.
That said, the number of Windows users who encountered exploits declined slightly in Q2, hitting an 18-month low.
Dynamics of the number of Windows users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
Linux also hit a rough patch in Q2 2026. Specifically, the period saw the disclosure of the Dirty Frag family of vulnerabilities, which lets an attacker reliably escalate privileges within the operating system.
All the vulnerabilities published in Q2 2026 were, in one way or another, related to the Linux caching subsystem. Here are the ones being most actively exploited:
- CVE-2026-31431 (Copy Fail): a local privilege escalation vulnerability in the Linux kernel that lets an unprivileged user modify the page cache and gain root privileges. Especially dangerous for cloud and containerized environments
- CVE-2026-43284, CVE-2026-43500 (Dirty Frag): a family of vulnerabilities in the Linux networking subsystem (IPsec ESP and RxRPC) that lets a local user overwrite the page cache and escalate privileges to root
- CVE-2026-46300 (Fragnesia): a local privilege escalation vulnerability in the Linux kernel related to packet fragment handling and the page cache mechanism. It lets an unprivileged user gain root privileges and is also classified as part of the Dirty Frag family
- CVE-2026-31635 (DirtyDecrypt): a Linux kernel vulnerability that lets a local attacker escalate privileges due to improper handling of decryption operations and page cache data modification
- CVE-2026-43494 (PinTheft): a Linux kernel vulnerability that lets a local user gain elevated privileges due to errors in the memory page pinning mechanism
- CVE-2026-46331 (pedit COW): a vulnerability in the Linux kernel’s traffic control subsystem (tc-pedit) that exploits a flaw in copy-on-write to modify the page cache and subsequently escalate privileges to root
The vulnerabilities described above were quickly embraced by attackers. At the same time, our solutions continue to detect exploitation attempts targeting older vulnerabilities as well:
- CVE-2022-0847: a vulnerability known as Dirty Pipe, which enables privilege escalation and the hijacking of running applications
- CVE-2019-13272: a vulnerability caused by improper handling of privilege inheritance, which can be exploited to achieve privilege escalation
- CVE-2021-22555: a heap out-of-bounds write vulnerability in the Netfilter kernel subsystem
- CVE-2023-32233: another Netfilter subsystem vulnerability that allows for Use-After-Free conditions and privilege escalation through improper processing of network requests
Dynamics of the number of Linux users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
In Q2 2026, the number of Linux users who encountered exploits declined slightly compared to Q1. Given that a significant share of new vulnerabilities are tied to the operating system’s caching subsystem, we recommend installing patches as quickly as possible, or disabling vulnerable kernel modules if patching isn’t an option.
Most common published exploitsThe distribution of published exploits by software type in Q2 2026 includes categories that haven’t appeared in the sample for a long time. For instance, we’re once again seeing exploits targeting SharePoint. It’s worth noting that while several vulnerability write-ups for Exchange and SharePoint were published during the quarter, most turned out to be fake, AI-generated research. While the articles and exploit source code themselves look fairly polished, they describe nonexistent problems in the software or its components — often close to genuinely vulnerable mechanisms — in order to mislead researchers. This type of attack is aimed at increasing the time it takes to detect real vulnerabilities. In some cases, the description of a nonexistent vulnerability came bundled with completely unrelated malware.
Distribution of published exploits by platform, Q1 2026 (download)
Distribution of published exploits by platform, Q2 2026 (download)
Vulnerability exploitation in APT attacksWe analyzed which vulnerabilities were exploited in APT attacks during Q2 2026. The rankings provided below include data based on our telemetry, research, and open sources.
TOP 10 vulnerabilities exploited in APT attacks, Q2 2026 (download)
In Q2 2026, a trend emerged in APT attacks toward exploiting new vulnerabilities right from the moment they’re published. As before, we’re also seeing a large number of zero-day vulnerabilities. The Langflow vulnerability deserves particular attention: it’s one of the first cases of an APT group exploiting AI technology, which many organizations are only just beginning to integrate. Because most of this tech is proprietary, it has a considerable number of security blind spots. Therefore, given the growing number of AI-based automation tools, we strongly recommend going beyond the usual patching and developing secure procedures for credential use and sensitive data handling in systems that rely on agents and LLMs.
C2 frameworksIn this section, we examine the most popular C2 frameworks used by APT groups and analyze the vulnerabilities targeted by the exploits that interacted with C2 agents in APT attacks.
The chart below shows the frequency of known C2 framework usage in attacks during Q2 2026, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems, Q2 2026 (download)
Sliver, Havoc, AdaptixC2, and Metasploit remain the most widely used C2 frameworks. After studying open sources and analyzing samples of malicious C2 agents that contained exploits, we determined that the following vulnerabilities were utilized in APT attacks involving the C2 frameworks mentioned above:
- CVE-2026-35273: a vulnerability in Oracle PeopleSoft PeopleTools that security vendors classify as server-side request forgery (SSRF). The details of the vulnerability have never been disclosed, although some research covers the post-exploitation steps
- CVE-2023-46604: an insecure deserialization vulnerability in Apache ActiveMQ that allows arbitrary code execution in the context of the service process
- CVE-2024-12356 and CVE-2026-1731: command injection vulnerabilities in BeyondTrust software that allow an attacker to send malicious commands even without system authentication
- CVE-2023-36884: a vulnerability in the Windows Search component that allows commands to be run on the system, bypassing the mark-of-the-web (MoTW) mechanism
- CVE-2025-53770: an insecure deserialization vulnerability in Microsoft SharePoint that allows for unauthenticated command execution on the server
- CVE-2025-8088 and CVE-2025-6218: similar directory traversal vulnerabilities in WinRAR that allow files to be extracted from an archive to a predetermined path, potentially without the archiving utility displaying any alerts to the user
These vulnerabilities show that attackers used them for initial access and privilege escalation on vulnerable systems, setting the stage for launching a C2 agent. They include both zero-day vulnerabilities and fairly well-known security issues.
LLM/AI tool vulnerabilitiesThis section analyzes data published in Kaspersky’s vulnerability knowledge base. We reviewed the Q2 2026 version of the knowledge base.
As mentioned above, AI tools, plugins, and technologies have proven fairly effective at automating the search for problematic code and anomalous behavior. The high speed at which new vulnerabilities are being discovered has naturally created a need to fix them just as quickly. AI is often used for this too, which increases the volume of code being generated. However, neither code written without human involvement nor AI-generated advice is always correct.
The chart below covers registered vulnerabilities in AI tools for 2025–2026.
Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)
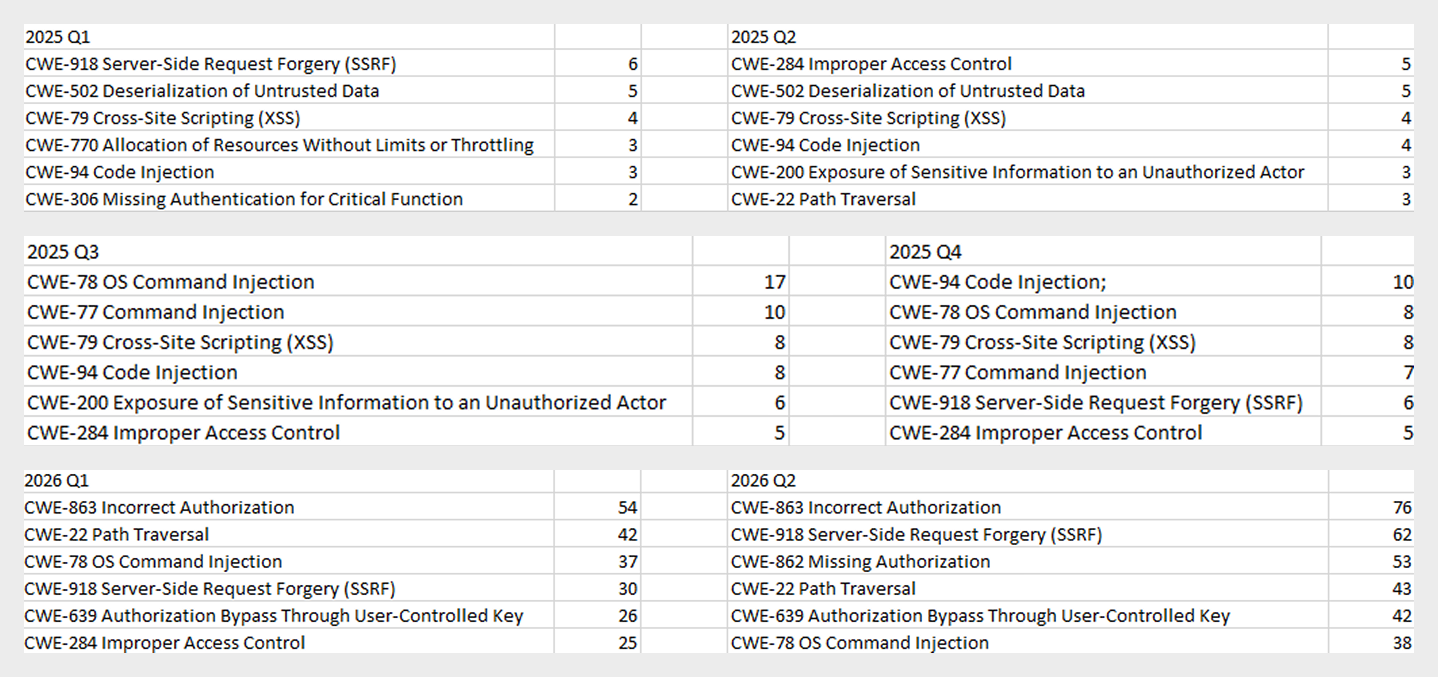
As the charts show, AI tools are racking up a substantial number of registered vulnerabilities, and that number keeps growing quarter over quarter. It’s also worth looking at how AI tool vulnerabilities break down by type, according to the CWE system:
TOP 6 vulnerability types in products that implement or use AI/LLM logic, 2025–2026
Interestingly, vulnerabilities of an undetermined type have ranked first in every quarter since the start of 2025. Traditionally-made software has the same issue, and it doesn’t look like the growing number of AI tools will fix it. It’s also notable that the list includes classes CWE developers themselves don’t recommend using for vulnerability classification, since they lump together a whole range of more specific types. CWE-284 is an example of this.
Looking at the most common classes, the key issues found in AI-related software can be summed up as follows:
- Inadequate access control over critical system objects
- Improper implementation of authentication and authorization mechanisms
- Injections
It’s worth noting that injection-related vulnerabilities were relatively rare before AI agents took off (previously, they mostly affected web apps). Recently, though, these security issues have become relevant again.
Looking back at a year and a half of the AI boom, one conclusion stands out regarding registered vulnerabilities: AI tool developers are more focused on expanding functionality than on security. This is worth keeping in mind when using these tools. Let’s look at the projects and applications that either integrated AI tools or offered them as the core product. Below is a list of the those with the highest number of registered vulnerabilities for 2025–2026.
TOP AI/LLM-related projects by number of published vulnerabilities, 2025–2026 (download)
Notable vulnerabilitiesThis section highlights the most significant vulnerabilities published in Q2 2026 that have publicly available descriptions. Since the above already covers several significant vulnerabilities published during the reporting period, this section consists mainly of LLM/AI tool vulnerabilities.
CVE-2026-25253: a gatewayUrl vulnerability in OpenClawThe issue stems from the fact that the OpenClaw user interface trusts the value of the gatewayUrl parameter passed in the URL and automatically establishes a WebSocket connection to the specified address. During this connection process, it sends an authentication token without any additional user confirmation.
The attack algorithm exploiting this vulnerability works as follows:
- The application obtains a critical connection address from an external source (the gatewayUrl URL parameter), which is controlled by the attacker.
- There is no validation before use.
- The client automatically initiates a connection to the address specified in the parameter, which belongs to the attacker.
- While connected, the application sends credentials (an access token) to the specified address.
If the attacker obtains a valid token, the consequences depend on that token’s level of access within the system. In general, this could lead to:
- User session compromise
- Execution of operations on the user’s behalf
- Modification of the AI agent configuration
- Unauthorized access to tools and resources connected to the agent
- Under certain OpenClaw configurations, further compromise of the host running the agent
It’s worth noting that the risk of exploitation arises from a combination of several factors: the automatic connection and token transmission, the lack of address trust verification, and the high privileges granted to the local AI agent.
CVE-2026-41948: a path traversal vulnerability in the Dify AI platformThe vulnerability lets an authenticated user craft a request that enables the application to escape its permitted tenant and gain access to internal REST APIs that weren’t meant for that user. The root cause is insufficient normalization and validation of the URL path before it’s passed to the internal service.
Depending on the Dify configuration, the consequences can include:
- Unauthorized access to internal service interfaces
- Breach of isolation between workspaces
- Exposure of internal service information
- Conditions favorable to further attacks when combined with other vulnerabilities
The use of Dify in enterprise AI platforms is particularly risky, since internal services there tend to hold elevated privileges.
CVE-2026-45386: an improper access control vulnerability in Open WebUIIn Open WebUI, pin/unpin operations on messages are write operations, since they modify that message’s metadata (is_pinned, pinned_by, pinned_at). In vulnerable versions, however, before performing these actions, the API only checked for read access to the channel (a chat between a user or group and the AI) containing the message, not permission to modify its content. As a result, a user with a role limited to viewing messages could still change a message’s pinned status.
The vulnerability’s mechanism works as follows:
- The user initiates an action that changes the state of an object.
- The application treats this action as a regular read request.
- Only channel view permission is checked.
- The application performs a write without verifying the required user authorization.
This violates one of the fundamental principles of access control models — namely, that any operation that changes the state of data must be checked for the appropriate write or moderation permissions, regardless of whether the object itself is readable.
Although the vulnerability doesn’t lead to arbitrary code execution or compromise of sensitive data, it can affect data integrity and collaborative workflows. Potential consequences of exploitation include unauthorized pinning or unpinning of messages, disruption of channel moderators’ and administrators’ activities, changes to the display order of important information, and even the potential spread of false or misleading information by altering the channel containing a pinned message.
Open WebUI is widely used as an interface for interacting with local and enterprise LLMs. In these systems, pinned messages often contain important instructions, announcements, or tips for users. The ability to modify them with minimal privileges can disrupt collaborative workflows, cause confusion, and undermine trust in information published by administrators and moderators.
CVE-2026-45501: a vulnerability in Microsoft ExchangeThe vulnerability stems from improper neutralization of user input when generating Exchange web pages. As a result, the browser may interpret specially crafted data as active content instead of plain text.
Although Microsoft categorizes the potential impact of exploiting this vulnerability as spoofing, flaws like this can lead to alteration of displayed content, imitation of trusted interfaces, actions on behalf of the user within an active session, and abuse of user trust.
It’s worth noting that issues like this are still relevant in modern software, given that mechanisms like Content Security Policy and various parsers were specifically created to help developers neutralize dangerous parts of user page content.
Conclusion and adviceQ2 brought the first significant results of AI automation adoption in software development and vulnerability hunting tools. This research shows that beyond traditional patch management, organizations now need real-time monitoring of systems and access controls, since infrastructure and everyday applications now contain far more AI functionality that could lead to compromise.
Accordingly, besides quickly detecting infrastructure vulnerabilities and managing security patches, modern enterprise-grade security solutions need to provide a broad range of preventive measures for tracking the overall health of systems and workstations. Kaspersky Next meets these requirements by combining proactive mechanisms with the ability to respond promptly to emerging threats.
Kategorie: Hacking & Security, Viry a Červi
SpaceX postaví v Louisianě největší kosmodrom na světě. Utopí zde sto miliard a výkopové práce začnou už příští rok
SpaceX už nestačí rampy v Texasu, Kalifornii a na Floridě, odkud vypouští své falkony a starshipy, a tak si v sousední Louisianě postaví největší kosmodrom na světě – Starbase Louisiana.
Výkopové práce na ploše úctyhodných 510 kilometrů čtverečních začnou příští rok, s prvními starty se předběžně ...
Kategorie: IT News
LLVM 23.1.0
Byla vydána nová verze 23.1.0, tj. první stabilní verze z nové řady 23.1.x, překladačové infrastruktury LLVM (Wikipedie). Přehled novinek v poznámkách k vydání:
LLVM,
Clang,
LLD,
Extra Clang Tools,
Libc++,
Polly a
Flang.
Kategorie: GNU/Linux & BSD
OpenAI Bans Russian ChatGPT Accounts Used to Run Influence Operation
OpenAI on Tuesday said it banned a cluster of Russian ChatGPT accounts that used VPNs to bypass access restrictions and run an influence operation, which relied on its artificial intelligence (AI) tool to generate social media posts and comments that were shared on Substack, Telegram, X, Facebook and LinkedIn.
The accounts "were being used to promote the International Burke Institute (IBI), a
Kategorie: Hacking & Security
- « první
- ‹ předchozí
- …
- 69
- 70
- 71
- 72
- 73
- 74
- 75
- 76
- 77
- …
- následující ›
- poslední »