Agregátor RSS
Hackers now scanning systems for recently-patched Oracle flaw
Attackers have begun probing the Internet for systems unpatched against a recently disclosed critical Oracle E-Business Suite (EBS) vulnerability. [...]
Kategorie: Hacking & Security
Cisco open sources tool for detecting AI agents on hacking sprees
Cisco has open sourced a behavior detection engine that watches AI agents, to help security teams prevent rogue agents from going off the rails like they did with the Hugging Face hack – or worse. It’s called Project Quarry, and it aims to provide a “shared language” for evaluating agent behavior, along the lines of what Snort, which Cisco also maintains, did for detecting malicious network traffic and what YARA did for rule-based malware identification. Most detection tools rely on specific interactions with an AI model or agent. Did it attempt prompt injection? Or did the agent call an attack tool? “But what is missing is the entire context under which something may occur,” Amy Chang, head of AI threat and security research at Cisco, said in an exclusive interview with The Register. She likened this to credit card fraud detection. Without context, individual transactions such as a small test charge or a single purchase in a location far away from a card-holder's usual location may not raise any flags. “And then you try again,” making another fraudulent purchase, “and that went through, too. So now I’m gonna buy the PS5,” Chang said. “Those are the things that Quarry addresses by taking into consideration the entire agent session,” she explained. “One tool call may seem in-scope until you realize that that next step is taking that information and sending it to an attacker-controlled inbox or server.” Even data theft is a sequence and not a single agentic action. Agentic AI security firm Invariant Labs demonstrated this with a proof-of-concept attack against GitHub's MCP server that hijacked a user's agent via a malicious GitHub Issue, and coerced it into leaking data from private repositories. Simply reading a configuration file, or sending a request to an external endpoint may be legitimate agentic actions. However, combining the two can lead to data exfiltration – and shows “why action relationships matter,” wrote Chang and fellow Cisco researchers Adam Swanda, Ravikumar Balakrishnan, and Konstantin Berlin in a blog post about Quarry shared with The Register ahead of publication “A policy can produce a finding when the trace shows a sensitive file read followed within a defined window by an external send,” they wrote. “The risk comes from the relationship between the two actions, so the finding should preserve evidence from both." Quarry covers single- and multi-turn large language model conversations, agents, tool use, Model Context Protocol (MCP) interactions, and multimodal inputs. In addition to the open source code itself, the project’s GitHub repository includes installation instructions, supported Python versions, plugins for Claude Code, Codex and other MCP-compatible agents, configuration examples, rule-writing guidance, and a rule starter pack. For instance, with the rule pack, “If a base-64 encoded malware is somewhere in the tool call, that would result in a block,” Chang said. The rule format looks similar to a YARA or Snort rule, with a header that details the traffic to examine, content to match, and metadata for tracking the rule. Here’s a Quarry rule that flags an agent that reads a credentials file: While the Cisco Ai researchers have not run Quarry against data describing the OpenAI-Hugging Face incident, they suggest that if the intrusion had been read as a complete, step-by-step record of a single session, there were several points where the AI agents’ steps would have given a Quarry rule something to act on and flag for humans. For example, Quarry would probably have flagged internet access from a sandbox. “The rule can flag specific tool calls that reach an external server asset that wasn’t in the task’s allow list,” Chang said. “Another one would be credentials found and used somewhere else.” According to OpenAI’s technical report about the Hugging Face intrusion, this is exactly what happened on July 10, when an agent validated 14 exposed Hugging Face tokens with write access and shared them. “The rule would flag that there was a credential in the tool result that then called an outside service, which is likely not within the parameters of what you would want to do in this case,” Chang said. “We don't want you to go and search for credentials that may have been leaked or inadvertently exposed and then utilize them to conduct a task.” The Cisco team is quick to say that rules along are not a substitute for chain-of-thought monitors, or other forms of human oversight – but they do help record a pattern that other teams can then “review, test, and apply to their own agents,” they wrote. Herein also lies the benefit of open source, and a collective approach to defending against adversarial use of AI, Chang said. “Do we have all the answers? No,” Chang said. “We all see slices of the problem, and it’s important for us to share what we see.”®
Kategorie: Viry a Červi
Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker to run code on a machine before its operating system loads, but only while the machine is booting over the network.
UEFI firmware is the software that runs first when a computer is switched on, before the operating system. An attacker who can reach the machine Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Který Fallout je nejlepší? Seřadili jsme všechny díly postapokalyptické série
Fallout patří mezi největší klasiky postapokalyptického žánru. Za čtvrt století dlouhou historii prošla velkými změnami, které nebyly vždy k lepšímu. Takhle bychom všechny díly seřadili my.
Kategorie: IT News
123 Reg discloses 'AI cyberattack' on customer data, suspects China nexus
UK domain registrar 123 Reg (no relation – Ed) says it was the victim of an “AI-driven cyberattack” that exposed customer data. Customers began receiving their notification emails this week, informing them that their contact information, "related customer relationship data," company VAT numbers, and "product information from an application programming interface (API)" were compromised. A company spokesperson elaborated, saying this means that names, phone numbers, countries, language and currency preferences, account creation dates, the products on the account, and marketing preferences were affected. 123 Reg described the September 18 intrusion as "the first known AI-driven cyberattack against our company," and told The Register that early signs point toward a China-nexus attacker. "Our investigation identified IP addresses that we assessed to be the core attacker infrastructure, which were hosted in China and Singapore, indicating a strong Chinese nexus," the spokesperson said. "Our investigation further identified AI cyberattack 'skills' hosted on Chinese infrastructure, including copies of skills open sourced by Anthropic and several other AI exploitation frameworks and scripts." They went on to say that many of the artefacts left behind led 123 Reg to suspect that a Chinese state-sponsored group, known for abusing Claude Code in attacks against at least 30 organizations, could be behind the break-in. There is also a suspicion that the same group that hit a number of South Korea’s financial institutions using open-source Chinese AI tool ARTEX, was behind the attack on 123 Reg too. "The TA's mirror of 'anthropic_skills,' and the account naming conventions found on the Chinese servers are consistent with preparation of this class of AI-augmented operation," the spokesperson told us. "In addition, on October 7, 2026, CrowdStrike published CSA-261162, describing an unknown, likely Chinese-speaking actor that targeted several South Korean financial organizations starting in late September 2026, which is the same period during which we were attacked. "That actor used ARTEX, an open-source Chinese-developed agentic penetration-testing tool released in July 2026, which was also observed to be used in the attack that targeted us." The GoDaddy-owned registrar reported the attack to law enforcement agencies, brought in outside cybersecurity support, and notified the FTC, as well as the data protection authorities in the UK and EU. The company spokesperson added that it worked with Singapore-based ISPs to shut down the attacker's servers in the region, which helped disrupt the attack, in addition to "other actions by us and industry partners." 123 Reg's email to customers stated the attacker's activity "was limited to reading" customer data, although the spokesperson told us "it's possible they created copies of the information," and that this is what prompted the notification. The registrar urged customers to stay alert to the potential misuse of their data, and to treat communications appearing to come from the company with caution. "If you receive a message or call and aren't sure it's from 123 Reg, go directly to our website and log in," the email said. "We will never contact you to request your password, payment details, or verification codes by email, text, or phone. "We also strongly recommend turning on two-step verification (2SV), which helps keep your account protected even if someone tricks you into sharing your password. You can find instructions for setting up 2SV in your 123 Reg account. "We apologize for any inconvenience this may have caused." ®
Kategorie: Viry a Červi
Wazuh and AI for Enhanced SOC Workflows
Artificial Intelligence (AI) has become one of this decade's defining technologies. From healthcare and finance to manufacturing and education, organizations increasingly rely on AI to automate repetitive tasks, uncover patterns hidden within large datasets, and support faster decision-making. Cybersecurity has experienced a similar transformation. While attackers employ AI to automate [email protected]
Kategorie: Hacking & Security
Claude dokázal vytvořit téměř dokonalé 3D modely listů. Stačil mi jediný prompt
AI agenti už před nějakým časem opustili bezpečí webových prohlížečů a dedikovaných klientů a začali ovládat nejrůznější programy na počítači.
Zpravidla se to děje buď pomocí protokolu MCP, tedy lokálního serveru, který si aplikace spustí a chatbot s ní pak může strojově komunikovat, anebo vedle ...
Kategorie: IT News
Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation.
The list of eight vulnerabilities is as follows -
CVE-2026-104351 (CVSS score: 9.9) - A code injection vulnerability that could lead to arbitrary code execution.
Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Trump says Microsoft abuses visa laws. Microsoft disagrees. Who’s telling the truth?
Decades ago, the United States established programs that allow businesses to hire highly skilled foreign workers — the H-1B visa program and a related green card program. They’re designed to make sure we lead the world in technology. Not uncommonly, H-1B workers and green card holders eventually become American citizens.
One of the best-known examples is Microsoft CEO Satya Nadella. He came to the US from India on the green card program, then switched to the H-1B visa program in the early to mid-1990s when working for Microsoft. He ended up becoming a US citizen. In 2014, he was appointed Microsoft CEO and subsequently architected one of the biggest turnarounds in tech history. Under his leadership, Microsoft has become nearly a $4 trillion company.
President Trump, who rode an anti-immigrant message to the White House two times, has both the green card and H-1B programs in his crosshairs — and he’s aiming right at Microsoft.
Earlier this month he claimed Microsoft, Adobe, and several other companies had abused an important part of the green card program called PERM, which helps H-1B visa holders get green cards. He’s suspended their use of it. Microsoft fired back that Trump was off target and the company has done nothing wrong.
Who’s right and who’s wrong? We’ll follow the facts to find out.
Trump’s and Vance’s fact-free charges against MicrosoftA green card allows a foreigner to stay and work in the US permanently. Companies often sponsor people for green cards, although there are other ways someone can get one as well. Once someone has a green card, they can switch to work for a company other than the one that sponsored them. Getting a green card is often a first step for someone to become a US citizen.
An H-1B visa, on the other hand, is temporary and allows a skilled worker to stay in the US for three years, which can be extended to six years.
The two programs are closely related. Not uncommonly, someone on an H-1B visa can get a green card by having the company sponsoring them apply for it through the PERM program.
PERM is what Trump targeted earlier this month. He suspended Microsoft, Adobe, and several other companies from the PERM program so they can’t get their H-1B workers green cards.
Vice President Vance claimed Microsoft had “abused” the system by laying off American workers and replacing them with lower-cost foreign workers. He said in a news conference that there was “no company in the United States, unfortunately, that has abused this system more.”
Vance contends that Microsoft laid off 6,000 American workers in the past year and replaced them with much less expensive foreign H-1B visa and green card holders. He called the foreign workers “indentured servants.”
Vance concluded, “If you do the math, for every worker that Microsoft laid off, they replaced that worker with one and a half foreign indentured servants. Now that is a scandalous system.”
That’s pretty damning, if true. But as so often is true with the Trump administration, the charges bear no relationship to the truth. For one thing, Vance’s numbers include Microsoft’s use of the H-1B program as well as the green card program.
It’s not just PERM and the green-card program that Trump has been attacking. Since his first election, he’s targeted the H-1B visa program as part of his war on immigrants and immigration. Last year, he imposed a $100,000 fee on companies for each H-1B visa they use, a move which a judge earlier this year ruled was illegal. His administration has appealed the ruling.
In August, the Department of Homeland Security proposed a similar fee plan, with companies having to pay $103,265 to hire an H-1B worker. The administration has also filed proposals to end work authorization for some H-1B workers’ spouses and eliminate the 60-day grace period H-1B workers have now to stay in the US after a job loss so they can look for new work.
Microsoft fights back with factsAfter Vance’s charges, Microsoft immediately fired back with a statement that succinctly pointed out how wrong his claims were. The company addressed Vance’s false claims about both the H-1B and PERM programs.
Microsoft noted that “of the approximately 6,000 H-1B visa applications we submitted in the last fiscal year, 80% were to extend or change the status of existing Microsoft employees. These were not to hire new people.”
It went on to say, “the remaining filings for new employees were for individuals already legally in the United States who decided to come work for us.”
Beyond that, Microsoft’s layoffs in the past year had nothing to do with H-1B visas or green cards. Even if Microsoft didn’t have a single H-1B visa worker or green card holder, the layoffs would have gone through.
All that’s not to say the H-1B program is perfect. Some companies do hire foreign workers under the program to perform jobs Americans can do and pay them less. Disney, for example, in 2014 replaced several hundred IT staff members with lower-paid foreign workers who had no unique, highly specialized skills. In fact, the Disney workers trained the foreign workers to do their jobs.
There have also long been charges that under the program, companies that provide IT outsourcing hire foreign workers with no greater skills than US workers and pay them less. The Biden administration issued a series of rules cracking down on that. It’s not clear how effective those rules have been. When Trump suspended Microsoft and Adobe from the PERM program, he also suspended several big IT outsourcing firms.
Trump honors foreign-born CEOsVance’s news conference was followed by a very different Trump news conference several hours later, offering the usual head-spinning sense of unreality so often found with the Trump administration. Trump awarded Nadella the National Medal of Technology and Innovation — an award he called “so well deserved.” No mention of the H-1B or PERM charges against the company, or that Nadella worked for Microsoft on an H-1B visa and with a green card in the 1990s.
At the same press conference, Trump awarded Elon Musk, CEO of Tesla and SpaceX, the National Medal of Science. Other foreign-born honorees included Google co-founder Sergey Brin, Nvidia CEO Jensen Huang, and AMD CEO Lisa Su.
Musk says he’s a former H-1B holder and is a big supporter of the program. He’s written on X, “The reason I’m in America along with so many critical people who built SpaceX, Tesla and hundreds of other companies that made America strong is because of H1B.”
Musk being Musk, there hasn’t been a peep from him about Trump’s latest assault on the program.
The upshotNothing could be clearer: Trump’s and Vance’s charges against Microsoft are lies. It’s true that some companies have abused the H-1B program, and possibly PERM, but Microsoft isn’t one of them.
Kategorie: Hacking & Security
CISA warns of hackers now exploiting critical Node2Shell flaw
On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed that hackers have begun exploiting a critical Brotli vulnerability known as Node2Shell, Broccoli2Shell, and HTTP2Shell. [...]
Kategorie: Hacking & Security
American Organizations Under Attack: Skyw4lker Device Code Phishing Campaign Exposed
Modern phishing campaigns can compromise American businesses without relying on traditional credential theft. Attackers can abuse legitimate cloud services, authentication mechanisms, and trusted business workflows to gain access to corporate accounts while leaving fewer obvious signs behind.
ANY.RUN's analysis of Skyw4lker, a device code phishing campaign primarily targeting U.S. [email protected]
Kategorie: Hacking & Security
Opera launches local browser AI, testing enterprise privacy and AI PC strategies
Opera has begun rolling out AI models that run locally in its browser, potentially allowing enterprises to perform certain AI tasks on existing PCs without sending the relevant data to cloud AI providers.
The company said it has introduced support for WebAI, a proposed web standard, through an opt-in early preview in Opera One. The technology allows websites and browser extensions to access AI models running locally in the browser for tasks such as generating text and classifying content.
The WebAI preview supports 64-bit Windows PCs running Intel or AMD processors and Macs powered by Apple silicon. Opera does not specify a requirement for a dedicated neural processing unit, although it says performance depends on the device’s hardware.
The preview does not currently support Windows on Arm, potentially limiting its availability across some newer AI PCs.
The feature is optional, with AI models downloaded only after users enable it. Opera said website-specific permissions allow users to control which sites can access the locally running models.
Opera said its implementation supports models including Google’s Gemma and Apple’s on-device foundation model on compatible Macs. The company said it plans to introduce additional models optimized for different devices as it expands the technology.
Local AI shifts enterprise security risksOpera’s implementation could have implications beyond its own browsers if the proposed WebAI standard gains wider adoption, potentially bringing locally running AI models to more enterprise users.
The privacy benefits for enterprises could depend on how organizations control access to locally running models, particularly through websites and browser extensions.
Pareekh Jain, CEO of Pareekh Consulting, said processing sensitive information locally could reduce enterprise security risks by limiting the need to send data to external AI providers. However, he warned that the approach could make it harder for IT departments to monitor activity on individual devices.
“It is easier for IT to monitor internet traffic,” Jain said, adding that monitoring activity on individual laptops can be more difficult.
He warned that malicious websites could potentially manipulate local AI models through hidden prompts, while rogue browser extensions could gain access to sensitive information displayed on a user’s screen.
“Local processing reduces risks but does not eliminate them,” Jain said.
Enforcing consistent safeguards across employee devices would become imperative for enterprises, according to Tulika Sheel, senior vice president at Kadence International.
“Enterprises still need controls over which websites and extensions can access local models, how information is used, and how models and browser permissions are managed across the organization,” she said.
Could browser AI reduce the need for new AI PCs?While WebAI can run on existing computers, its ability to reduce enterprise spending on new AI PCs will depend on whether those machines can deliver acceptable performance for everyday business tasks.
Jain said smaller AI models could handle tasks such as summarization and rewriting on existing PCs, potentially reducing the need for immediate hardware upgrades.
“Complex reasoning and advanced AI workloads will still benefit from dedicated AI hardware or cloud infrastructure,” he said.
WebAI’s support for compatible models from different providers could give developers greater flexibility in choosing which AI systems to use.
Browser-based AI could also reduce enterprise spending on cloud services by lowering API usage and dependence on external AI providers. However, limitations in model capabilities and enterprise integration could restrict its usefulness for more sophisticated applications.
“The future will likely be hybrid, with browser AI handling simpler tasks and cloud AI supporting advanced workloads,” Jain said.
Sheel said enterprises would still need to account for the costs of model updates and integration with existing systems, even if local processing reduces their cloud AI usage.
“Lower usage costs do not automatically mean lower total costs,” she said.
Kategorie: Hacking & Security
Millions of security cameras at risk: DoS vulnerability in Intelbras devices
Background
Network-connected surveillance cameras are now widespread in both home and enterprise environments, so securing them is essential to safeguarding physical spaces and sensitive assets. As these devices continue to gain new features and network connectivity capabilities, vulnerabilities in their implementation can have significant security implications.
During our research, we discovered a denial-of-service vulnerability that affects Intelbras IP cameras systems. The flaw resides in a firmware update endpoint that is accessible without authentication and allows anyone with access to the local Wi-Fi network to knock cameras offline. A single request disrupts the camera for only about a minute, but sending periodic requests keeps the device offline indefinitely. We reported the issue to Intelbras, monitored the remediation process, validated the fix in the new firmware, and will now demonstrate the exploitation procedure step-by-step.
Following our notification, Intelbras patched the vulnerability and released updated firmware (R.260804) along with update instructions. A candidate ID of CAN-2026-2035970 has been assigned by MITRE following submission, pending the final CVE assignment. Additionally, the Intelbras team recently informed us that MITRE has classified the vulnerability as Medium, assigning it a score of 5.1 under the CVSS 4.0 framework. The issue discussed in this article is no longer present in the latest firmware version.
FirmwareIntelbras provides firmware files on its official website. While users can manually install these updates via an SD card, the cameras also natively support firmware upgrades over the local network via their web interface and mobile app. We obtained the firmware version v240927 for the iM3B-C (IM3 C) camera, which was the latest available version at the time of our research. According to Intelbras, the same firmware is also compatible with the iMX C, iM4 C, iM5 SC, iME 360 C, and iM7+ FC models. Below, we can view the firmware version and the camera model used as an example.
To provide context, we will explain how the camera’s authentication mechanism works and why it is relevant to accessing the camera’s endpoints. The main firmware component is an ARM binary named sonia, responsible for controlling the kernel drivers used by the camera hardware, authentication, and livestream recording, among other things.
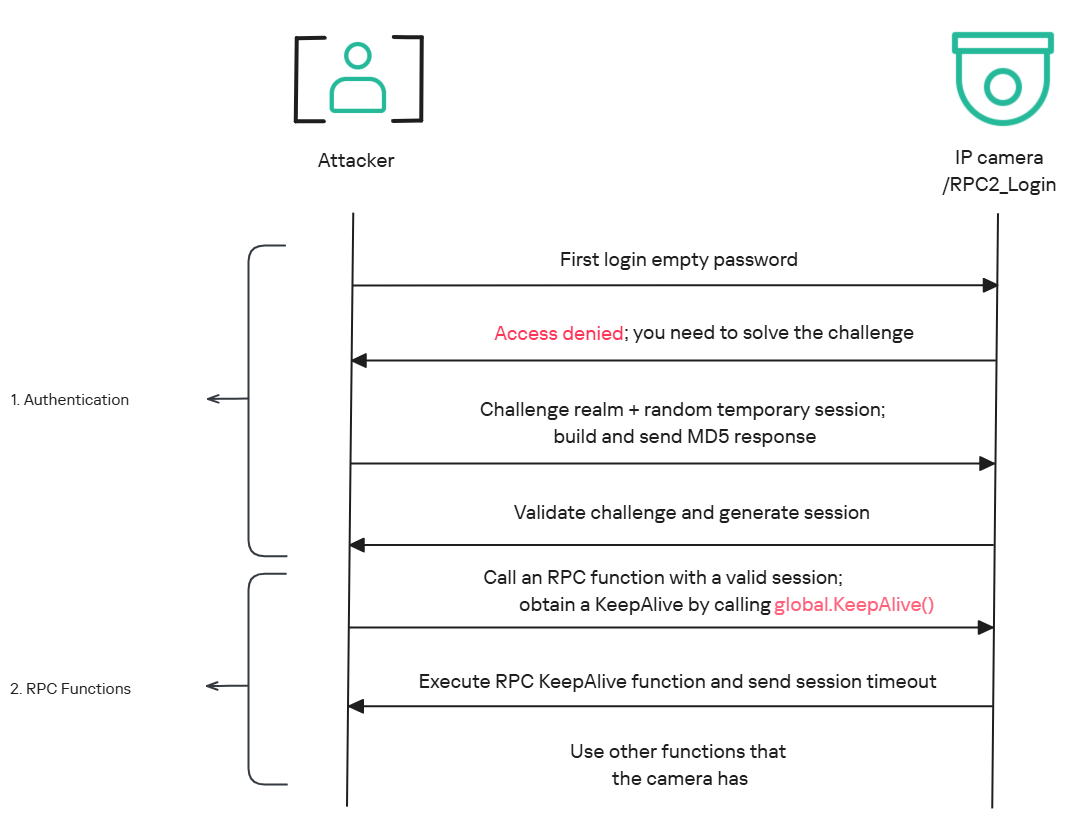
How authentication worksThe global.login RPC method handles authentication at the /RPC2_Login endpoint. First, the client, such as the mobile app or a custom script, sends the username and an empty password. The camera responds with an authentication challenge (a set of values to verify the password without transmitting it). This response returns a temporary session, the encryption type in the encryption field, a random value, and a realm (authentication scope). At this stage, a false response is normal and does not indicate a failed login, as the authentication process is not yet complete.
Next, the client calculates the response password from the authentication challenge. It first generates an MD5 (username:realm:original_password) hash as the base. It then calculates a second MD5 (username:random:first_md5) hash, where first_md5 is the result of the previous step. To complete the authentication, the client sends this final result back to /RPC2_Login in a second global.login call, passing the username, calculated password, and temporary session ID.
If the login is accepted, the camera returns true and a new, authenticated session. This session must be used for all subsequent RPC calls, including the camera’s other endpoints, for example, the one that reboots the device or those that expose sensitive information.
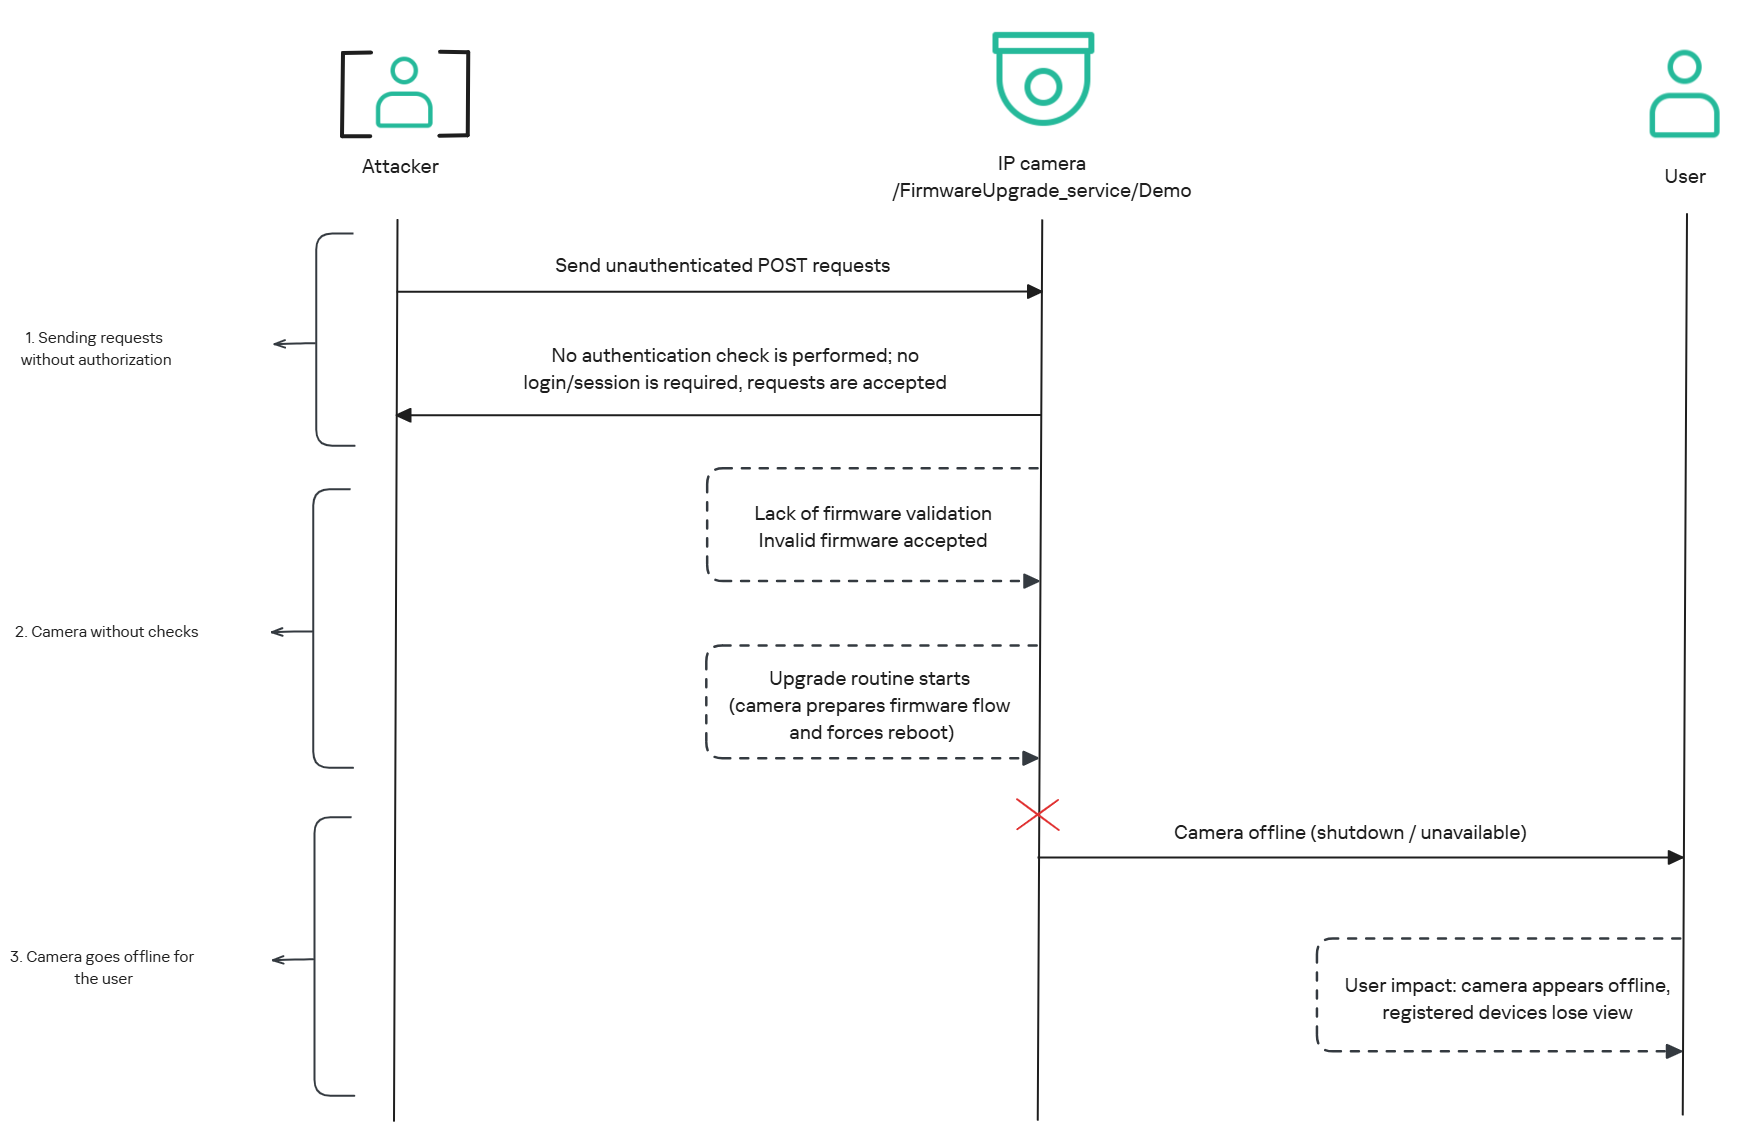
Affected endpointThe affected endpoint is the firmware upgrade route http://<ip_address>/firmwareUpgrade_service/Demo, which lacks authentication checks; furthermore, it fails to verify whether the firmware is actually valid before initiating the upgrade process. This creates a serious issue because the upgrade requires the camera to reboot, and that is precisely when the problem occurs: the camera enters reboot mode and eventually shuts down, appearing offline to the user and anyone who has the camera registered on their device.
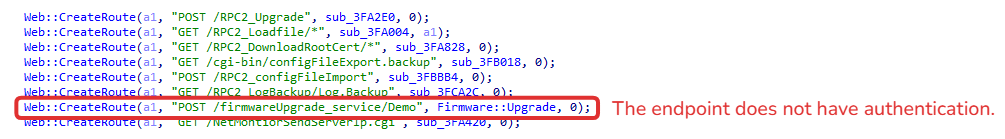
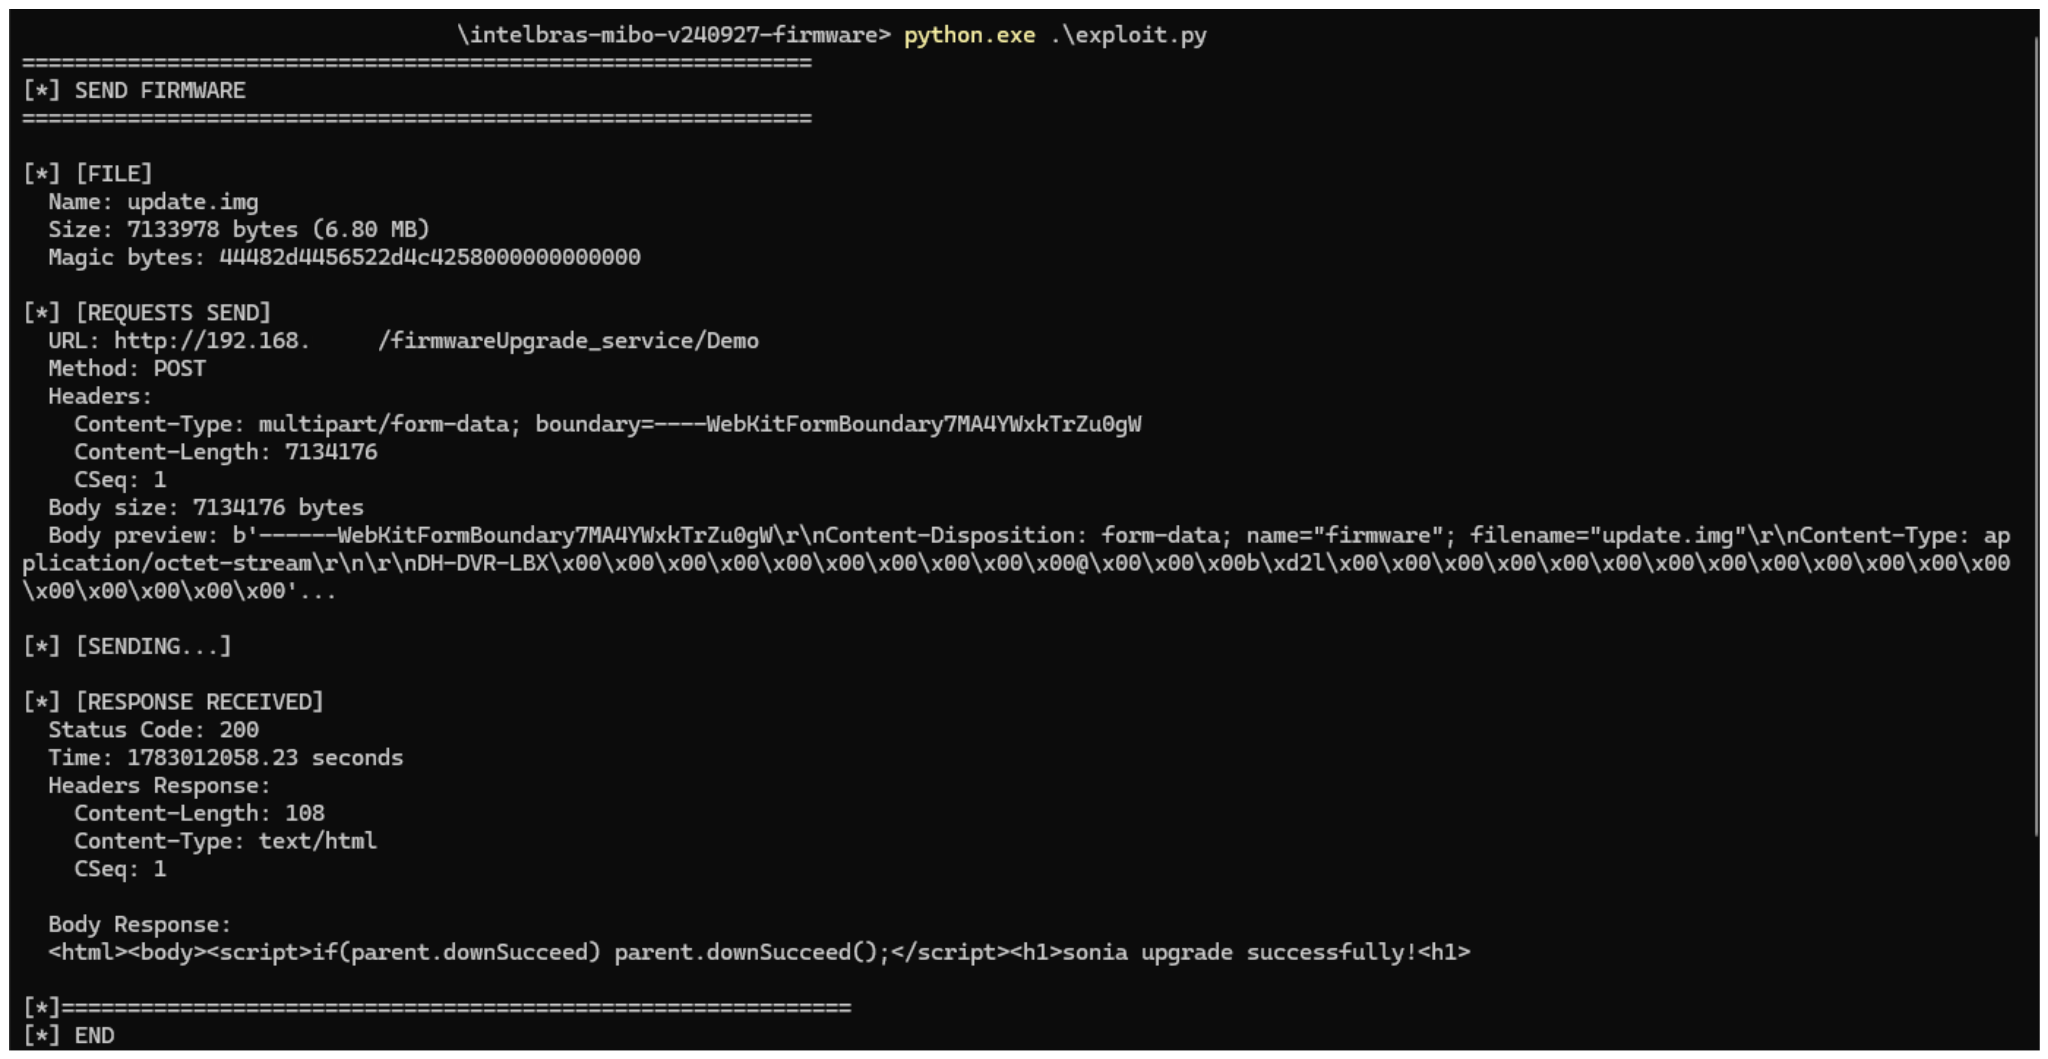
PoC: vulnerability exploitationNow that we have outlined how the vulnerability works, we will use a Python script on an iM3B-C camera to exploit it for demonstration purposes. The exploit contacts the camera’s endpoint to upload firmware. Below, we can see sonia creating the endpoint responsible for the firmware upgrade.
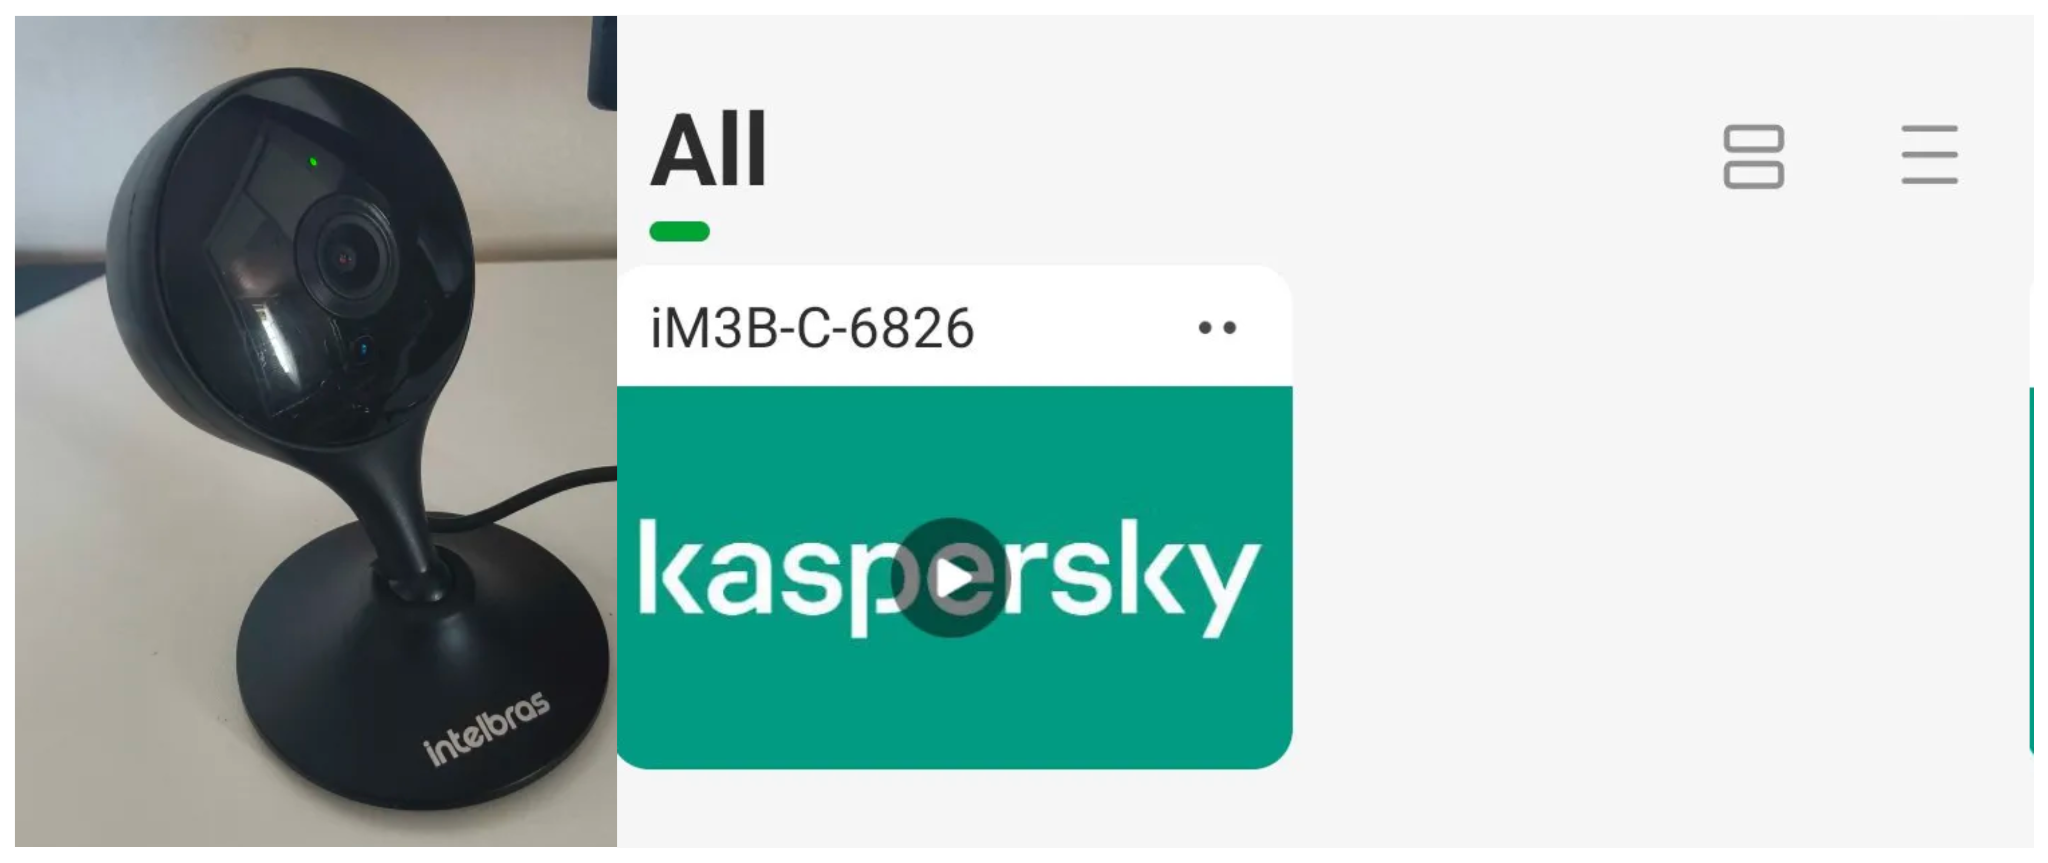
Next, the exploit will hit the endpoint and cause the camera to reboot. Consequently, mobile phones running the Intelbras app will lose connection with the registered device. Below, we can see the camera operating normally: the green light is on and the app is showing it is available for viewing.
The camera is online
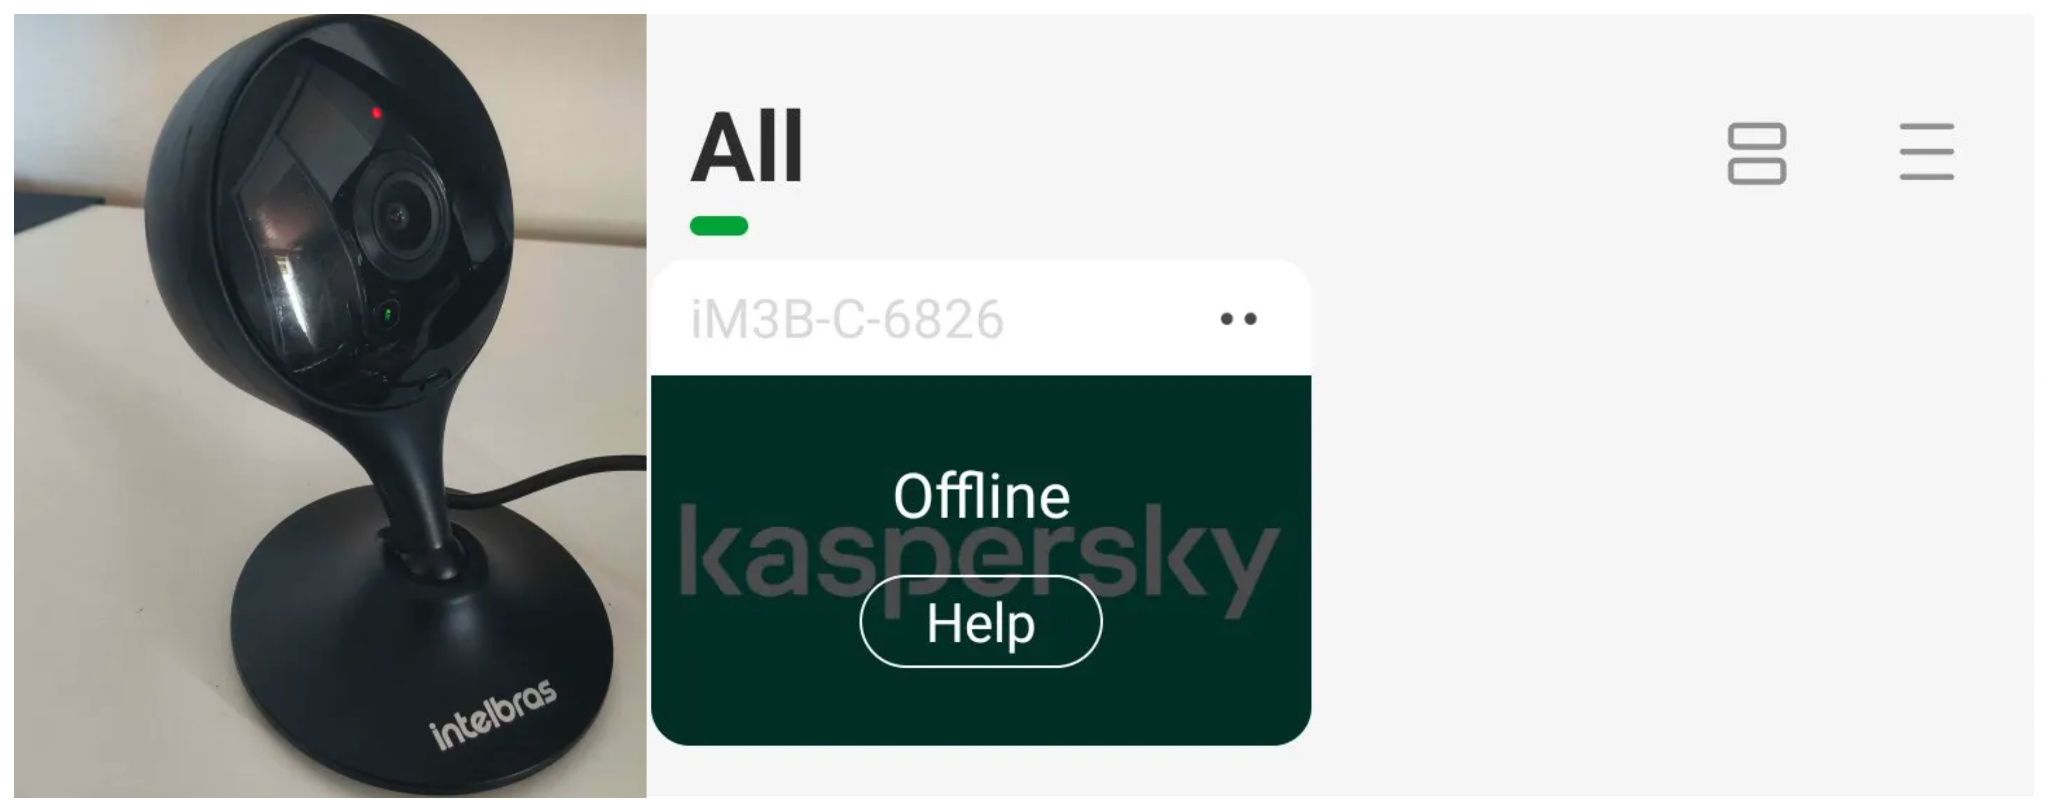
After the exploit executes, we can see the effects: the camera goes offline and loses connection to the registered devices.
The camera is offline
The exploit is quite simple: it sends an HTTP POST request with the firmware, which causes the camera to accept the request and initiate the reboot process. It does not matter whether the firmware is original; the reboot process will start regardless.
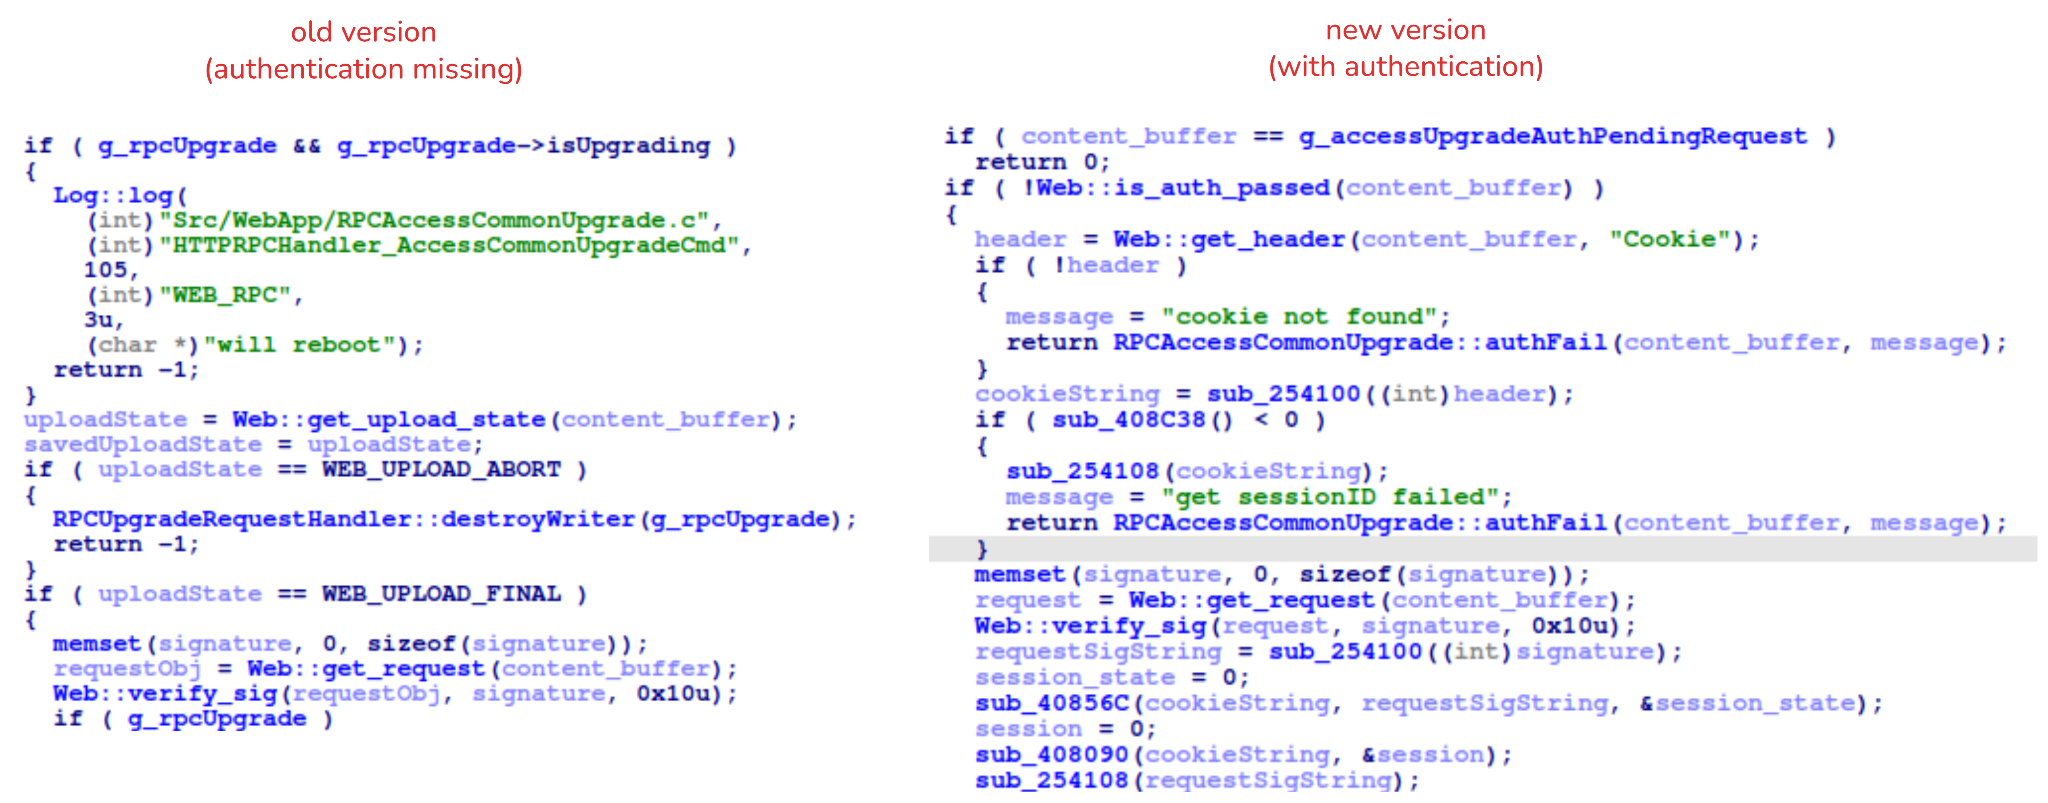
New firmware versionAfter we notified Intelbras about this flaw in the endpoint implementation, the company contacted the OEM vendor. As a result, a new firmware version was released that requires authentication to initiate an update through this endpoint.
Below, we can compare the new firmware, which validates cookies and session data, with the old firmware, which performed no authentication checks and proceeded directly to the update routine.
Real riskAn attacker can remotely trigger the camera firmware upgrade and reboot process without authenticating or supplying a valid firmware image. This may cause the device to go offline, which results in a denial-of-service condition preventing legitimate users from accessing live monitoring or managing the camera.
The potential impact is significant due to the number of affected users. The Intelbras Mibo Smart app, which the company provides to connect and manage the devices mentioned in this report, has over 4,000,000 downloads. Brazil represents the largest user base, followed by Paraguay, Ecuador, Colombia, Argentina, Chile, Peru, Bolivia, Uruguay, and Venezuela. As a result, exploitation of this issue affects a large number of users.
TakeawaysThis is a medium-severity vulnerability that Intelbras is already aware of. The issue has been addressed in a newer firmware release (R.260804 along with update instructions), which mitigates this attack vector. Because the vulnerability directly affects the availability and normal operation of the affected cameras, it is highly recommended that users verify the firmware version currently installed on their devices and update to the latest available version as soon as possible. Keeping the firmware up to date is an essential security practice, especially for internet-connected surveillance devices, as outdated versions may remain exposed to known vulnerabilities.
Kategorie: Hacking & Security, Viry a Červi
Otevřený headset Beyerdynamic MMX 130 wireless připojíte čtyřmi způsoby. Přes USB hraje a zároveň se nabíjí
Kategorie: IT News
The case for a full-circle Googlebook future
Put on your finest propeller-packin’ thinking caps, my fellow Android-appreciating animals — ’cause I’ve got a brain-bending bit of big-picture thinking about the future of Android and everything around it.
This pondering comes out of my ongoing time living with one of Google’s new Googlebook laptops — the beautifully built Lenovo Googlebook (provided to me as a short-term loaner for editorial assessment). Right now, the Googlebook experience itself is best summed up as an awkward start with plenty of potential. Android in a laptop environment just comes with an awful lot of asterisks, especially when you’re trying to use such a system for serious work. In many ways, it feels like a step down from the more polished and productivity-optimized Chromebook setup it’s ultimately designed to replace.
But while working on a Googlebook and using it as your primary computer still seems like a bit of a square-peg situation, I’ve been struck by one area where the Googlebook OS software at the center of the experience feels almost shockingly natural.
And that’s led me down a rabbit hole of pondering about the bigger-picture implications of this operating system and how it could, at least in theory, one day affect the rest of the Android ecosystem.
Lemme explain.
[Get original Googley insight in your inbox with my free Android Intelligence newsletter — one new thing to try every Friday.]
A Googlebook by any other nameSo, at its core, Googlebook OS is essentially Android — right? The software that powers Googlebooks is a specialized version of Android 17 designed to have some ChromeOS-like elements along with phone-connecting powers and a handful of feature additions that help it work better on a big screen.
And the more I use it, the more I keep coming back to a thought that I mentioned in passing in my initial Googlebook analysis — that this is what the Android tablet interface oughta be.
Think about it: Google has never really figured out how it wants an Android tablet to work — or if and how it even wants to promote and support the development of that not-quite-a-phone, not-quite-a-laptop form factor in the first place.
Early on, we saw a completely large-screen-optimized Android version called Honeycomb (a.k.a. Android 3.0 through 3.2), where Google gave us a dramatically reimagined interface designed to take full advantage of the tablet’s added screen space.
width="850" height="534" sizes="auto, (max-width: 850px) 100vw, 850px"> Android’s Honeycomb version featured an interface optimized for tablets — not so different in concept from Googlebook OS today.JR Raphael, Foundry
It wasn’t long, of course, before Google did its Google Thang™ and gave up on that idea — and that’s to say nothing of the even more ambitious Android tablet plan the company spent millions of dollars to develop and then never brought to fruition at all. By a certain point, it became obvious that Google was for all practical purposes giving up on Android tablets and that touch-oriented Chromebooks were effectively filling that role for informed buyers.
Fast-forward through a few other confusing short-lived pivots — the very brief return to tablet devotion with the ChromeOS-running Pixel Slate, the declaration of being done with tablets that followed, and the about-face and (once more) brief return to tablet devotion with the Pixel Tablet and its admirable but never fully realized and rapidly abandoned tablet-smart-display combo philosophy — and we’re back to a present now where Android tablets are mostly an afterthought, as far as Google and the underlying platform are concerned.
With all of that in mind, using a Googlebook is a bit of a revelation — when you think about the experience as less of a full-fledged laptop replacement and more of a potential future for a revamped Android tablet.
The Googlebook-Android tablet connectionConsider: In many ways, Googlebook OS picks up where Honeycomb left off 15 years ago — as far as the interface itself is concerned. It feels like a familiar Android environment, for anyone who’s used Android on a phone, but with some thoughtful touches that make it more sensible in that larger-screen setting. Everything from having the clock in the upper-left corner alongside a split-apart notification panel and Quick Settings area in the right to having the same desktop-style taskbar we’ve seen on recent Android foldables just feels right when you frame a Googlebook as a tablet and not, first and foremost, a work laptop.
width="1024" height="640" sizes="auto, (max-width: 1024px) 100vw, 1024px">The Googlebook desktop feels like a natural Android tablet interface.
JR Raphael / Foundry
Plain and simple, it’s Android — only optimized for a larger screen. And, thanks to its ChromeOS-inspired elements, it adds in the advantages of a less restrictive big-screen browser environment and smarter tools for interacting with your phone. The elements that feel awkward for a work laptop don’t matter as much in an Android tablet, which you’re more likely to use as a touch-centric supplement and companion to your workday computer and as a device where productivity is more of an occasional add-on as opposed to the primary purpose.
As a tablet interface, Googlebook OS gives you a souped-up version of the standard Android tablet setup that’d also be much more useful than a traditional tablet when you connect a keyboard. And without the expectation of it completely replacing your computer, it suddenly makes a lot of sense.
So riddle me this: With Android tablets being an afterthought now, anyway, what’s to stop Google from starting over — yes, again — and encouraging companies to create Googlebook tablets next?
It’d allow Google to rebrand and relaunch a category that’s always struggled to catch on and get past its not-so-exceptional early reputation. And for us, as users of these products, it’d give us some overdue options for a larger slate-like Android experience that’d work seamlessly with our phones, be pleasingly familiar and capable, and offer the unique advantage of having a mostly desktop-caliber browser for light work when such needs arise (with or without a keyboard connected) — all with the kind of timely and reliable software support promise any such product should provide.
And — oh, yes — there’s more.
Googlebook, Googlebook, everywhereHere’s the real mind-blowing next-step possibility to consider: If we do one day have Googlebook tablets — and the Googlebook OS software at the heart of them continues to evolve and become a core focus for Google as time moves on — how much of a leap would it be from there to see things streamlined and reaching a point where we also have Googlebook phones?
It brings me back, fittingly enough, to a question I posed over a decade ago — back when Android and ChromeOS were coming ever-closer together and it looked like that was the path Google was pursuing.
Consider this now, with the notion of Googlebook OS in the mix in place of ChromeOS:
If all Android apps can eventually run on ChromeOS — and if ChromeOS evolves to look more like Android while web apps and Android apps grow increasingly similar in design — would you notice the difference between a phone running Android and a phone running Chrome?
The specific platforms and concepts at the center of this have shifted since we last thought this through in 2015, but the idea itself is the same.
And, once more, there’s no better way to end this contemplation than by saying:
Welcome to the Matrix, my friends. Whoaaa.
Keep the creative thinking coming with my free Android Intelligence newsletter — one new thing to try every Friday and my experience-enhancing Android Notification Power-Pack as an instant welcome bonus.
Kategorie: Hacking & Security
Nefilim and Hive ransomware affiliate gets 70 months in prison
A Ukrainian national was sentenced to 70 months in prison for his role in ransomware attacks targeting hospitals, government entities, and high-revenue businesses worldwide between 2018 and 2021. [...]
Kategorie: Hacking & Security
Apple updates iMac, MacBook Pro, and Creator Studio
Apple’s second day of launches this week saw it follow its tempting iPad mini upgrade by pumping up the processor in two of its most popular Macs, even while it injected artificial intelligence into Creator Studio.
24 hours of portable pro performance: 14-in MacBook ProApple’s 14-inch MacBook Pro is popular but sits in a funny place in Apple’s notebook lineup, with the powerful and popular MacBook Air biting at its heels and the more performant and powerful (though not yet M6) MacBook Pro models sitting above.
We already know what the M6 chip is capable of, because it is already inside the Mac mini (which will be made in the US later this year). We know it delivers better single-core scores on Geekbench than the 10-core M5 MacBook Pro. We also know it beats that last MBP in multi-core. Now that same chip is available in a 14-inch MacBook Pro — a really promising dose of power and performance in a highly portable pro Mac that now packs a mighty 24-hour battery life.
The chip gives you a 12-core CPU, a 12-core GPU with Neural Accelerators in each core, a dual 16-core Neural Engine, and faster (16GB, upgradable up to 32GB) unified memory. What that means is power. And what that means is productivity — 30% faster graphics compared to last year’s model.
For those upgrading from M1, the performance gains are even more significant, with up to 11x faster graphics and up to 13x faster AI performance. The idea is that you’ll pick up your highly portable pro portable and take it anywhere you need it to be.
AppleWhat’s new in Apple’s new portable pro laptop other than the processor?
- Networking has been enhanced with Wi-Fi 7 and Bluetooth 6.
- It will support up to two external 6K displays.
- Liquid Retina XDR display with up to 1,600 nits of peak brightness.
- 12-megapixel Center Stage camera.
- Support for fast charging.
- HDMI, MagSafe 3, three Thunderbolt 4 slots, SDXC card reader.
- Headphone jack.
Available in Space Black and Silver.
Pre-order from October 28, in stores November 6.
Apple New colors, new processors, the new M6 iMacYou don’t even need me to say it anymore, but the introduction of M6 chips inside the iMac makes the all-in-one desktop even more powerful and performant. This tops out a 12-core CPU, 12-core GPU, and Dual 16-core Neural Engine.
Those fast processors combined with the fast, 170GB/s memory bandwidth means you’ll get twice the graphics performance of the M4 iMac. The Mac ships with 16GB of unified memory, but you can upgrade up to 32GB if you like spending money.
Inevitably, the new iMac is faster for, well, everything. You’ll be hitting pro performance comparisons all over again as Apple silicon continues to redefine expectations across the industry, putting pro performance in reach of most people. It’s all about AI at Apple at the moment, so expect 12 times faster performance in some tasks compared to the M1, Apple said.
Some specifications:
- The iMac retains the 4.5K 24-inch Retina display, 500 nits, and P3 wide color of before.
- It brings Wi-Fi 7, Bluetooth 6, and 2.5Gb Ethernet.
- It will support up to two external 6K displays.
- Up to four Thunderbolt 4 ports.
- 12MP Center Stage camera.
- 2x faster SSD read and write.
- Touch ID.
- Available in blue, green, pink, yellow, purple, orange, and silver.
The new iMac is on pre-sale from October 28 and in stores from November 6. It costs $1,499 with a 10-core CPU, 10-core GPU, and 16GB of RAM, or $1,699 with a 12-core CPU and 12-core GPU (16GB of RAM).
Apple Apple leans into AI for creative customersOf course, once you have put together the world’s leading mass-market AI ecosystem, you have to do something to show that power off. Apple has done this with a selection of interesting updates to its Creator Studio suite of creative tools. They’ll ship in November.
- Final Cut Pro for Mac now includes a large MotionVFX collection consisting of thousands of visual effects, transitions, and motion graphics tools and built-in Pixelmator Pro editing. Apple has also filled out its Content Hub with a bunch of new video assets that can be snagged from inside Final Cut Pro.
- Logic Pro gains AI, an enhanced Stem Splitter that now separates drums, a redesigned sound Browser, and a new intelligent assistant powered by a combination of Apple-built models and OpenAI.
- Pixelmator Pro introduces Generate Fill, which lets creators transform selected areas of an image using natural language.
- Keynote, Pages, and Numbers introduce new AI features in beta, including assistants that understand document context and new Model Context Protocol (MCP) support for workflow automation. They add stock video in the Content Hub, new premium themes and templates, and that intelligent assistant powered by a combination of Apple-built models and OpenAI.
Now please subscribe to my daily, human-curated Apple-related news headline feed at The Core, or follow me on BlueSky, LinkedIn, or Mastodon.
Kategorie: Hacking & Security
PPF opět expanduje v telekomunikacích. V portfoliu má novou firmu, založila ji s méně známým partnerem
Skupina PPF přes Cetin zakládá novou firmu Cetin Digital, která se zaměří na software a IT služby pro telekomunikace. • Cetin v ní drží 51 procent, zbytek patří firmě DataLite Holding, která vyvíjí systém tSM pro řízení sítí a zákazníků operátorů. • Mezi zákazníky systému patří i konkurence ...
Kategorie: IT News
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report.
The exploits were built in the lab after the model was prompted, not seen in any real attack, and Anthropic reported every flaw to the vendor first, so all of them are already patched. One proof of Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Nejkrásnější PC skříň v akci. Fractal North s dřevěným čelem zlevnila pod tři tisíce
Fractal North patří mezi nejhezčí počítačové skříně na trhu. • Bílá varianta s dřevěnými lamelami vpředu zlevnila na 2919 Kč. • Nabízí kvalitní konstrukci, snadnou montáž a dobré možnosti chlazení.
Kategorie: IT News
- « první
- ‹ předchozí
- …
- 18
- 19
- 20
- 21
- 22
- 23
- 24
- 25
- 26
- …
- následující ›
- poslední »